Self-host Zed Attack Proxy (ZAP)
v2.17.0Web app security scanner and intercepting proxy
- Stars
- 16 199
- Ports
- 8080 (Default ZAP port checked by the container healthcheck; with Webswing the browser UI is served at http://localhost:8080/zap), 8090 (ZAP's proxy/API port used by the default daemon options and for browser proxying)
ghcr.io/zaproxy/zaproxy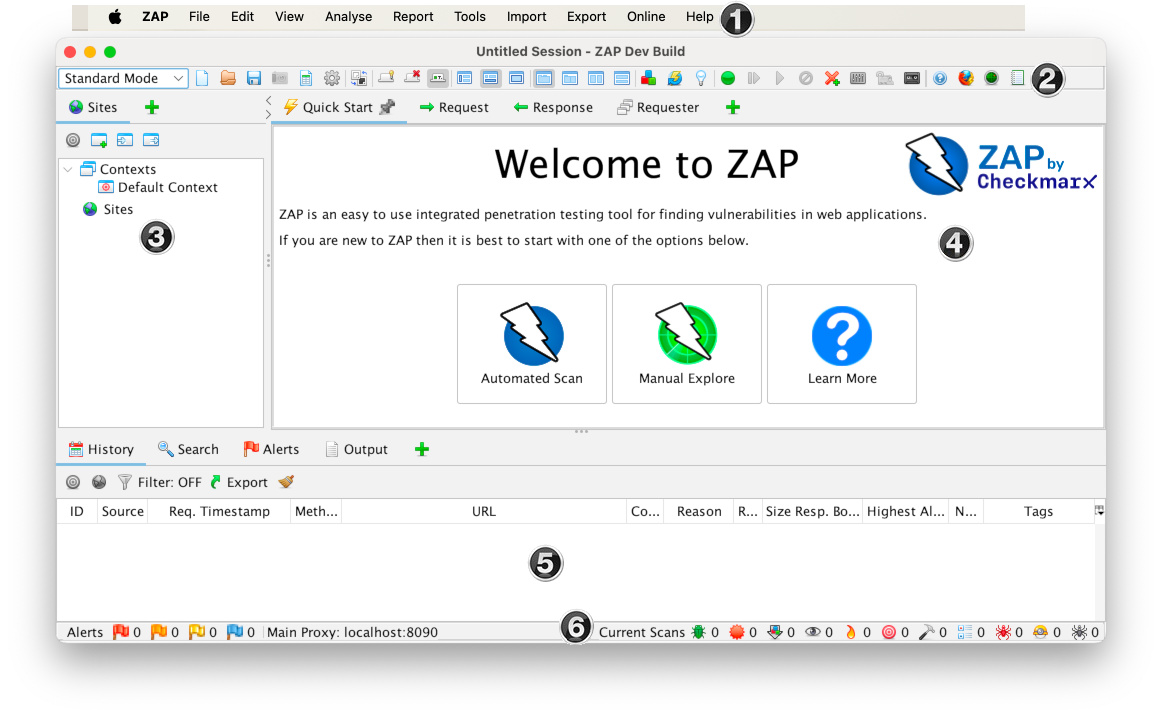

What is Zed Attack Proxy (ZAP)?
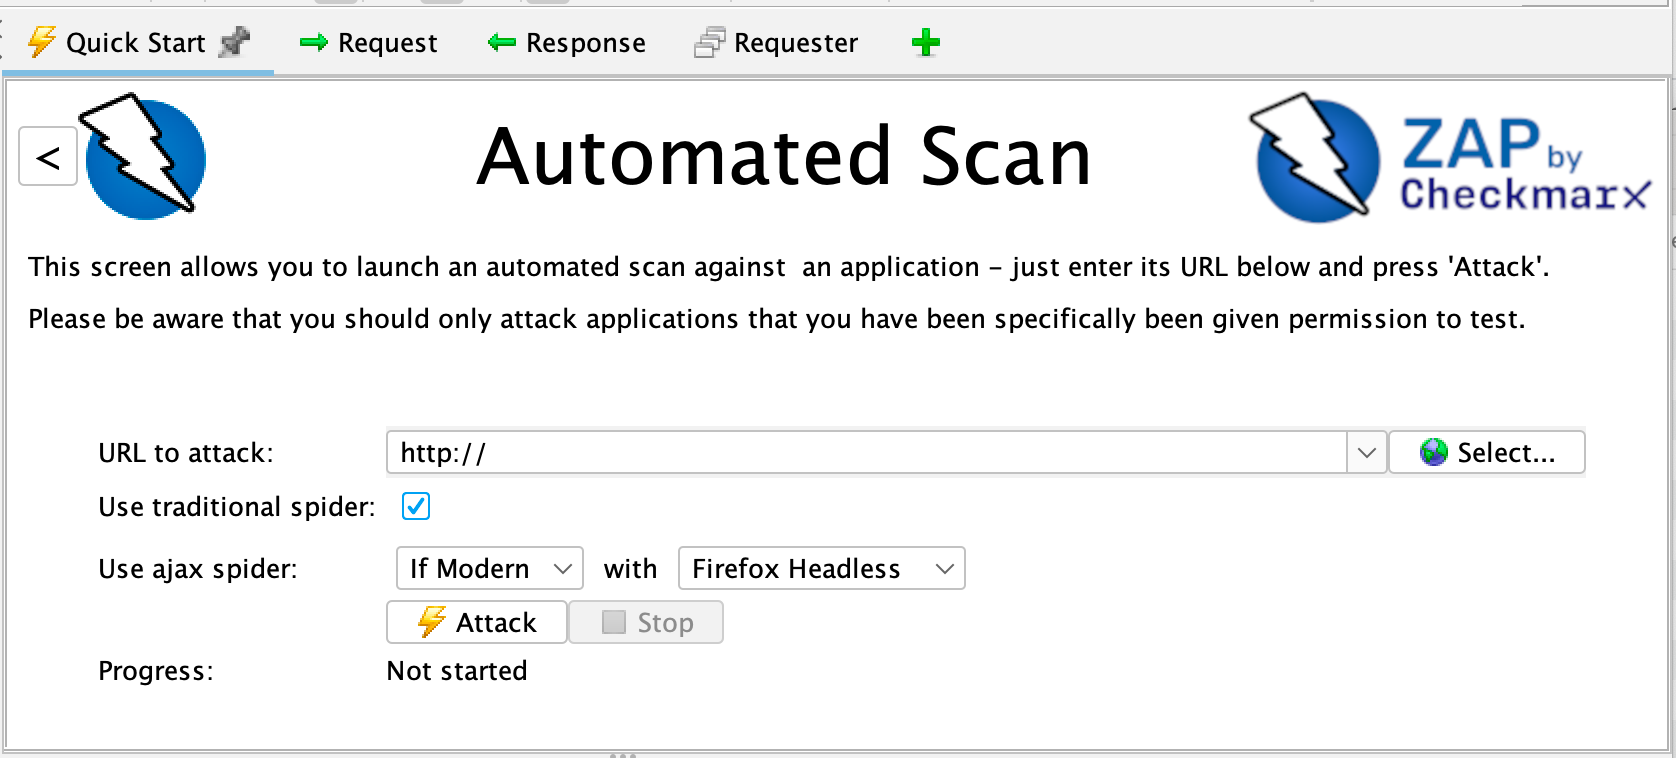
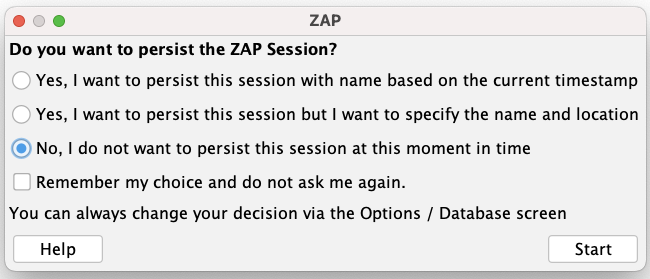
ZAP (Zed Attack Proxy) is a widely used dynamic security testing tool for web applications, released free of charge under Apache-2.0 and branded as ZAP by Checkmarx. At its heart it works as a proxy placed between your browser and the app under test, so traffic can be inspected and edited on the fly while scan rules hunt for problems. Every request and response that flows through is checked passively, and an active scanner can then attack whatever the crawl uncovered - pages, features and parameters alike. Three crawlers are available: a fast HTML spider, a browser-driven Client spider better suited to modern JavaScript apps, and the older AJAX spider; the Quick Start tab combines crawling and scanning into one automated attack run. A separate API scan mode targets OpenAPI, SOAP or GraphQL definitions, read from a spec file or pulled over HTTP.
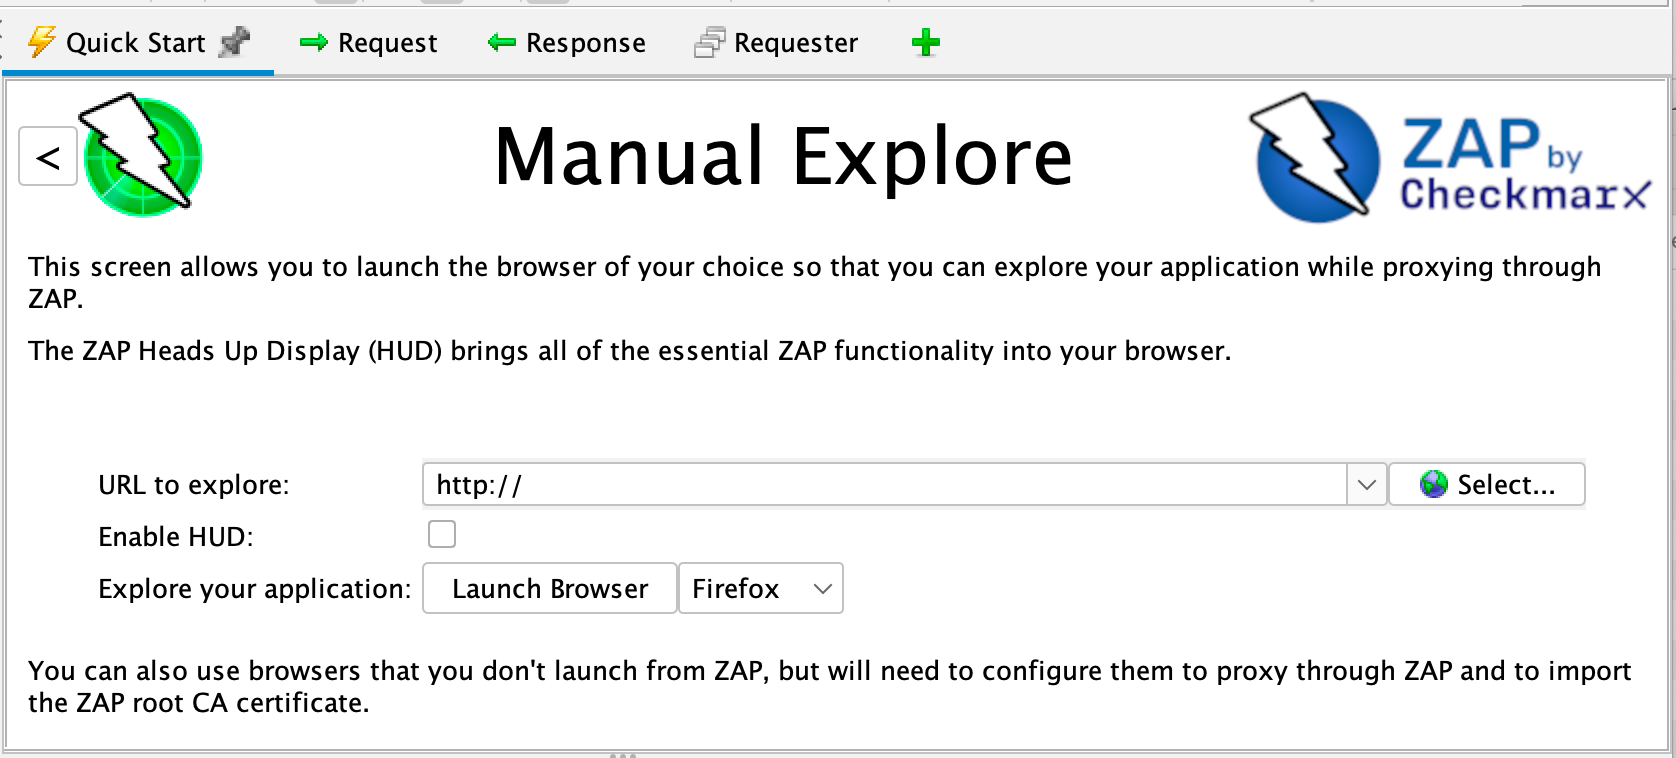
Automation is a first-class use case. YAML plans drive complete checks through the Automation Framework, ZAP can run headless as a daemon controlled through its API, and the container images ship baseline, full and API scan scripts that official GitHub Actions wrap; findings can be exported as HTML, Markdown, XML or JSON reports. Add-ons from the free marketplace bolt onto the plugin-based desktop client, and the Heads Up Display surfaces ZAP's information inside the browser during manual exploration.
Deployment options are broad: the Swing desktop runs natively on Windows, Linux and macOS, the Webswing Docker mode serves that same UI in a browser, and containers fit straight into pipelines. Windows and Linux builds need Java 17 or higher, whereas the macOS installer ships Java 17 bundled and the images need no local Java at all. Two caveats worth knowing: ZAP releases are currently unsigned, which triggers antivirus and OS warnings, and active scanning is a genuine attack, so use it only against systems you are allowed to test.
Zed Attack Proxy (ZAP) alternatives
 WazuhSelf-hosted, open-source XDR and SIEM platform: endpoint agents plus server, indexer and dashboard for log analysis, file integrity, vulnerabilities and compliance.CompareWazuh with Zed Attack Proxy (ZAP)
 web-checkOpen-source, self-hosted OSINT tool that runs 44 checks on any URL - DNS, TLS, headers, ports, CVEs, trackers - through a web UI or plain API.Compareweb-check with Zed Attack Proxy (ZAP)
 crowdsecSelf-hosted, open-source intrusion detection and web-app firewall that reads your logs, bans abusive IPs, and shares a crowdsourced blocklist across users.Comparecrowdsec with Zed Attack Proxy (ZAP)
 pwnflowPwnflow is a self-hosted, open-source mind-mapping platform for cybersecurity professionals to visualize and track security testing methodologies with AI assistance.Comparepwnflow with Zed Attack Proxy (ZAP)
 ThreatMapperSelf-hosted, open-source CNAPP: Deepfence ThreatMapper scans cloud, Kubernetes and container workloads for vulnerabilities, exposed secrets and CIS compliance gaps.CompareThreatMapper with Zed Attack Proxy (ZAP)
 Deadend CLIDeadend CLI is a self-hosted, open-source CLI for autonomous web app pentesting using feedback-driven AI with any LiteLLM model, achieving ~80% on XBOW.CompareDeadend CLI with Zed Attack Proxy (ZAP)
 spiderfootSpiderFoot automates OSINT for threat intelligence and mapping your attack surface.Comparespiderfoot with Zed Attack Proxy (ZAP)
 ReconnerSelf-hosted bug-bounty platform for attack surface intelligence and verification-first DAST with continuous monitoring, asset discovery, and evidence-based findings.CompareReconner with Zed Attack Proxy (ZAP)
Should you self-host Zed Attack Proxy (ZAP)?
Zed Attack Proxy (ZAP) scores 80/100 on selfhost.directory (how scoring works) and ranks #3 of 78 in Security. It has 16 199 GitHub stars, +274 in the last 30 days.
It shipped 34 stable releases in the past year. The latest, w2026-11-11, came out on 11 November 2026. New versions land roughly every 7 days.
Setup is easy: most people get it running in one sitting. An official Docker image is available. It is Apache-2.0-licensed and written mostly in Java.
Its closest alternative on selfhost.directory is CyberChef (83/100, 36 419 stars). It scores higher overall, so compare the two before you pick. See Zed Attack Proxy (ZAP) vs CyberChef side by side.
Features
- Active scanning
- Add-on marketplace / plugin architecture
- API scanning
- Authenticated scans
- Automation framework (YAML plans)
- Desktop GUI in a browser
- Heads Up Display (HUD)
- Intercepting proxy
- Packaged CI scans
- Passive scanning
- REST API and daemon/headless mode
- Safe mode
- Scan reports in several formats
- Web crawling with multiple spiders
Zed Attack Proxy (ZAP) README


More in Security
 zitadelSelf-hosted open-source IAM stack: password, passkey and second-factor logins, external IdP brokering, OIDC/SAML tokens, on PostgreSQL with Docker or Kubernetes.
 εxodusεxodus is a self-hosted, open-source platform that analyzes Android apps to detect embedded trackers, analytics, and advertising libraries.
 2faSelf-hosted, open-source TOTP/HOTP key manager that runs as a Cloudflare Worker: AES-GCM encrypted storage, QR import, PWA offline use, backups to WebDAV/S3/OneDrive.
 acme-companionSelf-hosted Docker container automating Let's Encrypt SSL for nginx-proxy. Supports HTTP-01/DNS-01 challenges, multi-domain SAN certificates, and wildcards via DNS.
 AdGuard HomeSelf-hosted open-source DNS server blocking ads/trackers network-wide. Supports encrypted DNS, parental controls, safe search, per-client config, DHCP.
 AdrianAdrian is an open-source runtime security tool that monitors AI agent reasoning and actions, spotting injected prompts and unsafe tool calls before they execute.
 Advanced Camera CardA comprehensive camera card for Home Assistant
 AgentSafeSelf-hosted gateway intercepting AI agent HTTP actions, asking Decionis for authorization, forwarding only approved requests with signed evidence.
 aisecuritygatewaySelf-hosted AI gateway that redacts PII, blocks prompt injection, and routes to 8 LLM providers via OpenAI-compatible API.
 AiSOCSelf-hosted, open-source AI SOC with 2,535 detection rules and agents that record every step in an auditable ledger. MIT licensed, no API keys needed.
 AlarmoEasy to use alarm system integration for Home Assistant
 altchaSelf-hosted, open-source CAPTCHA alternative that swaps image puzzles for a silent proof-of-work widget plus MIT-licensed server libraries for 10+ languages.
0 comments