Self-host tesserae
v0.480.0Composable dashboards for your e-ink wall panels
curl -fsSL https://raw.githubusercontent.com/dmellok/tesserae/main/install.sh | bash- Stars
- 973
- Ports
- 8765 (Web UI + API), 1883 (Built-in MQTT broker (optional, enabled in Settings))
ghcr.io/dmellok/tesserae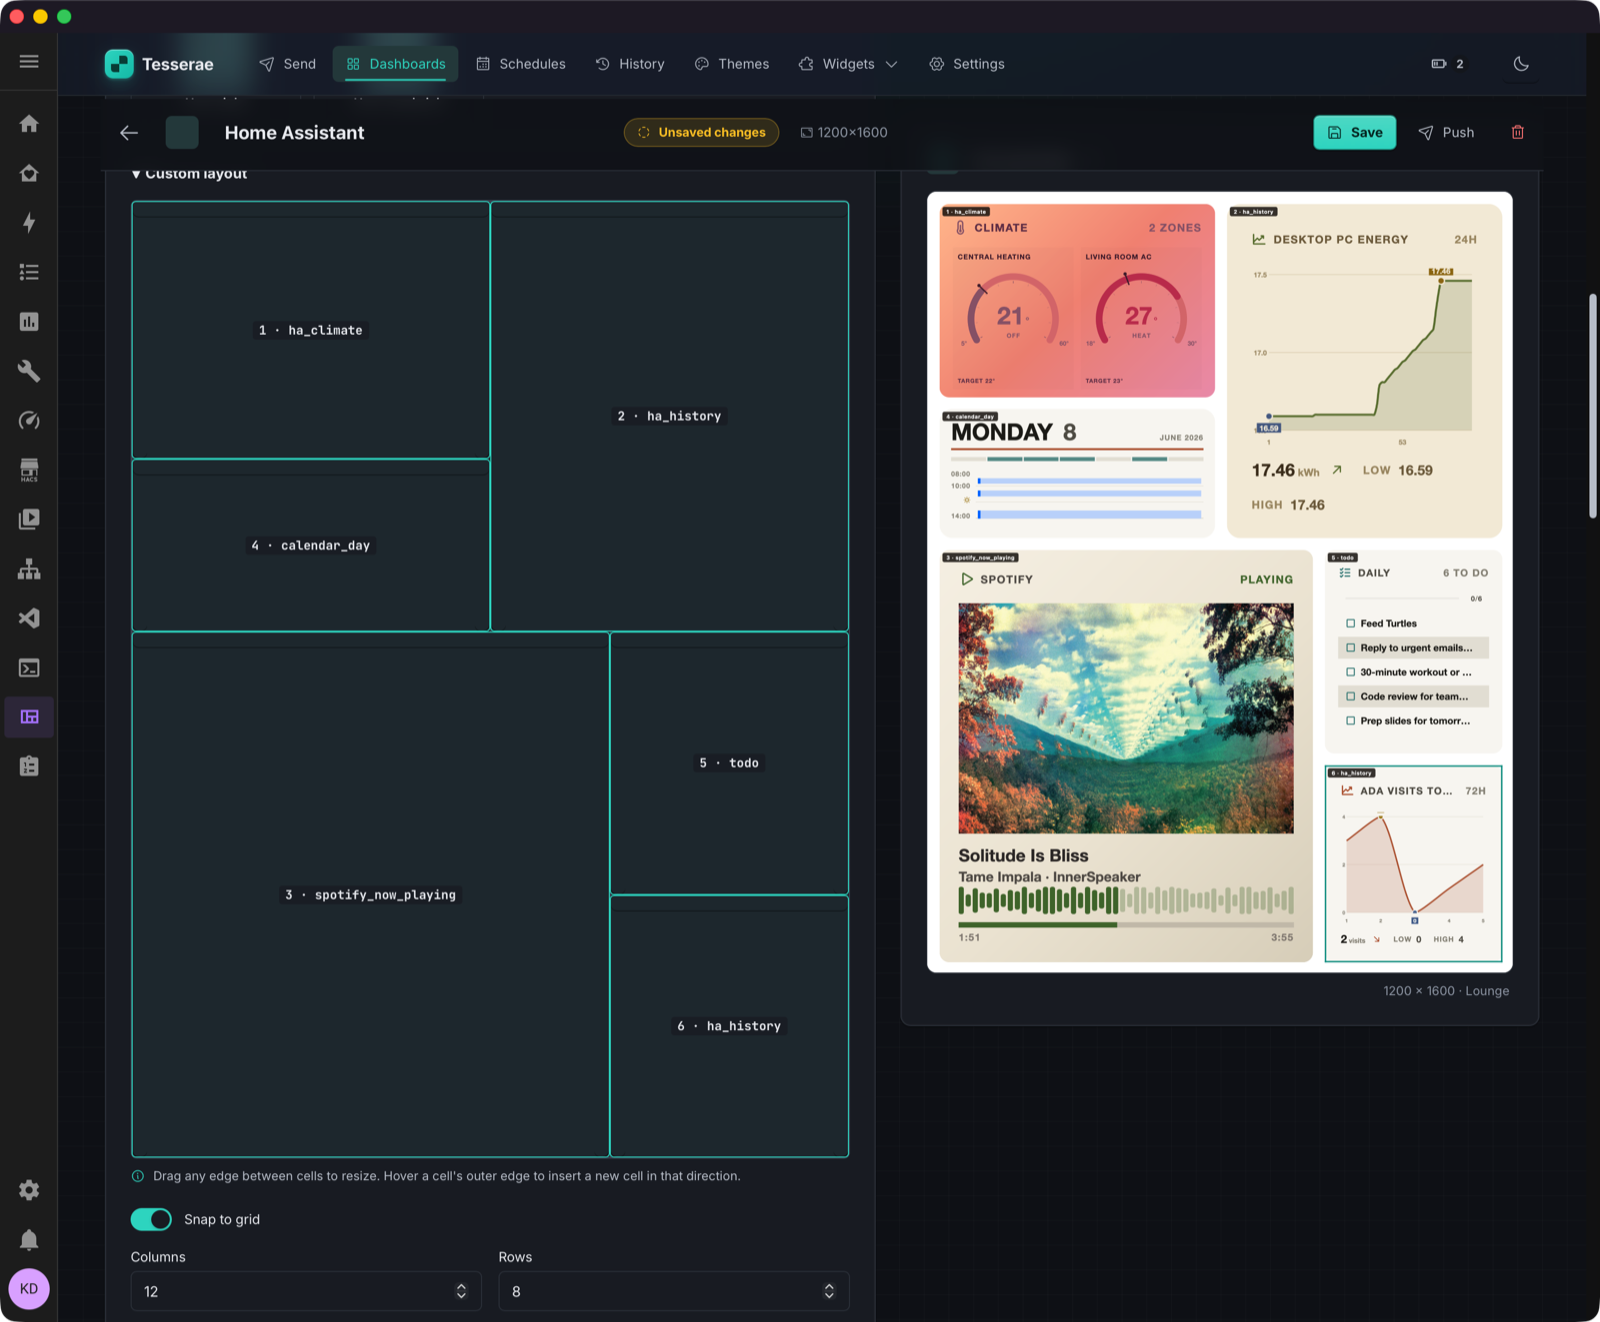
What is tesserae?
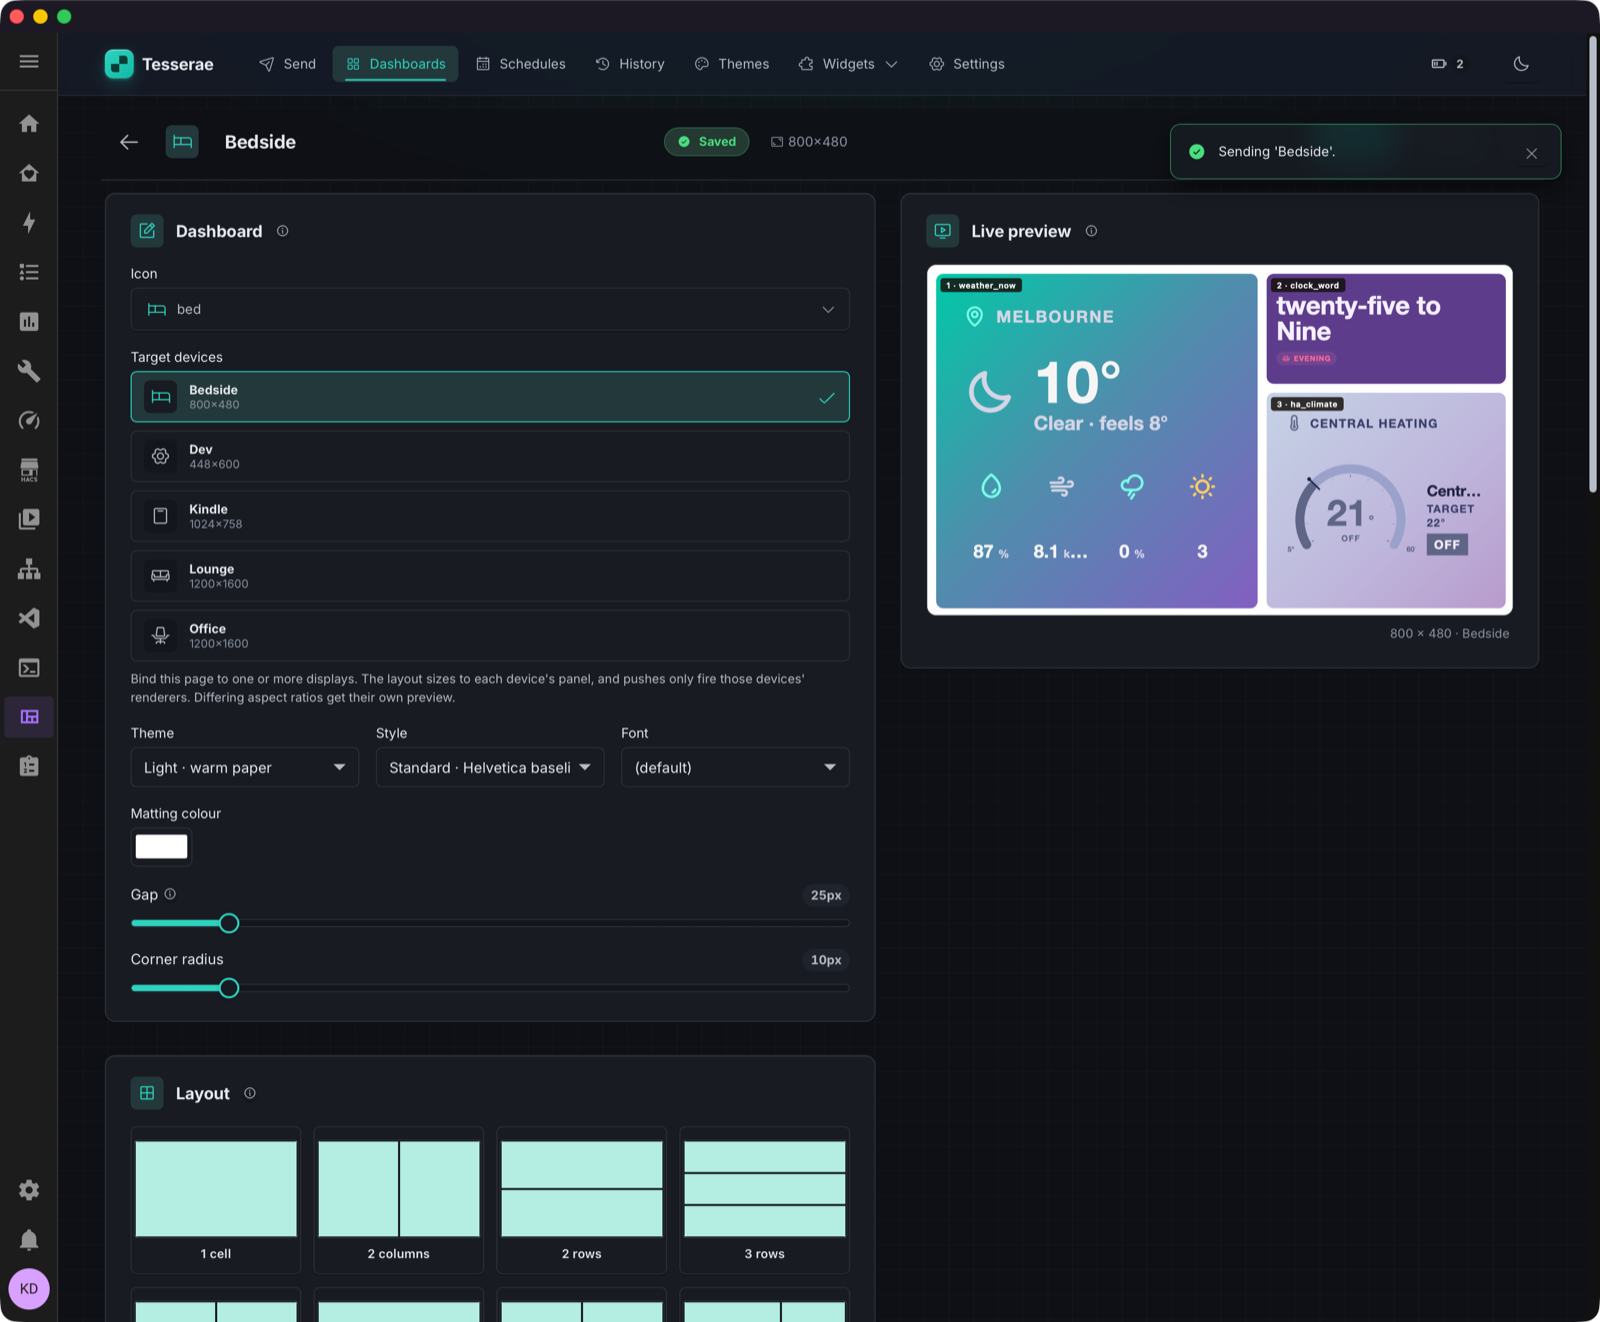
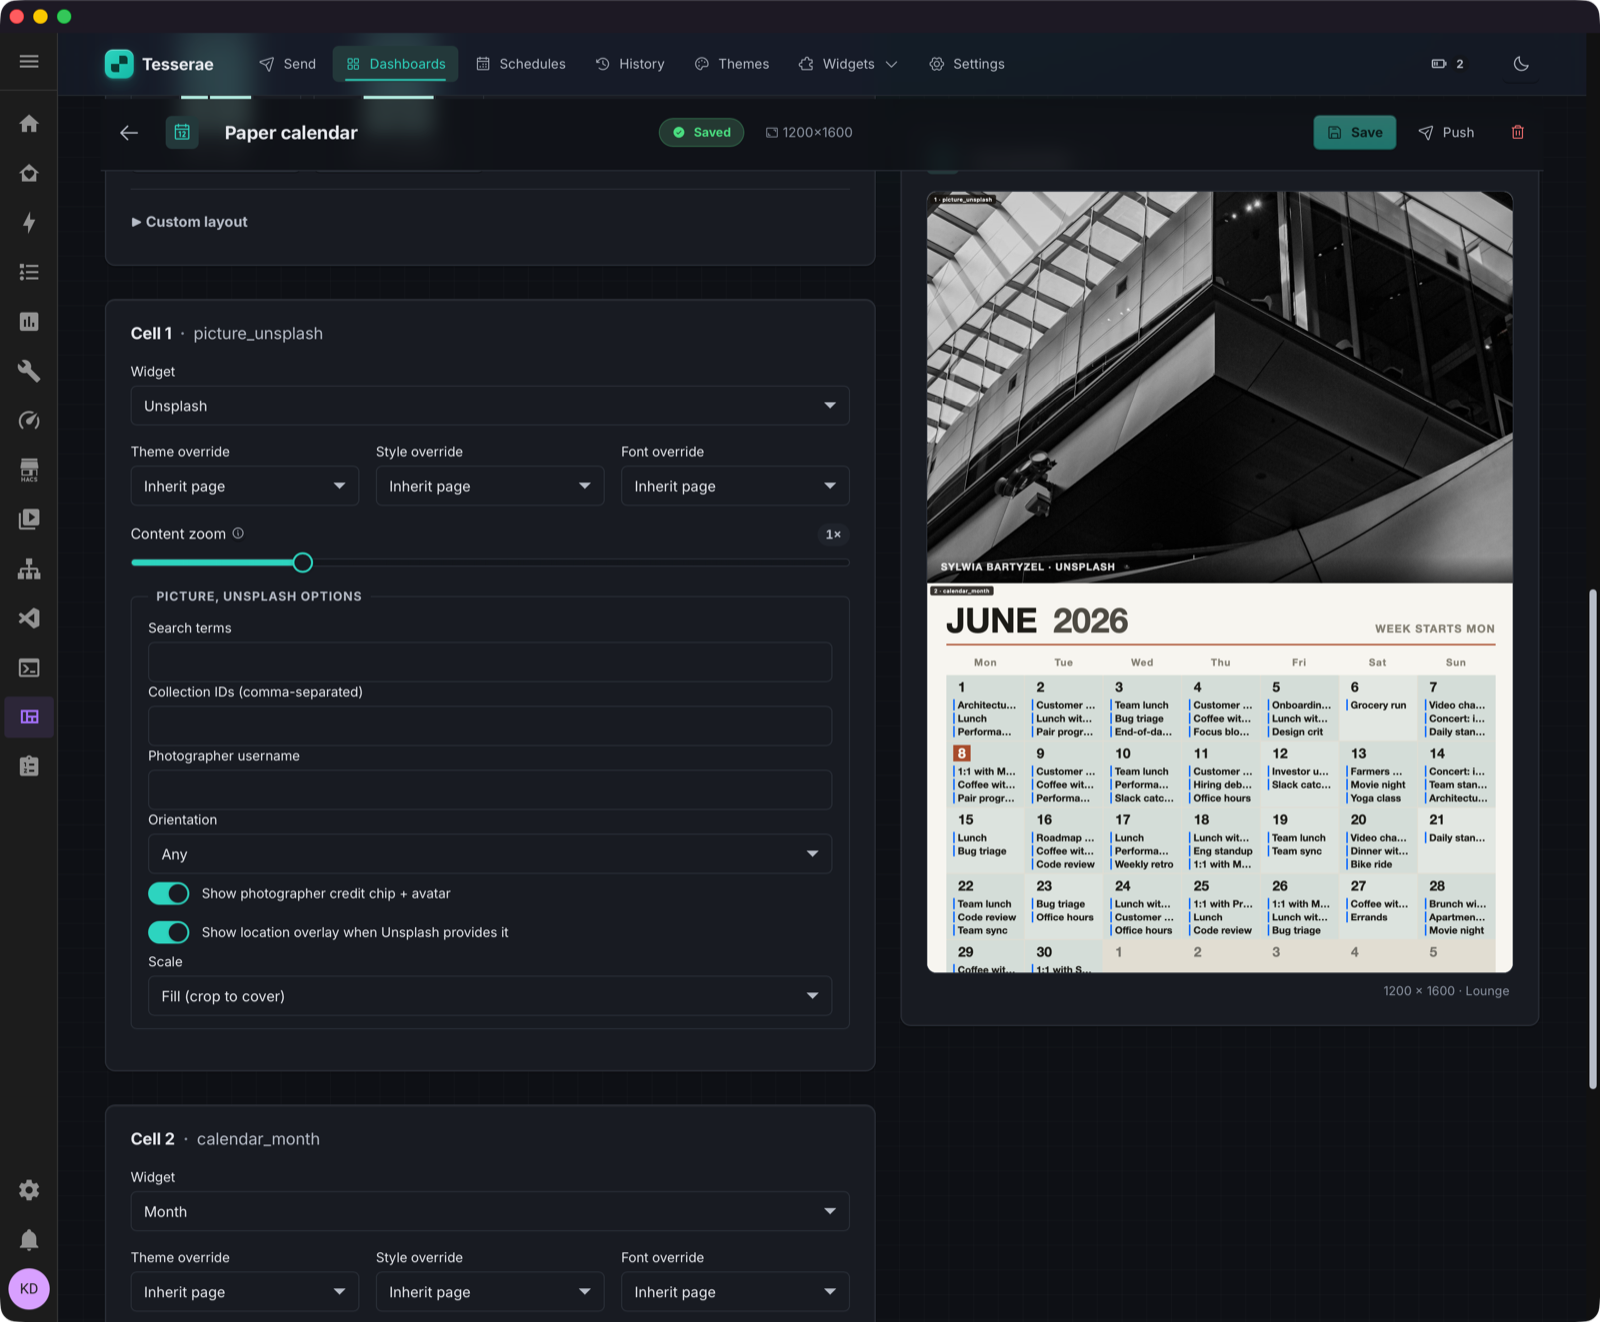
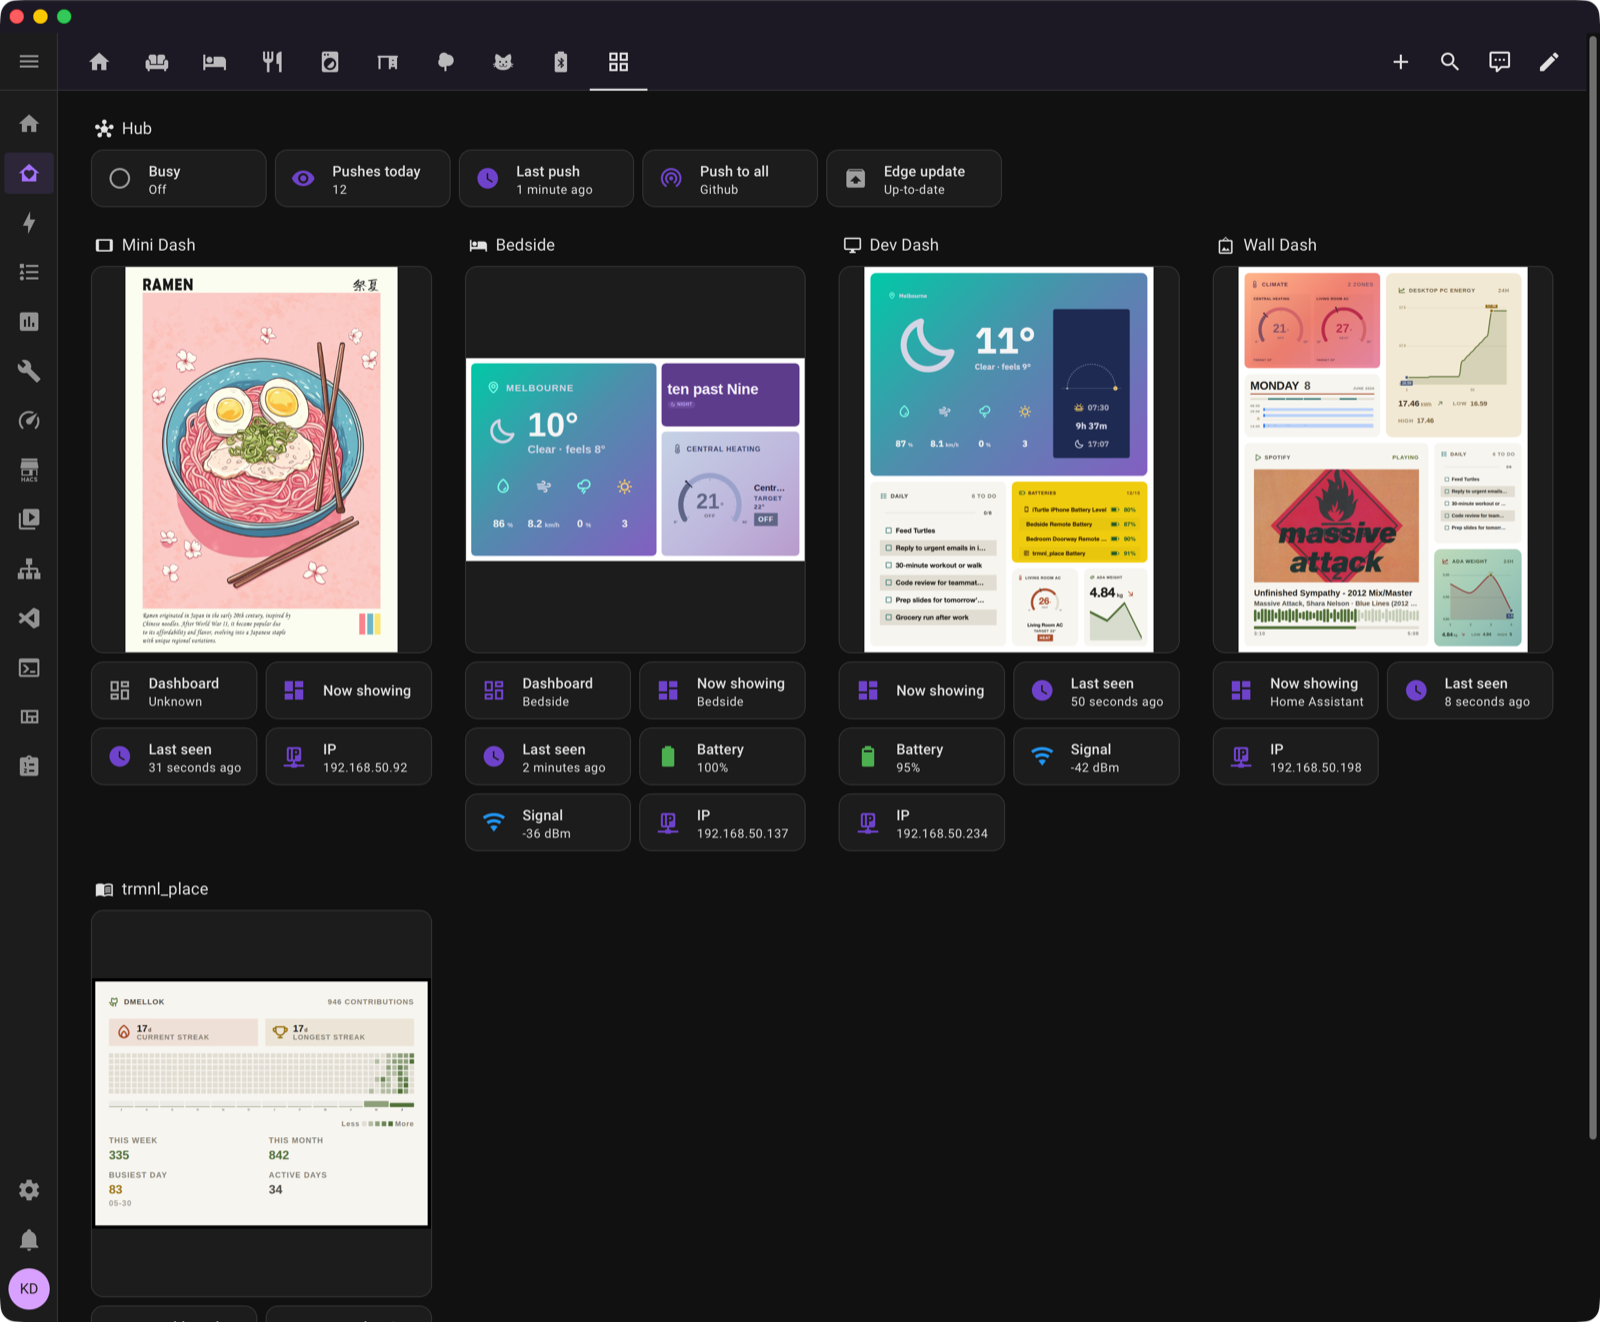
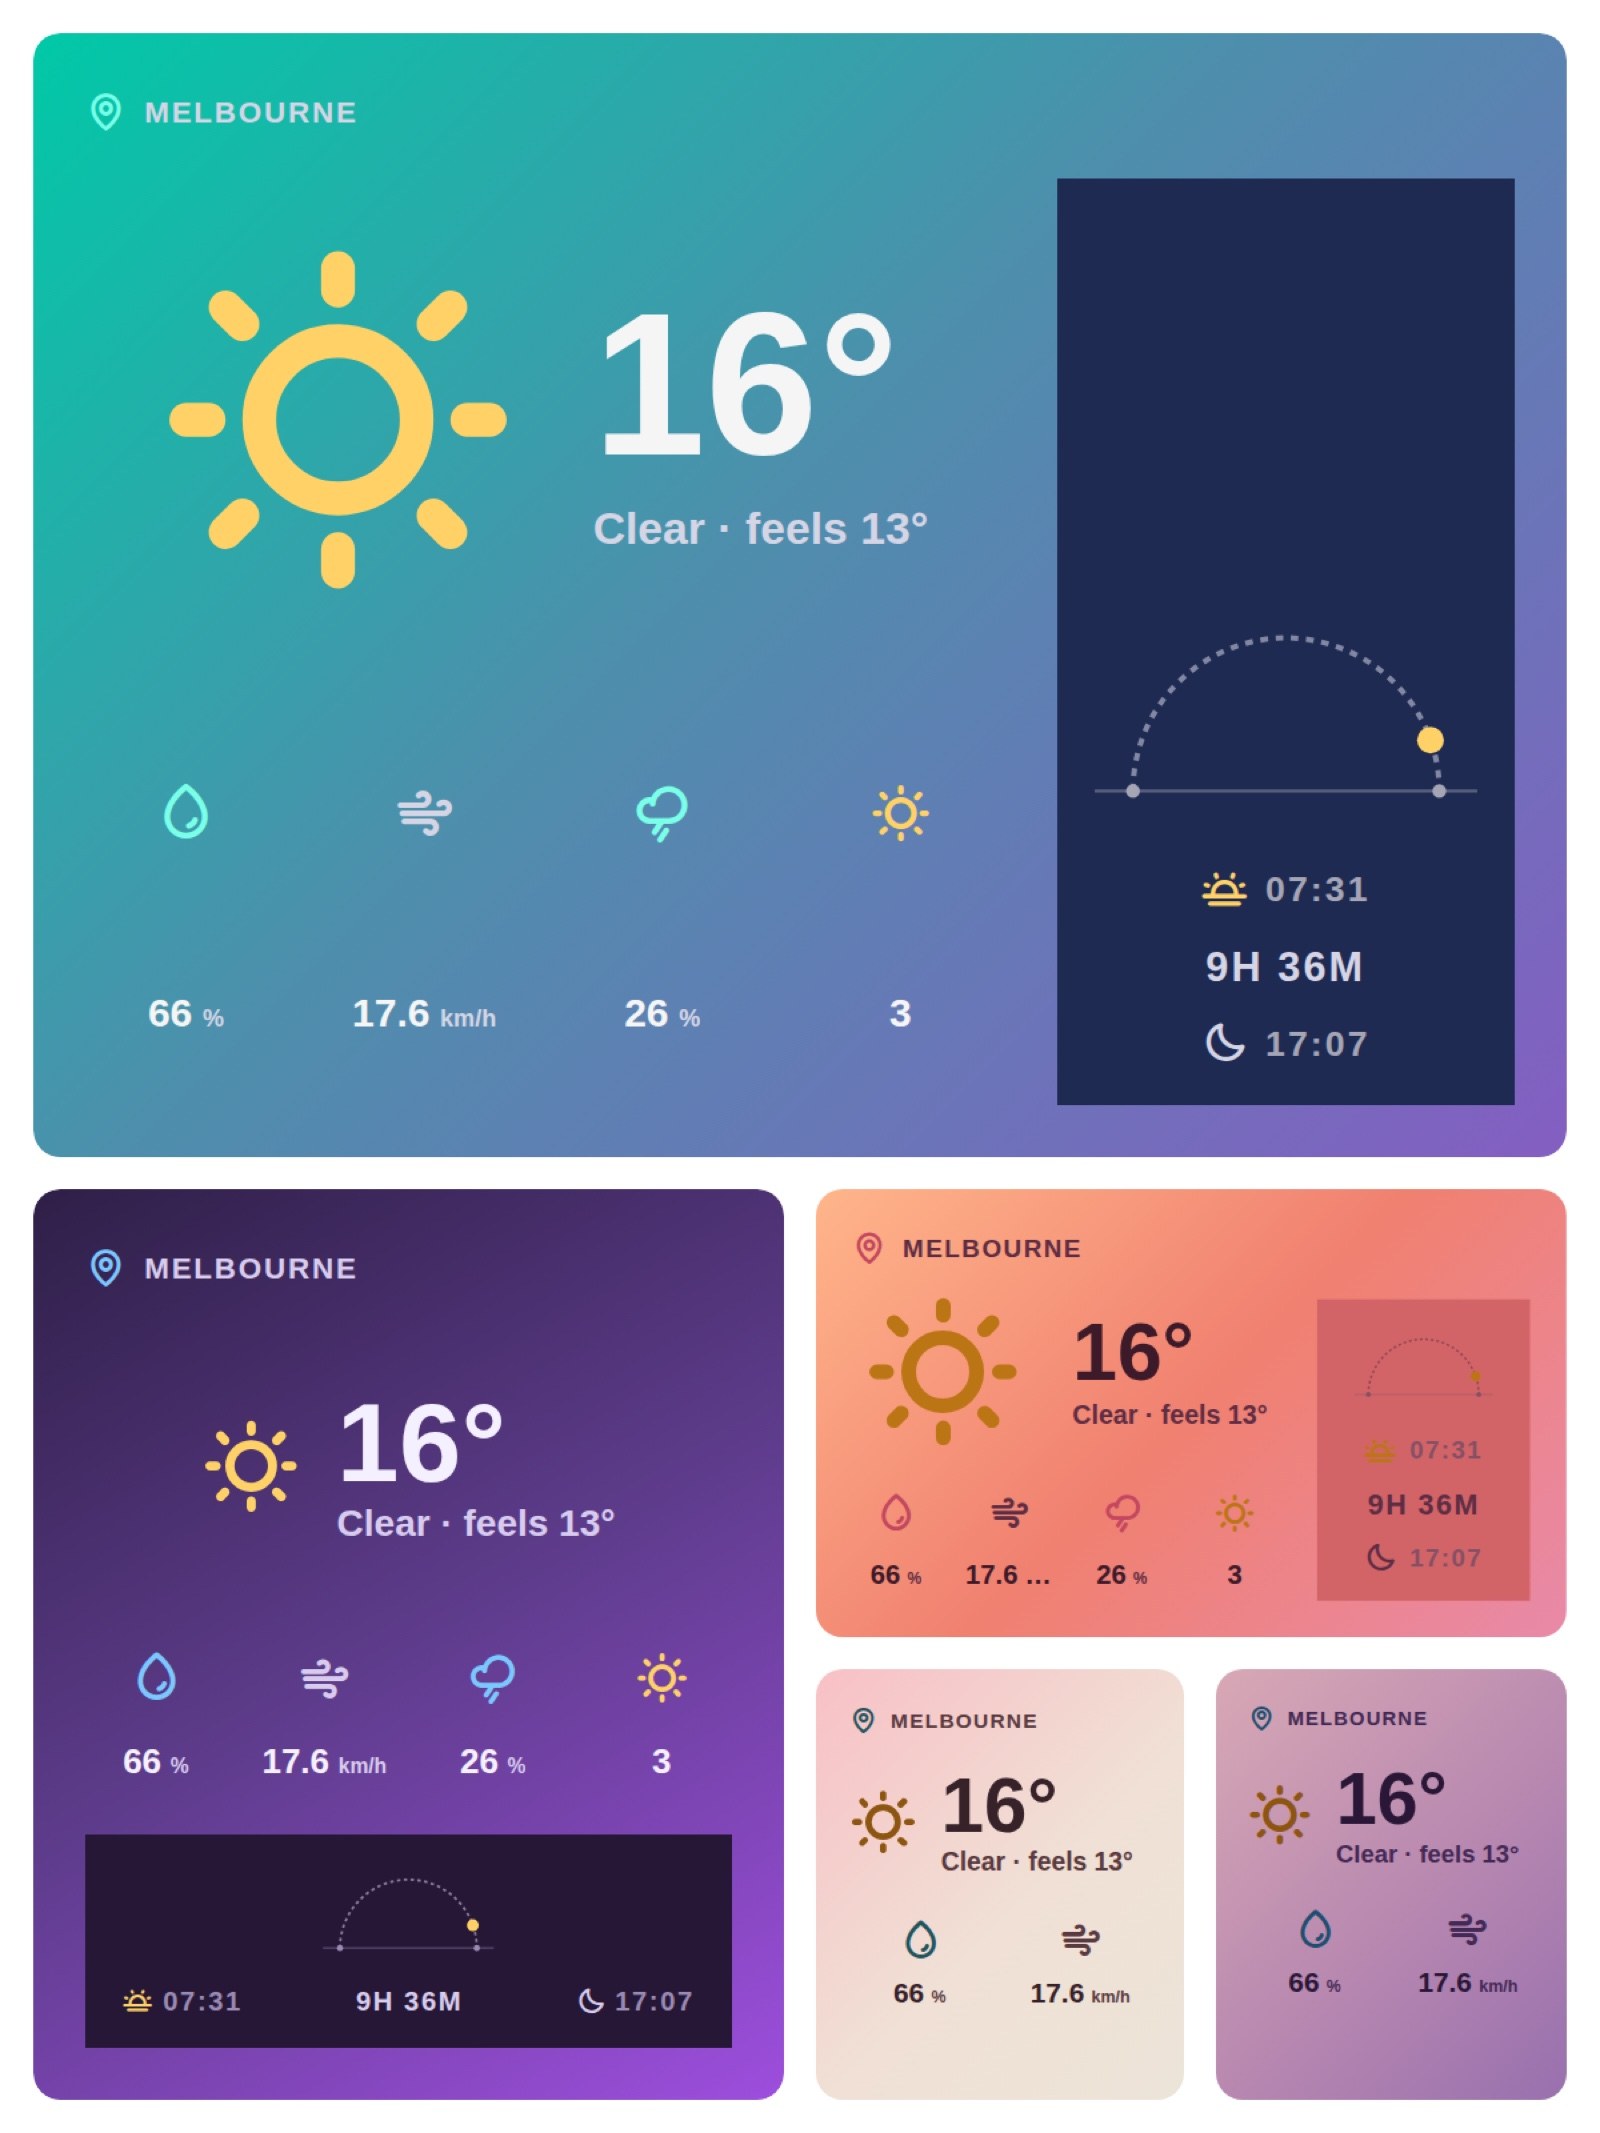
Tesserae is a self-hosted server that feeds dashboards to e-ink panels around the home. Pages are built in a browser editor — widget grids or pixel-precise free canvases — and every frame is produced on the server: headless Chromium captures the composition at the display's own resolution, then a per-device renderer applies Floyd-Steinberg dithering calibrated to measured panel palettes and packs the result into the byte layout that controller expects. Battery panels poll over REST while always-on clients take pushed MQTT frames, so one installation can run a fleet of screens, each rotating through its own schedule. About 37 widgets ship included (Open-Meteo weather, clock faces, calendar views, Hacker News / Reddit / RSS / Wikipedia feeds, many Home Assistant tiles, GTFS transit boards, NASA APOD, photo galleries, todo lists, a generic webpage embed), and community extras come from a reviewed catalog with checksum-verified installs. Every extension point — widgets, themes, render pipeline, transports, device drivers — is a folder you drop in; an MCP endpoint lets AI agents design a page, check a preview render, and send it to a screen. Run it with one docker compose up from the official ghcr.io image, as a one-click Home Assistant App, or via shell and PowerShell installers covering macOS, Linux, Pi and Windows machines (a systemd setup script is included); LXC and manual venv paths are documented too. First-party online contact — version checks, an anonymous install counter and a daily aggregate ping — is opt-in and off by default. Caveats: it is pre-1.0, the image is heavy (~2.5 GB unpacked, it bundles Chromium), the built-in broker tops out at MQTT v3.1.1, and third-party widgets run in-process under a socket-level egress allowlist rather than a true sandbox. A separate hosted Tesserae Cloud (waitlist, paid plans) exists; the self-hosted server is the full product, free under AGPL-3.0-or-later.
Should you self-host tesserae?
tesserae scores 51/100 on selfhost.directory (how scoring works) and ranks #14 of 44 in Dashboard. It has 973 GitHub stars.
It shipped 78 stable releases in the past year. The latest, v0.480.0, came out on 26 October 2026.
Setup is moderate: expect some configuration beyond a single command. An official Docker image is available. It is AGPL-3.0-licensed and written mostly in Python.
Its closest alternative on selfhost.directory is Homepage by gethomepage (84/100, 33 412 stars). It scores higher overall, so compare the two before you pick. See tesserae vs Homepage by gethomepage side by side.
Features
- Backup and data export/import
- Broad e-ink hardware support
- Browser dashboard composer
- Built-in MQTT Broker
- Bundled widget gallery
- Colour-palette dithering and calibration
- Community widget catalog
- Drop-a-folder plugin system
- Home Assistant Integration
- MCP API for AI agents
- MQTT and REST frame delivery
- Per-panel scheduling and rotation
- Server-side headless rendering
- Theme System
- Webhook-triggered re-render
tesserae README
More in Dashboard
 ThunderHubSelf-hosted, open-source web interface for Lightning node operators: manage LND or litd channels, payments, Taproot Assets and reports from any browser.
 tralaTraLa is a self-hosted, open-source dashboard that automatically discovers and displays your Traefik services with smart grouping, icon detection, and dark mode support.
 Vigil365Self-hosted open-source dashboard aggregating M365 security signals into one UI with alert policies, notifications, RBAC, and scheduled reports. Runs on Windows/Docker.
 WarmbOSWarmbOS is a self-hosted, open-source web desktop environment for homelab dashboards with drag-and-drop windows, persistent state, and themeable UI.
 WeatherStarA self-hosted, open-source simulator of the 1990s Weather Channel WeatherStar 4000 that builds retro forecast screens from NOAA/NWS data for US locations.
 web-portalSelf-hosted, open-source personal web dashboard with widget plugins, dark/light themes, and SQLite/MySQL support.
 XenonXenon is a self-hosted dashboard turning any spare screen into a PC control center with system stats, media controls, a Stream Deck-style key grid, and voice AI.
 your_lastfmYourLastFM is a self-hosted, open-source Node.js dashboard that syncs Last.fm scrobbles into SQLite for stats, friend comparisons, leaderboards, and recaps.
 adguard-buddySelf-hosted dashboard for monitoring and synchronizing multiple AdGuard Home servers with merged query logs, statistics, and drift detection.
 aegis_avataAEGIS is a self-hosted, open-source personal intelligence dashboard with Live2D avatar, Gemini voice briefings, and Notion, Google Calendar, YouTube Music integrations.
 Antigravity-DeckSelf-hosted web dashboard for Antigravity AI IDE — manage conversations, workspaces, cascades with full history, live control, and Cloudflare Tunnel remote access.
 AppsmithOpen-source low-code platform for self-hosted internal tools, admin panels and dashboards, deployed as one Docker container or via Helm with Git version control.
0 comments