Self-host voidaccess
v2.1.0Dark-web OSINT platform for automated threat intelligence
- Stars
- 947
- Ports
- 3001 (Web UI (Next.js frontend)), 8000 (REST API (FastAPI backend)), 9050 (Tor SOCKS5 proxy)
- Requires
- Meilisearch, PostgreSQL, Tor
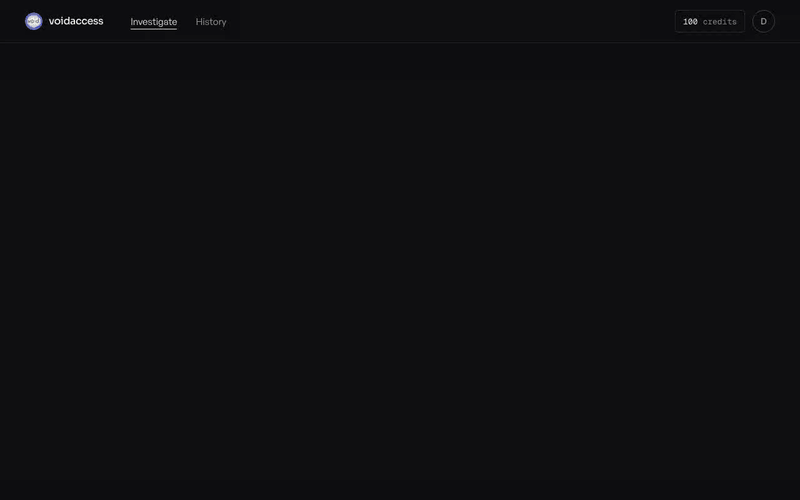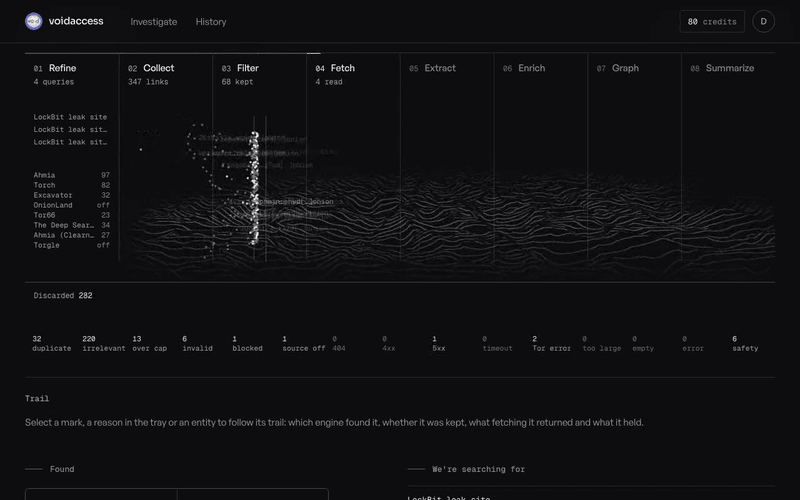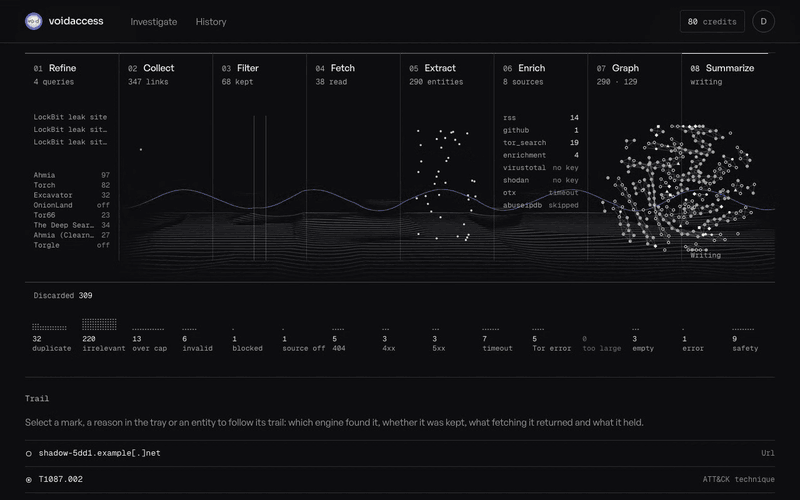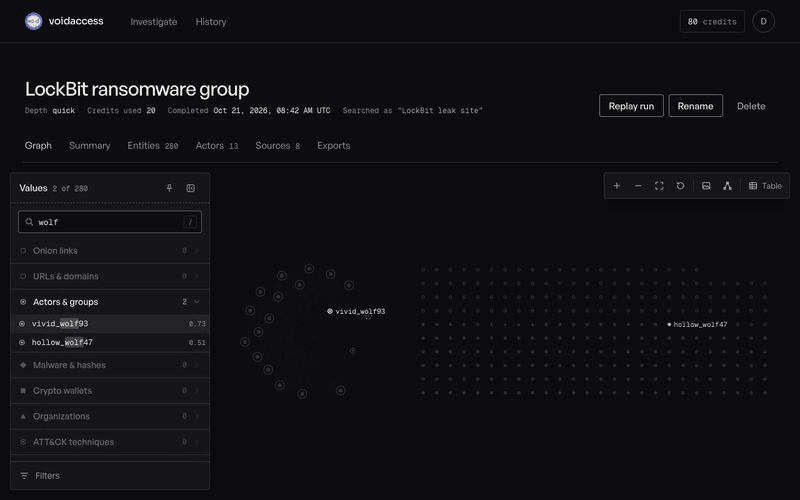
What is voidaccess?
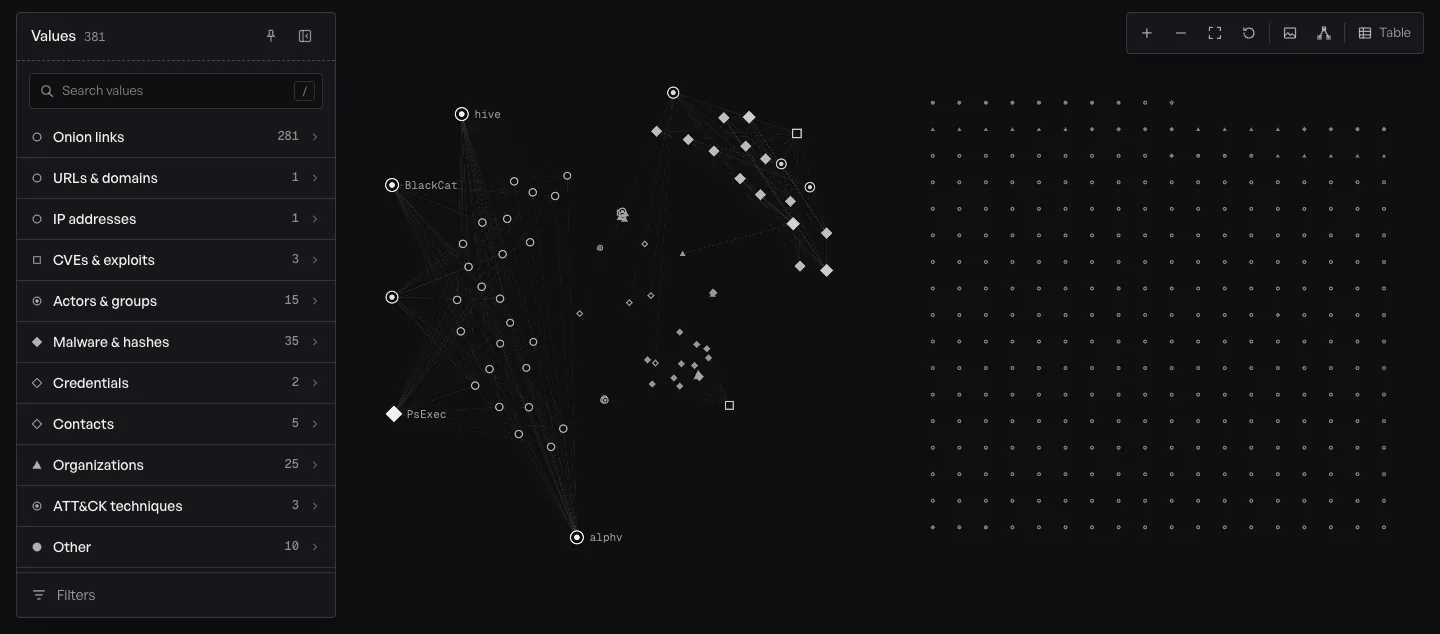
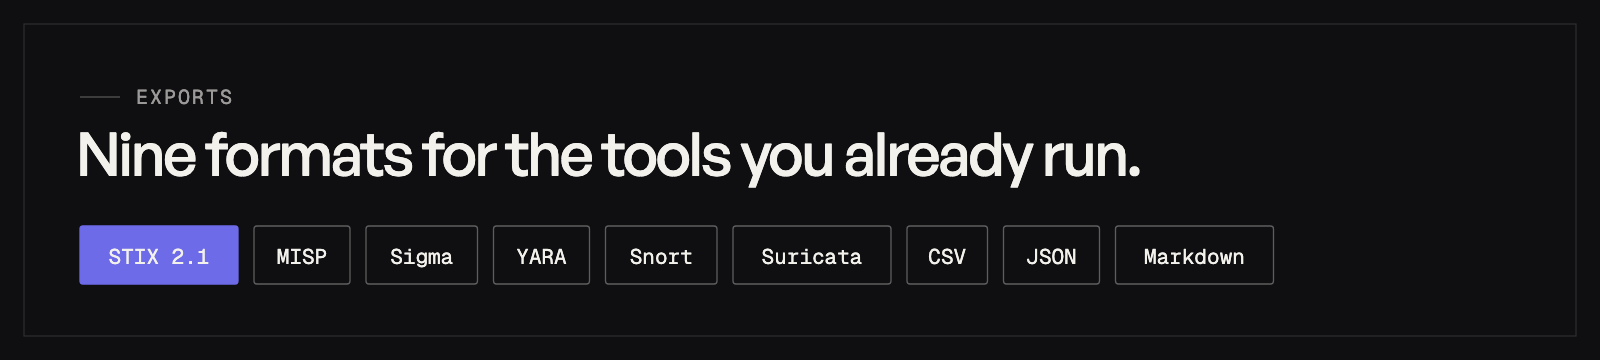
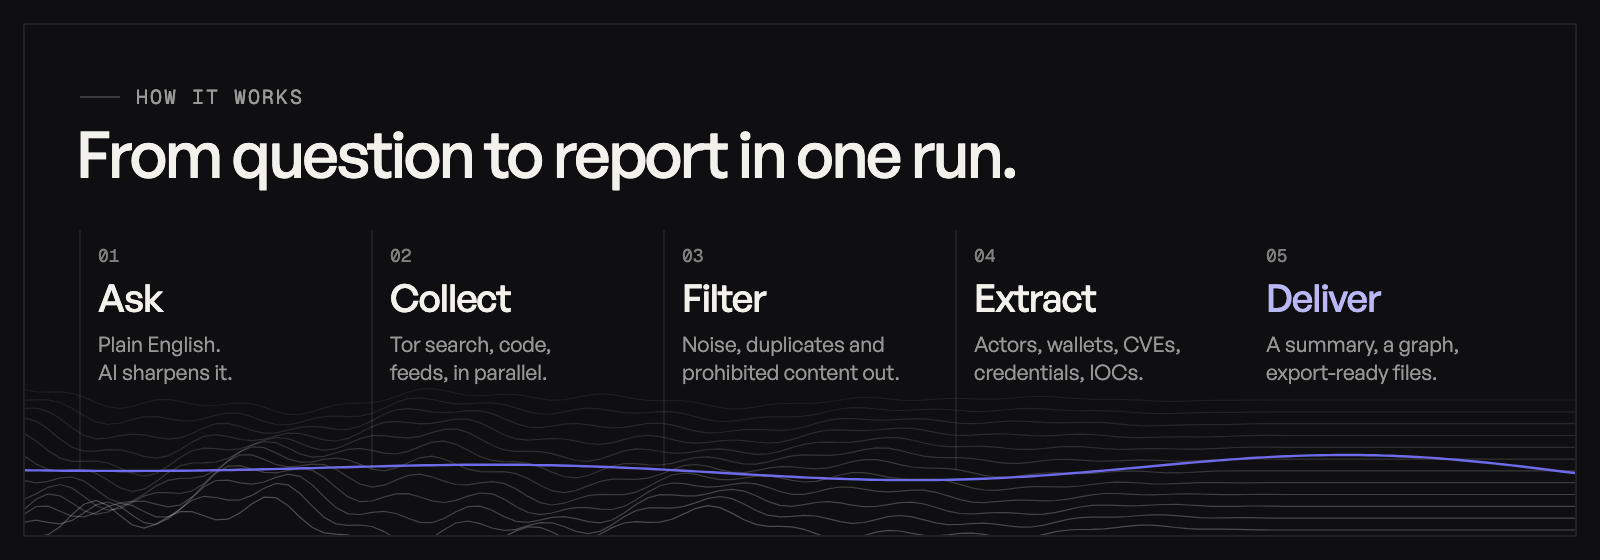
VoidAccess is a self-hosted dark-web OSINT platform for security researchers and threat-intel teams. It automates intelligence gathering from question to visual graph, querying multiple Tor search engines, code repositories, and security feeds simultaneously. It identifies threat actors, malware families, CVEs, crypto wallets, credentials, messaging handles, and infrastructure indicators, connecting them into a searchable relationship graph. Results export in nine formats for sharing and detection including STIX and MISP for sharing, Sigma and YARA for detection rules, Snort and Suricata for network rules, plus CSV, JSON, and Markdown. Runs as a CLI or containerized deployment with PostgreSQL, Tor, FastAPI, and Next.js. MIT licensed.
Should you self-host voidaccess?
voidaccess scores 57/100 on selfhost.directory (how scoring works) and ranks #28 of 78 in Security. It has 947 GitHub stars.
It shipped 18 stable releases in the past year. The latest, v2.1.0, came out on 18 October 2026. New versions land roughly every 1 days.
Setup is advanced: plan for several services and some ongoing maintenance. It is MIT-licensed and written mostly in Python.
Its closest alternative on selfhost.directory is pentagi (83/100, 32 610 stars). It scores higher overall, so compare the two before you pick. See voidaccess vs pentagi side by side.
Features
- Clearnet-only mode
- CLI Interface
- Content safety filters
- Dark-web search
- Entity extraction
- LLM provider flexibility
- Multi-format Export
- Multi-user support
- Relationship graph
- REST API
- Threat intelligence collection
- Web UI
voidaccess README
FAQ
Can I self-host instead?
Yes. Install with 'pip install voidaccess', MIT license, free forever.
Who is it not for?
Not for stalking, doxxing, harassment, or anyone looking for illegal content or services. Accounts that try are closed.
What happens to my queries?
Investigations are kept while your account is open and deleted when you delete it. Queries and collected text go to AI providers to refine search and write summaries, never with account details. Findings go into an anonymous, dated archive without your identity or query text.
Will it show me illegal content?
Safety filters block prohibited queries, links, and page content before anything reaches you. Results never link to dark-web pages; found addresses are shown as copyable text, not links.
Is this legal?
VoidAccess searches publicly reachable sources: Tor search engines, code hosts, and public threat feeds. It doesn't log into closed forums or buy data. Use is limited to security research and authorized investigation by the Acceptable Use Policy.
More in OSINT
 web-checkOpen-source, self-hosted OSINT tool that runs 44 checks on any URL - DNS, TLS, headers, ports, CVEs, trackers - through a web UI or plain API.
 World MonitorSelf-hosted open-source dashboard streaming 460 news feeds from 761 providers onto a live map with 57 layers, correlating geopolitics, markets, shipping, aviation
 AkashicSelf-hosted open-source geospatial intelligence workspace combining live aircraft, satellite, seismic, weather, radio, and OSINT data on an interactive map.
 Global Threat MapSelf-hosted, open-source OSINT command center: a Next.js Mapbox app plotting real-time global events, wars, conflicts and military bases, with AI intel dossiers.
 God's Eye ViewSelf-hosted open-source CesiumJS globe with live flights, ships, satellites, weather and public camera feeds, voice AI control and an MCP server.
 spiderfootSpiderFoot automates OSINT for threat intelligence and mapping your attack surface.
0 comments