Self-host Snitch
v1.6.4Real-time network monitor and outbound firewall
sudo docker run --network host --cap-add NET_ADMIN --cap-add NET_RAW -v snitch-data:/app/data ghcr.io/aixisstudio/snitch- Stars
- 638
- Port
- 8000 (HTTP API and Web UI)
- Requires
- libpcap / Npcap
ghcr.io/aixisstudio/snitch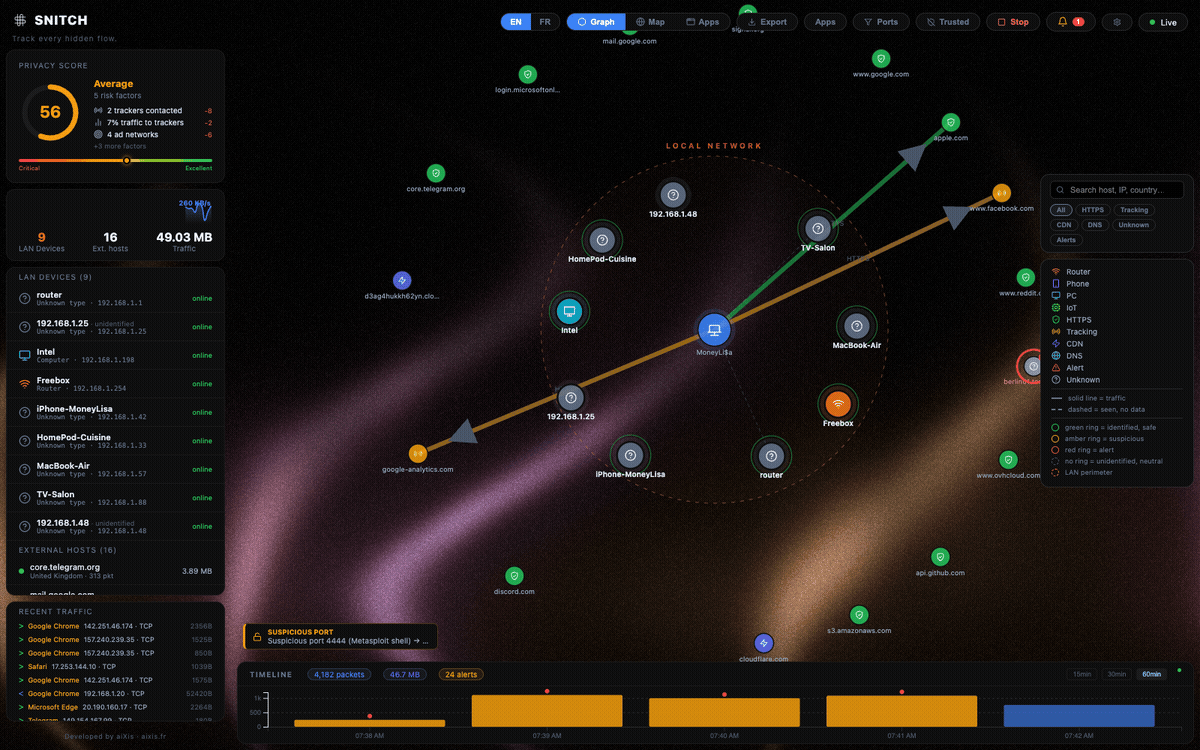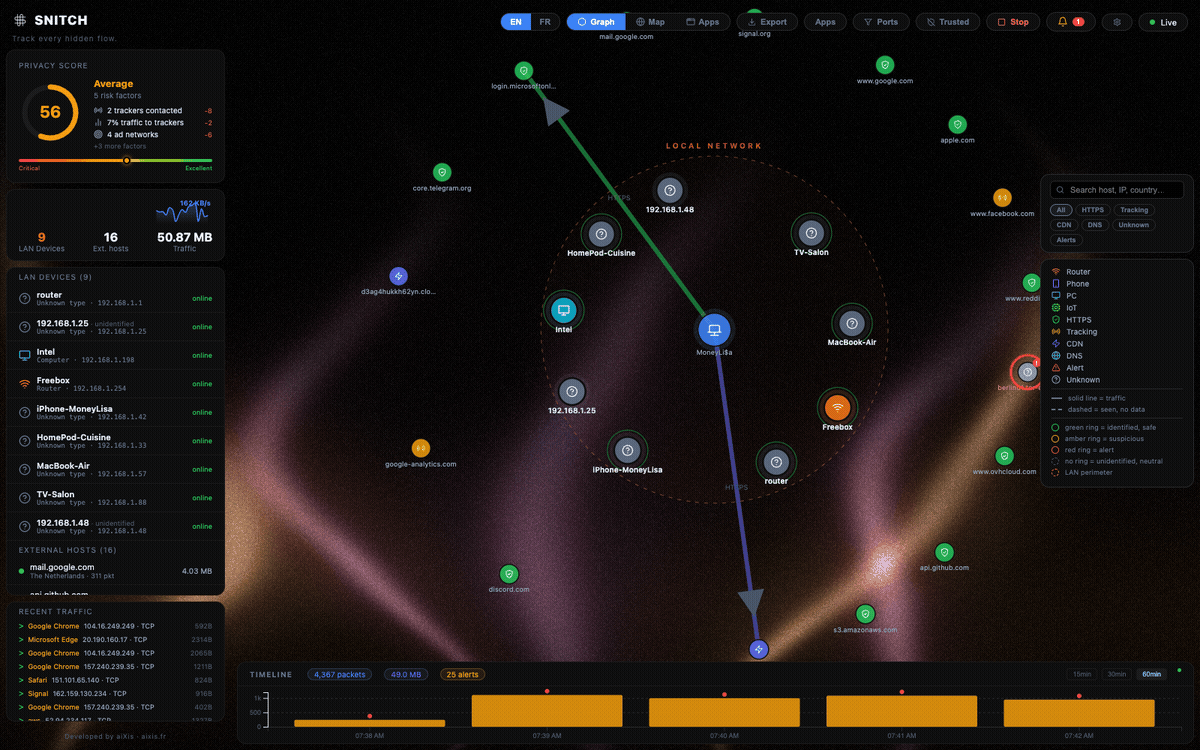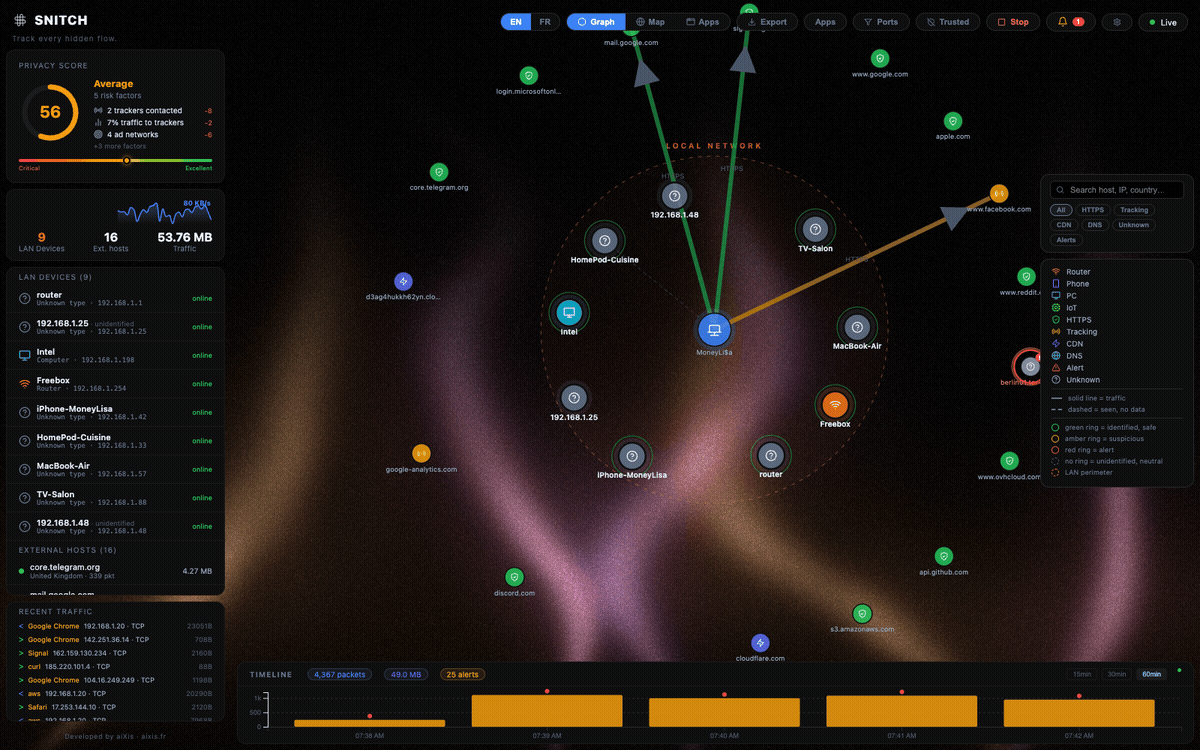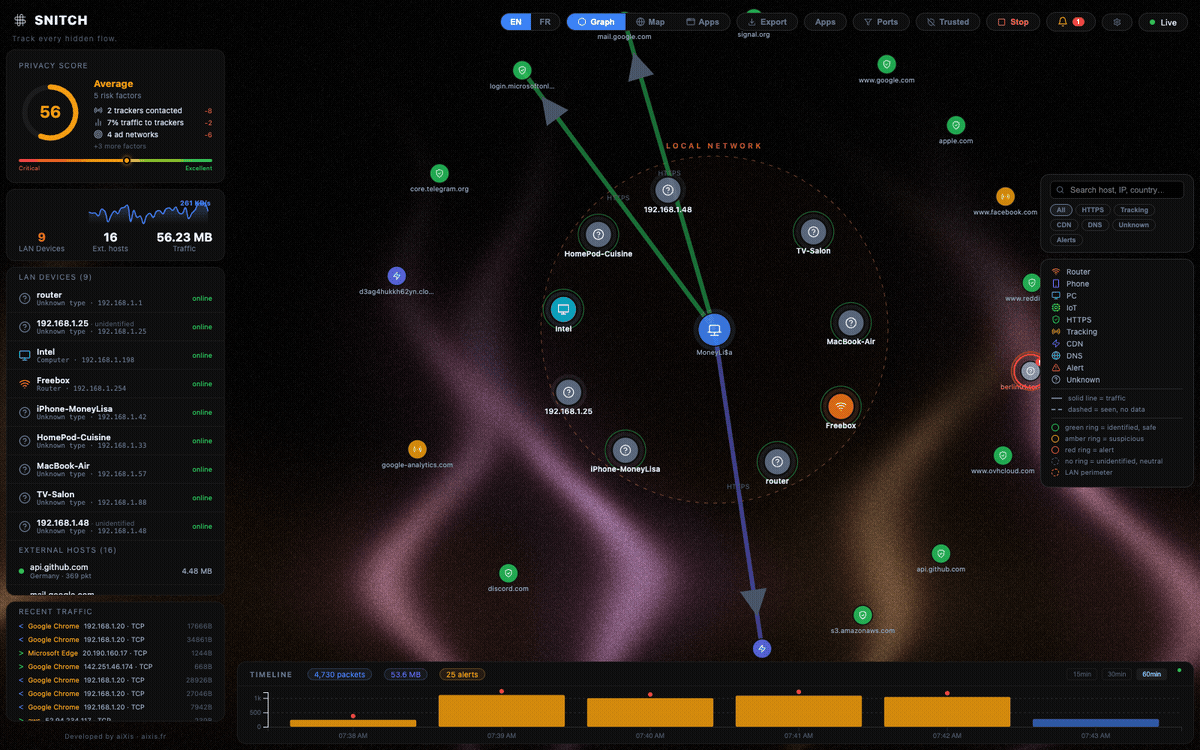
What is Snitch?
Snitch is a privacy-first network monitoring tool that lets you see every outbound connection from your computer in real time. It displays a live force-directed graph with your machine at the center, a geolocated world map of remote hosts, and a sliding timeline of traffic history. The software detects anomalies like port scans, beaconing, DNS tunneling, and data exfiltration patterns using pure-Python ML models. It can block connections through the OS-native firewall (Windows Filtering Platform, nftables/iptables, pf) rather than filtering in user space. Snitch runs as a desktop app (Electron/React) on macOS, Windows, and Linux, plus a headless daemon for servers and a Docker container for Linux. All data stays local in SQLite with configurable retention; geolocation uses an offline DB-IP Lite database. Optional integrations include syslog/SIEM export (CEF, RFC 3164), webhooks to chat platforms, and threat intelligence lookups with your own API keys. The project is licensed under AGPL-3.0 and has no telemetry or mandatory outbound calls.
Should you self-host Snitch?
Snitch scores 54/100 on selfhost.directory (how scoring works) and ranks #20 of 48 in Network Monitoring. It has 638 GitHub stars.
It shipped 10 stable releases in the past year. The latest, v1.6.4, came out on 23 October 2026.
Setup is moderate: expect some configuration beyond a single command. An official Docker image is available. It is AGPL-3.0-licensed and written mostly in Python.
Its closest alternative on selfhost.directory is mitmproxy (86/100, 46 448 stars). It scores higher overall, so compare the two before you pick. See Snitch vs mitmproxy side by side.
Features
- Actionable alerts
- Advanced Threat Detection
- Anomaly Detection
- Ask-on-connect (Linux)Linux only, requires root
- Entropy watch
- Firewall orchestration
- Geolocated world map
- ICMP tunnel detection
- IOC peer sync
- Memory forensicsLinux only
- ML anomaly scoring
- Passive TLS inspection
- Real-time Network Monitoring
- Sliding timeline history
- Syslog/SIEM export
Snitch README
More in Network Security
 spoofdpiSelf-hosted, open-source anti-censorship proxy that beats Deep Packet Inspection via TLS fragmentation, fake packets and DoH, in HTTP, SOCKS5 and TUN modes.
 strongswanSelf-hosted open-source IPsec VPN: an IKEv2/IKEv1 daemon for site-to-site and road-warrior tunnels with X.509 or EAP auth on Linux, FreeBSD, macOS and Windows.
 subspaceSelf-hosted, open-source web GUI for running a WireGuard VPN server: per-device configs with QR codes, SAML SSO with G Suite or Okta, and Let's Encrypt TLS.
 Technitium DNS ServerSelf-hosted, open-source authoritative and recursive DNS server with a web console, DNS sinkhole ad blocking, DoH/DoT/DoQ, and a built-in DHCP server.
 traefik-geoip-filterSelf-hosted Docker container adding GeoIP filtering to Traefik, allowing or blocking traffic by country, region, or city via MaxMind GeoLite2.
 UnboundSelf-hosted, open-source DNS resolver that validates, recurses and caches, adding DNS-over-TLS, HTTPS and QUIC, RPZ filtering and DNSSEC privacy features.
 wireguard-uiSelf-hosted, open-source web UI for administering a WireGuard VPN: manage peers, hand out configs via QR code, file, email or Telegram, and tweak server settings.
 Xray VPN OneClickSelf-hosted tool that deploys a VLESS+Reality proxy server on Linux in minutes with CLI for user management, traffic quotas, and subscription links.
 Zed Attack Proxy (ZAP)Self-hosted, open-source web app security scanner: an intercepting proxy with passive and active scans, three spiders, API scans and Docker automation for CI/CD.
 3proxySelf-hosted, open-source tiny proxy server: HTTP/HTTPS, SOCKS4/5, FTP, DNS and port mapping with ACLs, bandwidth limits and parent chaining.
 amneziawg-installerSelf-hosted, open-source AmneziaWG 3.1 VPN server you provision on your own VPS with a single bash script: DPI-proof obfuscation, no Docker, kernel module.
 beelzebubOpen-source, self-hosted deception runtime that turns SSH, HTTP, TCP, Telnet, MCP decoys into honeypots, configured via YAML rules, with LLM replies and Go plugins.
0 comments