Self-host OAuth2 Proxy
v7.15.6Reverse proxy that fronts apps with OAuth2/OIDC sign-in
- Stars
- 15 381
- Ports
- 4180 (HTTP listener, default bind 127.0.0.1:4180), 443 (HTTPS listener when the proxy terminates TLS itself)
quay.io/oauth2-proxy/oauth2-proxy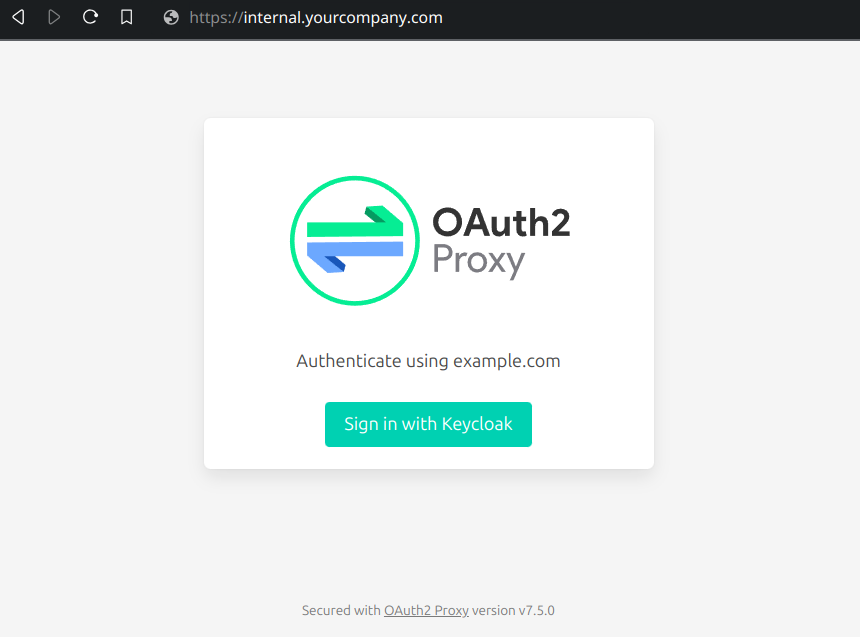
What is OAuth2 Proxy?
OAuth2 Proxy is a reverse proxy and middleware that stands in front of your web applications and makes visitors pass an OAuth2 or OpenID Connect login before any request reaches the upstream. It can serve as the whole front door or slot into infrastructure you already have, where it hands back 202/401 verdicts for auth_request style setups. Dedicated provider implementations cover Google, Microsoft Entra ID, GitHub, GitLab, Keycloak and login.gov among others, and a generic OIDC client handles the rest; specialised providers can also lift extra detail such as preferred usernames and group membership out of the token and forward it to the upstream as HTTP headers. Access can be narrowed to certain email domains, individual addresses or groups, and sessions live either in signed, encrypted cookies or in Redis, including Sentinel and cluster setups. Static files, WebSocket traffic and several upstreams with path-based routing are all supported, the proxy can terminate TLS on its own, and it exposes Prometheus metrics plus ping and ready endpoints. Settings come from command-line flags, a TOML file or OAUTH2_PROXY_ environment variables, and --config-test checks them without starting the server. Deploy it with the GitHub release binaries, the distroless Quay image (Alpine variants still tagged -alpine), go install, or the official Helm manifests; it is a MIT-licensed CNCF Sandbox project driven by volunteers, and multi-provider setups are still unfinished.
OAuth2 Proxy alternatives
 autheliaSelf-hosted, open-source IAM portal providing single sign-on, multi-factor authentication and an OpenID Certified OpenID Connect provider for proxied apps.Compareauthelia with OAuth2 Proxy
 DexOpen-source, self-hosted OIDC and OAuth 2.0 identity service that fronts LDAP, SAML, GitHub, Google and other IdPs, so every app just speaks OpenID Connect.CompareDex with OAuth2 Proxy
 voidauthOpen-source SSO for homelabs: an OIDC provider, reverse-proxy forward-auth, optional read-only LDAP, and user management with invitations, passkeys and MFA.Comparevoidauth with OAuth2 Proxy
 autenticoSelf-hosted OIDC identity provider as a single Go binary with SQLite, handling login, MFA, passkeys, sessions, and tokens with built-in admin UI.Compareautentico with OAuth2 Proxy
 GitProxyGitProxy is a self-hosted, open-source proxy that intercepts git push to enforce security policies like secret detection and commit validation.CompareGitProxy with OAuth2 Proxy
 PomeriumOpen-source self-hosted identity-aware reverse proxy that gates private web apps, SSH and TCP services through OIDC sign-in and per-request access policy.ComparePomerium with OAuth2 Proxy
 TraefikTraefik is a self-hosted, open-source reverse proxy that auto-discovers services from Docker, Kubernetes, and other orchestrators to route traffic without manual config.CompareTraefik with OAuth2 Proxy
 authentikSelf-hosted, open-source identity provider for SSO over OIDC, SAML, LDAP, RADIUS and SCIM, with TOTP and passkeys, configurable flows, RBAC and Helm or Compose installs.Compareauthentik with OAuth2 Proxy
Should you self-host OAuth2 Proxy?
OAuth2 Proxy scores 75/100 on selfhost.directory (how scoring works) and ranks #3 of 19 in Identity & Auth. It has 15 381 GitHub stars, +223 in the last 30 days.
It shipped 11 stable releases in the past year. The latest, v7.15.6, came out on 5 November 2026. New versions land roughly every 4 weeks.
Setup is moderate: expect some configuration beyond a single command. An official Docker image is available. It is MIT-licensed and written mostly in Go.
Its closest alternative on selfhost.directory is jumpserver (77/100, 31 970 stars). It scores higher overall, so compare the two before you pick. See OAuth2 Proxy vs jumpserver side by side.
Features
- Configuration validation
- Custom Templates
- Email and group access control
- Health check endpoints
- Many identity providers
- Middleware / auth_request mode
- OAuth2/OIDC authentication gate
- Prometheus metrics endpoint
- Sign-in and sign-out handling
- TLS Termination
- Upstream proxying and static files
- User info header forwarding
- WebSocket proxying
OAuth2 Proxy README


OAuth2 Proxy is a flexible, open-source tool that can act as either a standalone reverse proxy or a middleware component integrated into existing reverse proxy or load balancer setups. It provides a simple and secure way to protect your web applications with OAuth2 / OIDC authentication. As a reverse proxy, it intercepts requests to your application and redirects users to an OAuth2 provider for authentication. As a middleware, it can be seamlessly integrated into your existing infrastructure to handle authentication for multiple applications.
More in Identity & Auth
 openamSelf-hosted open-source access management: SSO, SAML, OAuth 2.0 and OIDC federation, adaptive authentication, centralized policy; ships as a Docker image or WAR.
 oryOpen-source, self-hosted identity server for login, registration, recovery and MFA, with passkeys, TOTP and social sign-in served through headless HTTP APIs.
 permifyAn open-source authorization as a service inspired by Google Zanzibar, designed to build and manage fine-grained and scalable authorization systems for any application. — Permify is now part of FusionAuth 🎉
 phpLDAPadminphpLDAPadmin (PLA) is a self-hosted, open-source web app for browsing, searching, and modifying LDAP directory data — a user-friendly alternative to CLI LDAP tools.
 Pocket IDSelf-hosted, open-source OpenID Connect Certified provider for homelabs and small teams that find Keycloak or Authentik too heavy; passkey sign-in only.
- PomeriumOpen-source self-hosted identity-aware reverse proxy that gates private web apps, SSH and TCP services through OIDC sign-in and per-request access policy.
 pwmPWM is a self-hosted, open-source password self-service app for LDAP directories. Users reset passwords, unlock accounts, and manage credentials via web UI.
 qauthQAuth is a self-hosted, open-source OAuth 2.1/OIDC 1.0 server for AI agents with on-behalf-of delegation, audience-bound tokens, and post-quantum ready crypto.
 rauthyOpen-source, self-hosted Rust identity provider: single sign-on for apps and Linux hosts via OIDC, OAuth 2 and PAM, with passkey-first MFA, HA mode and an admin UI.
- SambaSamba is an open-source implementation of the SMB/CIFS protocol for Linux and Unix systems, providing secure, stable, and fast file and print services.
 supertokensSelf-hosted, open-source authentication service replacing Auth0, Firebase Auth or AWS Cognito, with passwordless, social, email-password login and session management.
 tesseralTesseral is a self-hosted, open-source auth platform for B2B SaaS with multi-tenant login, SAML/OIDC/SCIM, RBAC, MFA, passkeys, API keys, and audit logs.
0 comments