Self-host authelia
v4.39.28MFA SSO portal and OpenID Connect provider for your apps
- Stars
- 29 659
- Port
- 9091 (Main HTTP server listener, default address tcp://:9091/)
docker.io/authelia/authelia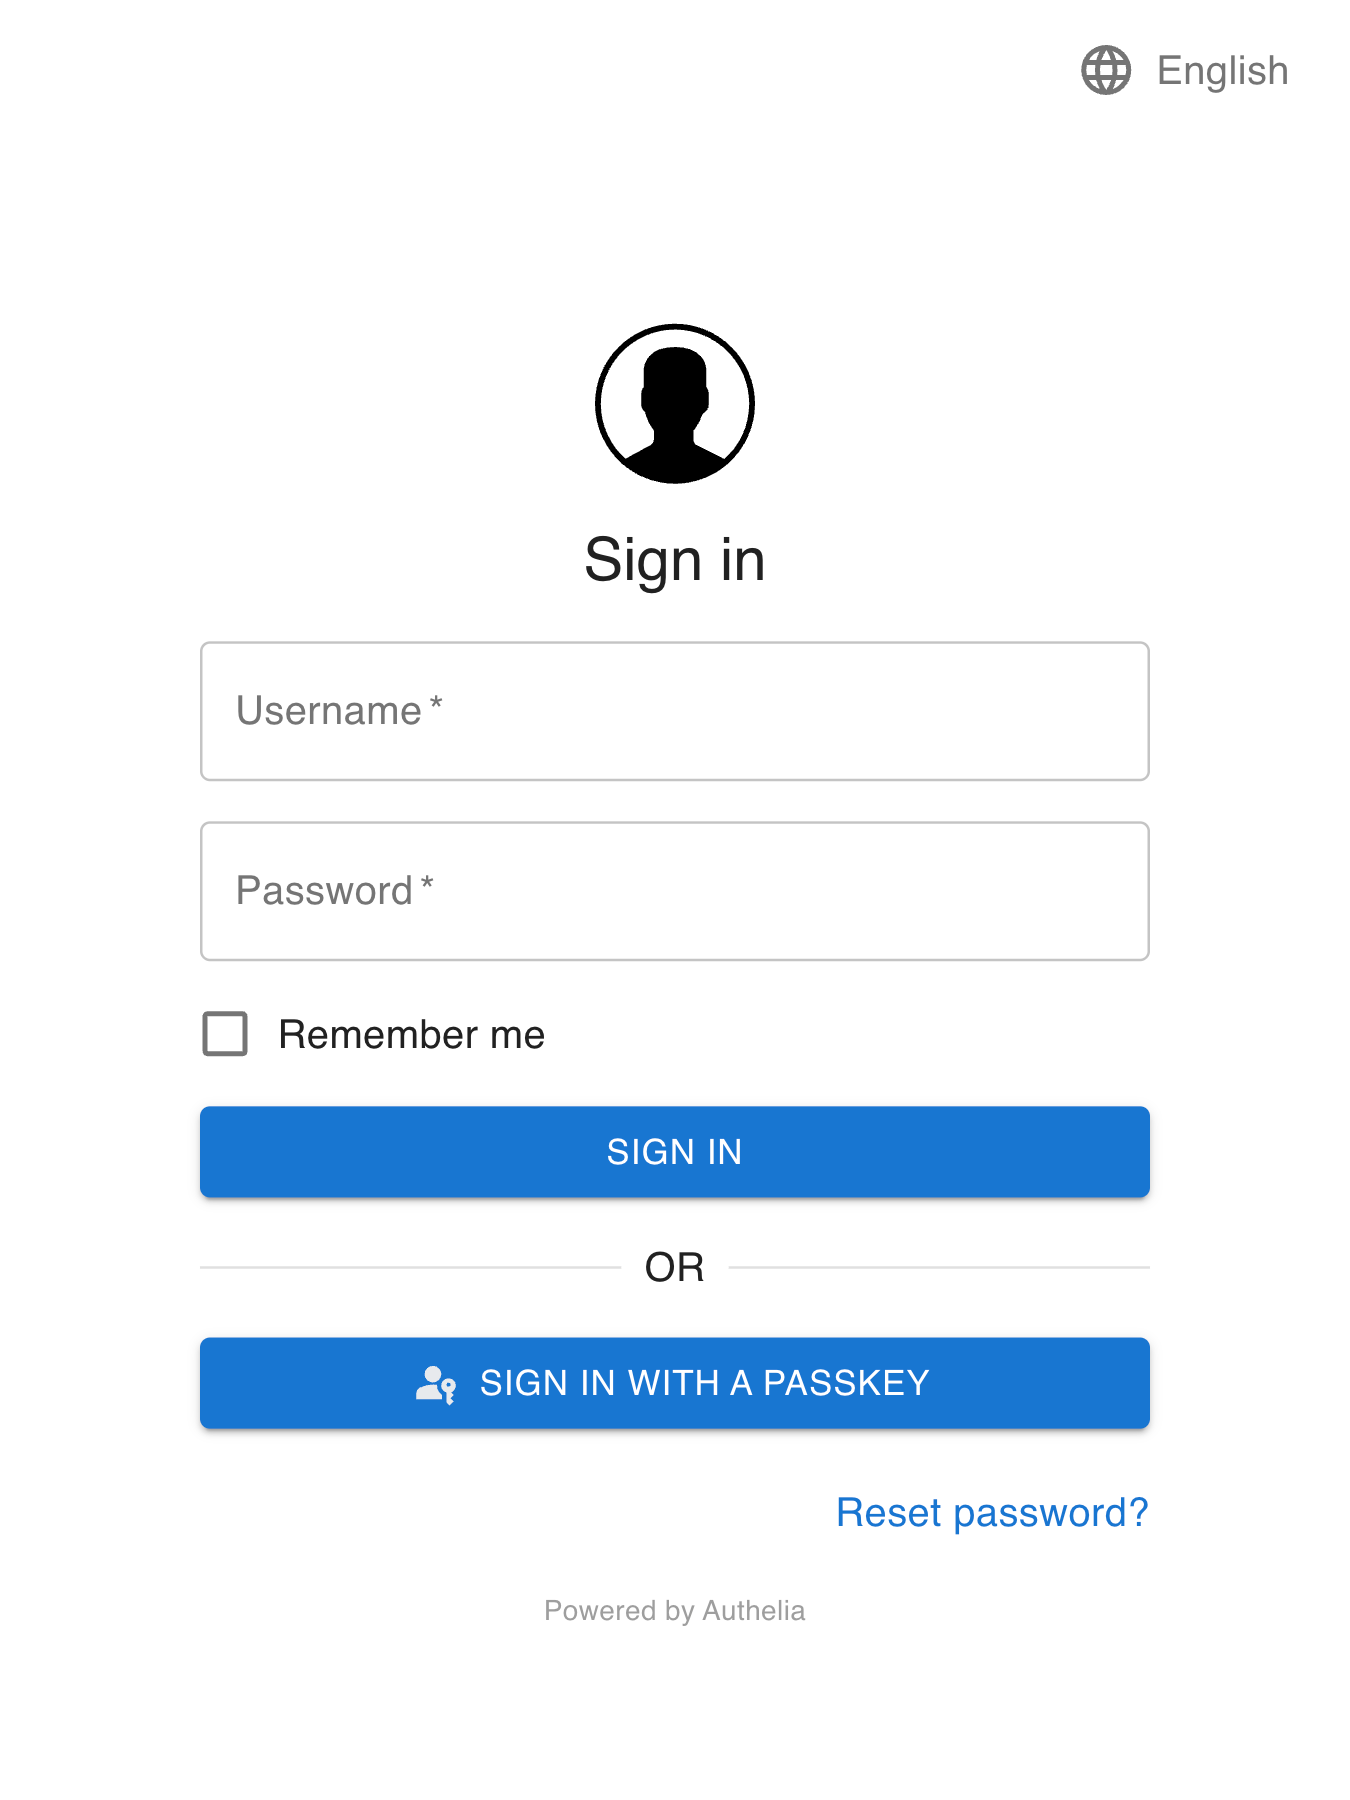
What is authelia?
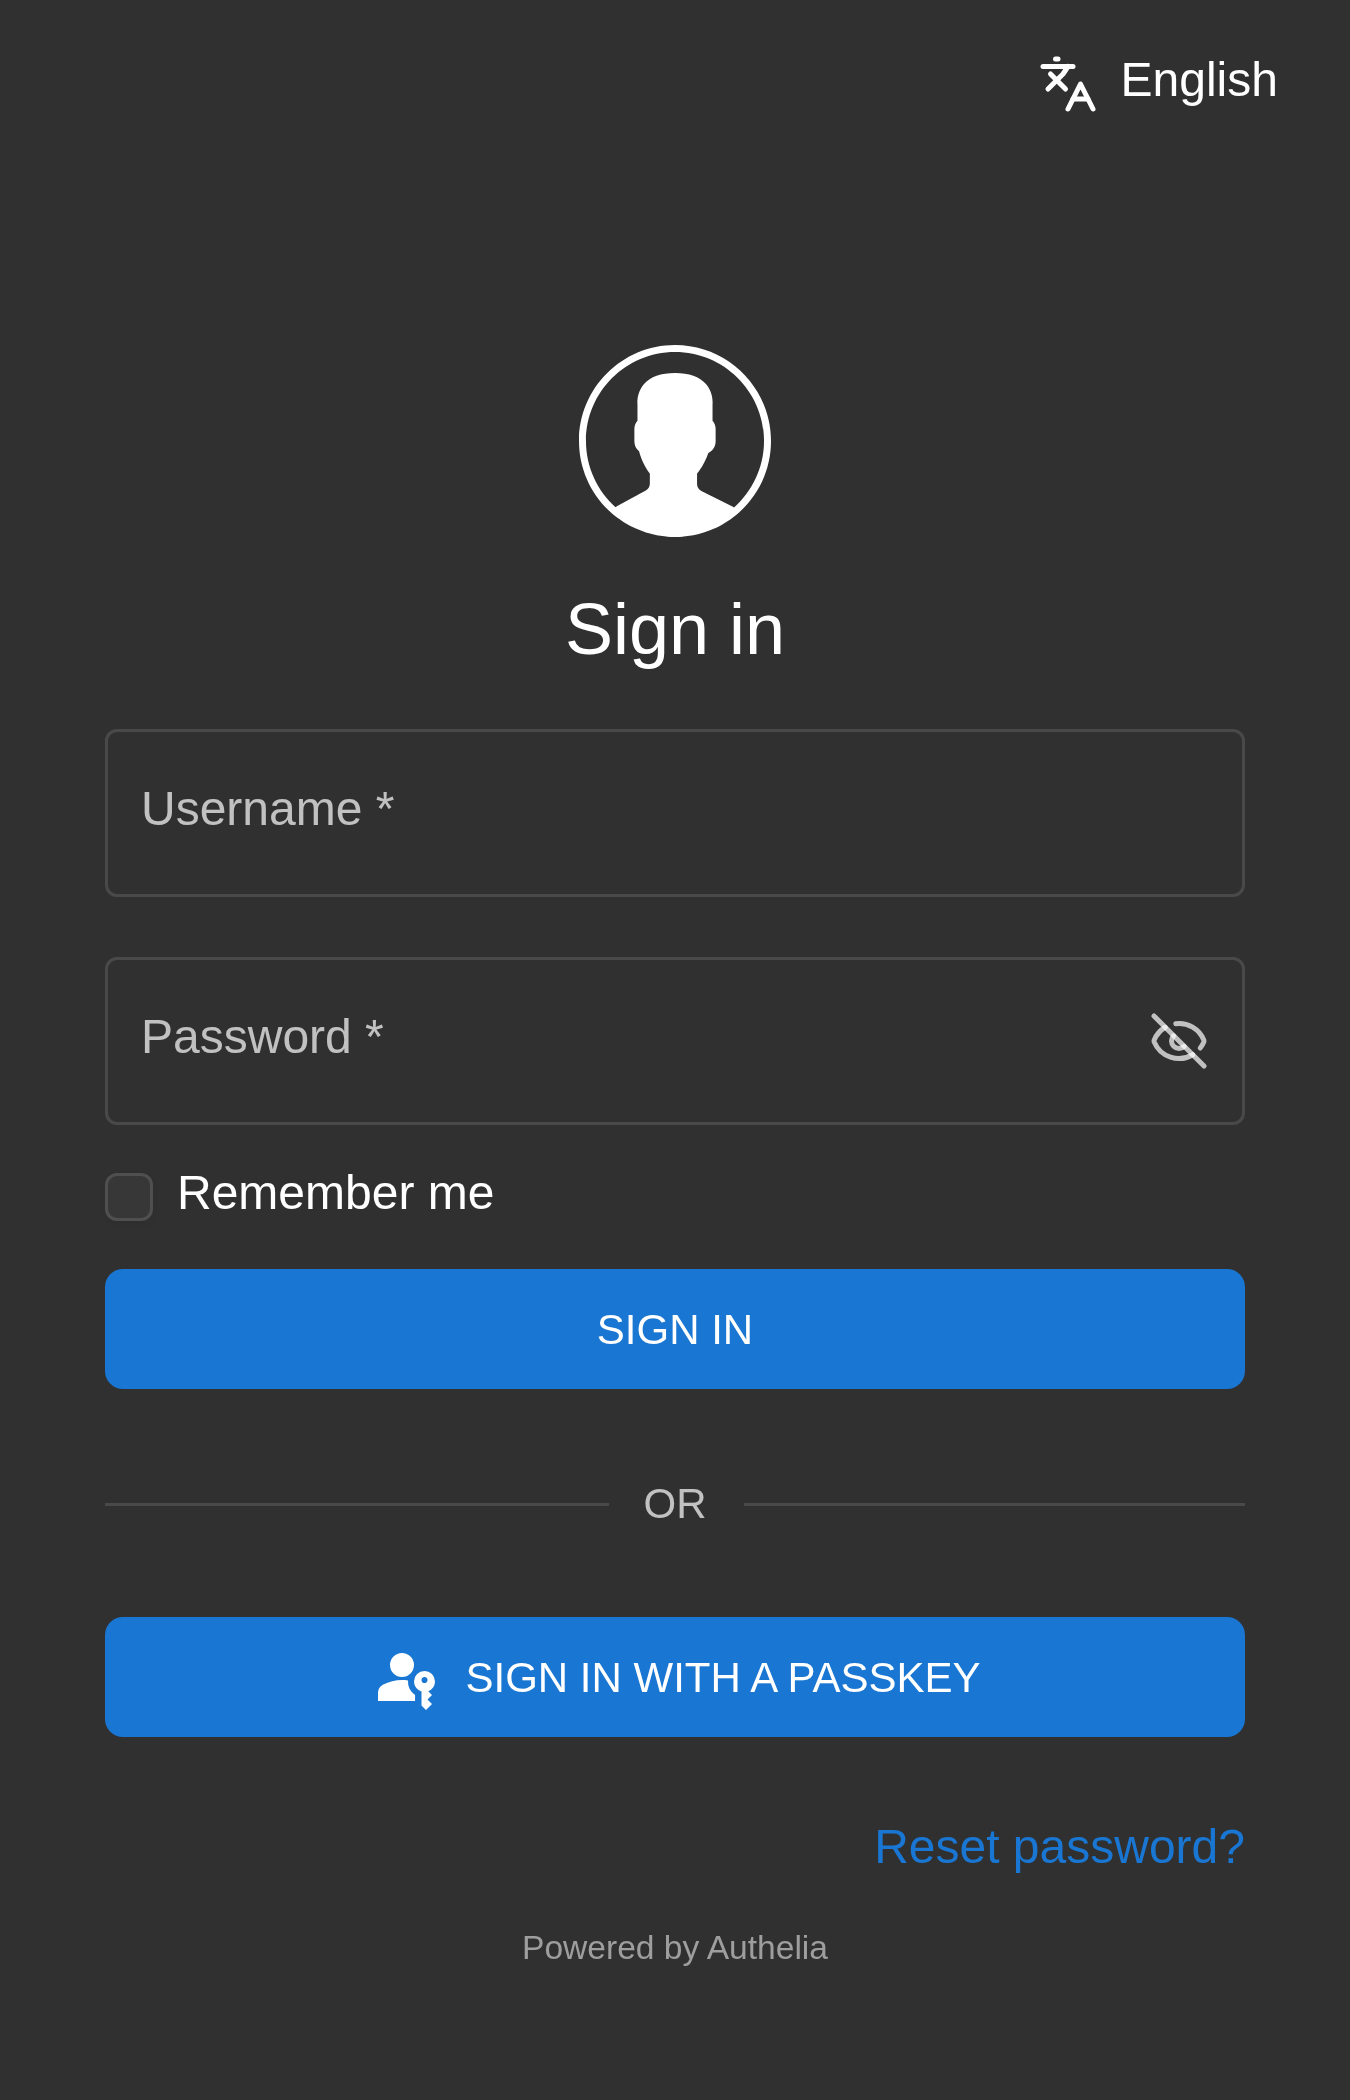
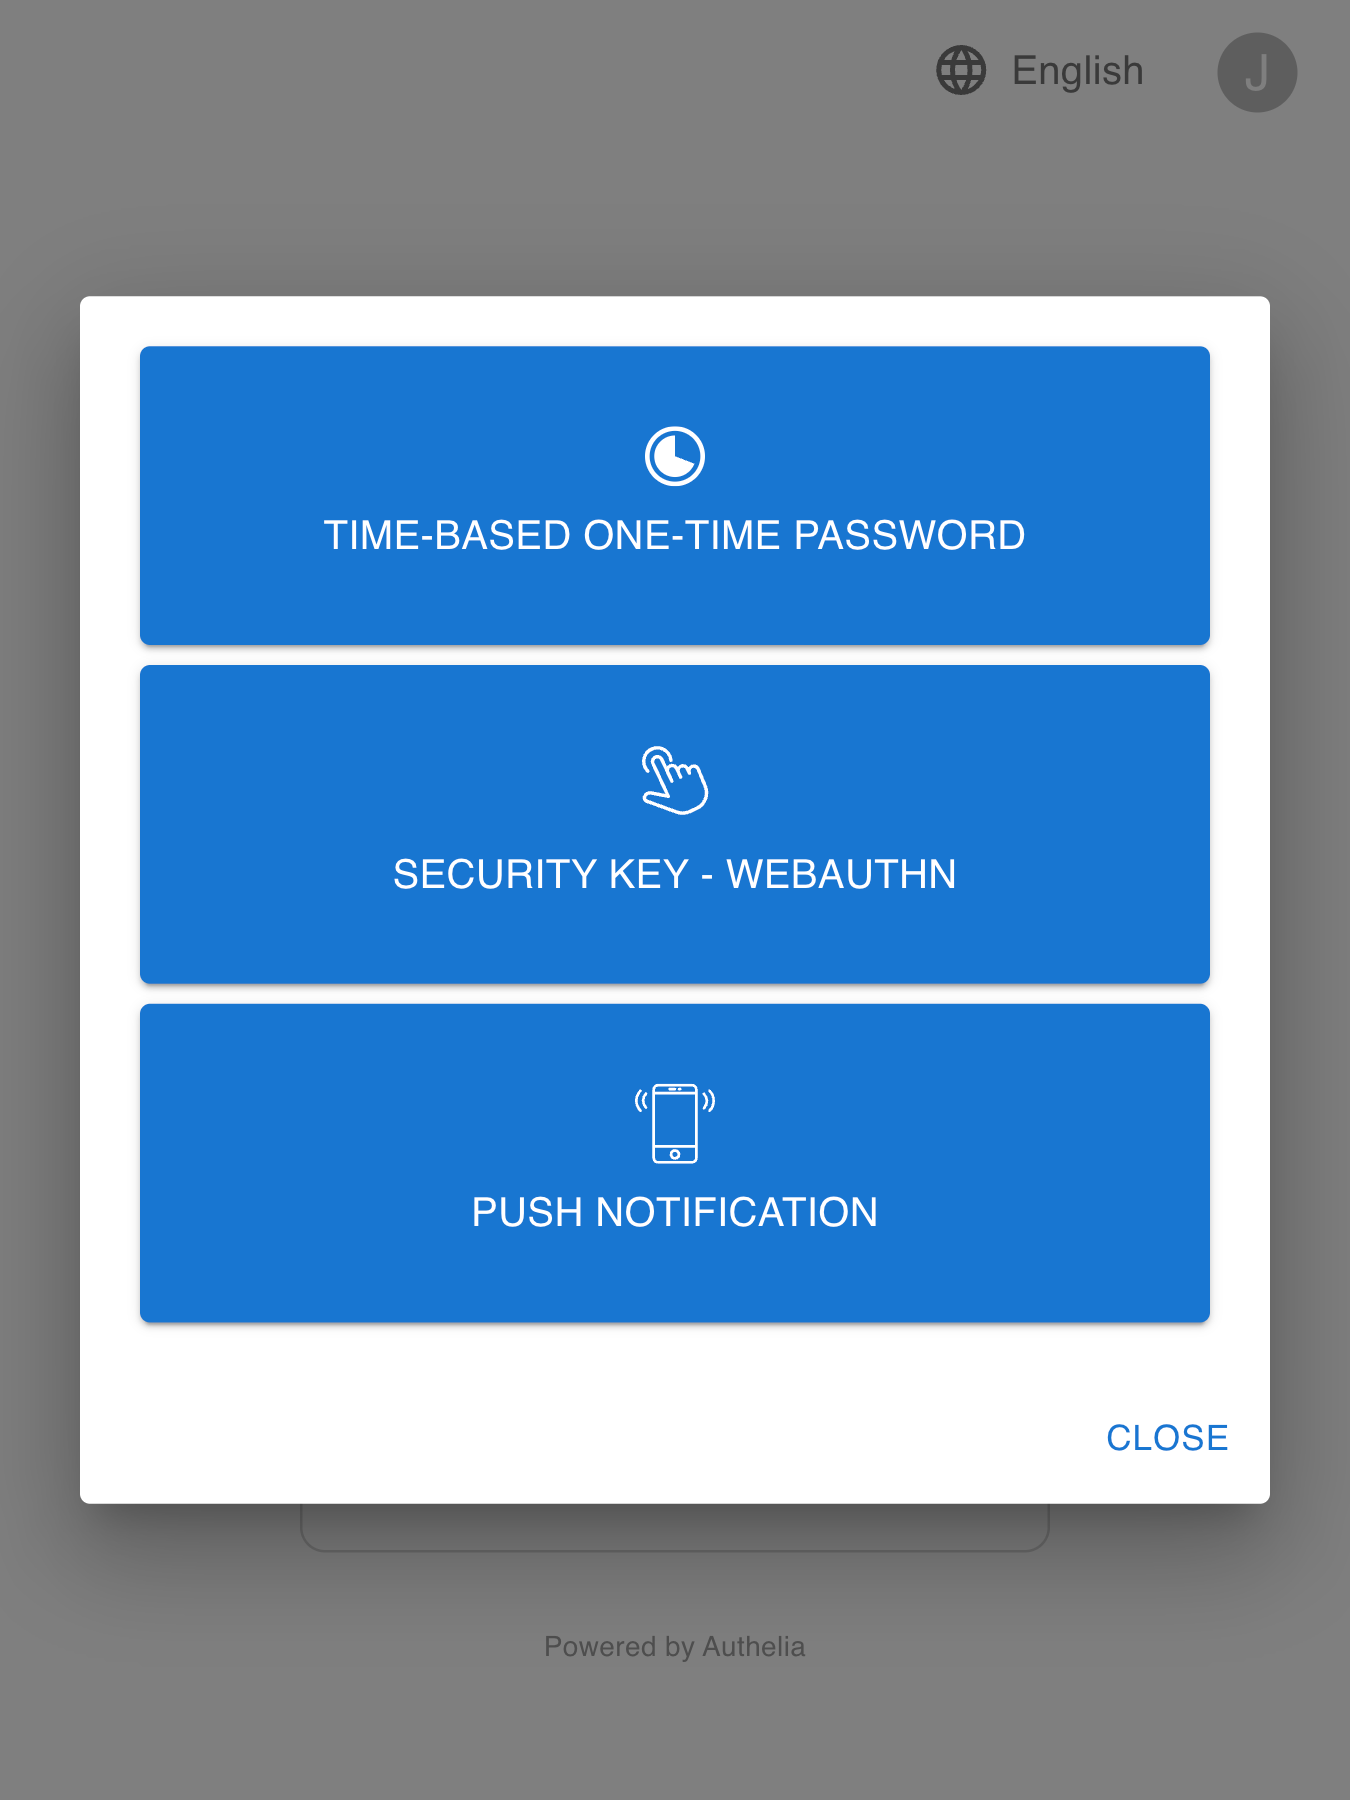
Authelia is a self-hosted identity and access management server with a web login portal, so users authenticate once and their session then gates every application sitting behind your reverse proxy. Second factors cover time-based one-time passwords, WebAuthn security keys, passkeys and Duo mobile push, while the first factor comes from an LDAP directory or a YAML user file. It is OpenID Certified as an OpenID Connect 1.0 provider and also handles OAuth 2.0, and access decisions come from granular rules matching domain, user, group membership, request URI and method, each ending in a one-factor, two-factor or deny outcome. Guard rails built in include lockout after repeated failed logins, email identity validation before a second-factor device is registered, email-driven password reset for both LDAP and internal accounts, and post-quantum cryptography readiness. You deploy it beside Traefik, NGINX, Caddy, Envoy, HAProxy or Skipper: official containers are published on Docker Hub and GHCR, the repository ships lite and local compose bundles, a beta Helm chart covers Kubernetes, and bare-metal installs come from the AUR, an APT repository, FreeBSD Ports or release binaries and .deb packages. State is kept in PostgreSQL, MySQL or SQLite3, Redis is recommended for sessions once you go live, and the whole thing is configured through a static YAML file rather than a GUI, with secrets optionally injected as environment variables or secret files. The daemon listens on 9091 and normally leaves TLS to the proxy. The maintainers describe it as under active development with occasional breaking changes, so pin a version tag and read the release notes before upgrading.
authelia alternatives
 OAuth2 ProxyOpen-source, self-hosted auth proxy that puts OAuth2/OIDC sign-in in front of web apps, with email/domain/group checks and Redis sessions.CompareOAuth2 Proxy with authelia
 voidauthOpen-source SSO for homelabs: an OIDC provider, reverse-proxy forward-auth, optional read-only LDAP, and user management with invitations, passkeys and MFA.Comparevoidauth with authelia
 TeleportSelf-hosted open-source platform replacing VPNs with short-lived certificates, SSO, MFA, RBAC, and session audit across SSH, Kubernetes, databases, and web apps.CompareTeleport with authelia
 PomeriumOpen-source self-hosted identity-aware reverse proxy that gates private web apps, SSH and TCP services through OIDC sign-in and per-request access policy.ComparePomerium with authelia
 LLDAPlldap is a self-hosted, open-source lightweight LDAP server with web UI, supporting SQLite/MySQL/PostgreSQL, simpler than OpenLDAP.CompareLLDAP with authelia
 DexOpen-source, self-hosted OIDC and OAuth 2.0 identity service that fronts LDAP, SAML, GitHub, Google and other IdPs, so every app just speaks OpenID Connect.CompareDex with authelia
 FusionAuthFusionAuth is a self-hosted CIAM platform for auth, authorization, and user management with SSO, MFA, passkeys, and social login. Free Community edition available.CompareFusionAuth with authelia
 logtoSelf-hosted, open-source auth server for SaaS and AI apps: OIDC, OAuth 2.1 and SAML with passwordless, social login, MFA, RBAC and multi-tenant organizations.Comparelogto with authelia
Should you self-host authelia?
authelia scores 81/100 on selfhost.directory (how scoring works) and ranks #1 of 3 in IAM. It has 29 659 GitHub stars, +421 in the last 30 days.
It shipped 18 stable releases in the past year. The latest, v4.39.28, came out on 17 September 2026.
Setup is moderate: expect some configuration beyond a single command. An official Docker image is available. It is Apache-2.0-licensed and written mostly in Go.
Its closest alternative on selfhost.directory is authentik (80/100, 26 356 stars). authelia scores higher overall. See authelia vs authentik side by side.
Features
- Basic authentication for one-factor endpoints
- Brute-force login regulation
- Email password reset
- Fine-grained access control rules
- Highly available deployment
- Identity validation by email
- LDAP or file user database for first factor
- Mobile push notification 2FARequires a Duo account; configured under second factor.
- Multi-factor authentication portal
- OpenID Connect 1.0 / OAuth 2.0 provider
- Passkeys (passwordless login)
- Post-Quantum Cryptography readiness
- Single sign-on via reverse proxy
- Time-based One-Time Passwords
- WebAuthn security keys
authelia README
More in IAM
 authentikSelf-hosted, open-source identity provider for SSO over OIDC, SAML, LDAP, RADIUS and SCIM, with TOTP and passkeys, configurable flows, RBAC and Helm or Compose installs.
 authgearSelf-hosted open-source CIAM and identity provider, an Auth0/Clerk alternative with passkeys, MFA, SAML SSO and RBAC, deployed via Helm.
 CasdoorSelf-hosted open-source IAM and SSO server with a web console, a built-in MCP server for AI agents, and support for more than 100 identity providers.
 defguardSelf-hosted WireGuard VPN platform bundling an identity provider, per-connection MFA, LDAP/AD sync and firewall ACLs; open-source AGPL core written in Rust.
 hankoOpen-source self-hosted authentication and user management platform with passkeys, MFA, OAuth SSO and SAML, an API-first alternative to Auth0 or Clerk.
 KanidmSelf-hosted, open-source identity management server in Rust: passkey/WebAuthn login, OAuth2/OIDC SSO, an app portal, read-only LDAPS, RADIUS, SSH keys and Unix auth.
0 comments