
Self-host Nginx-Reverse-Emby
plugin-sdk/v0.13.1Go reverse-proxy control plane with auto-HTTPS
- Stars
- 191
- Port
- 8080 (control plane HTTP API and panel)
sakullla/nginx-reverse-emby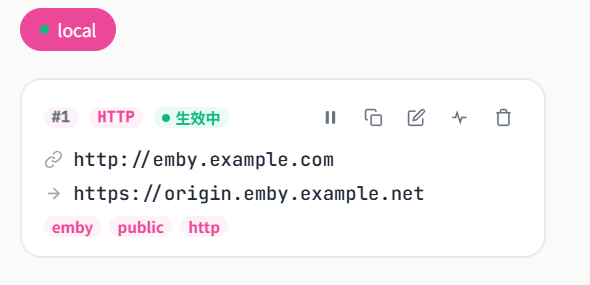
What is Nginx-Reverse-Emby?
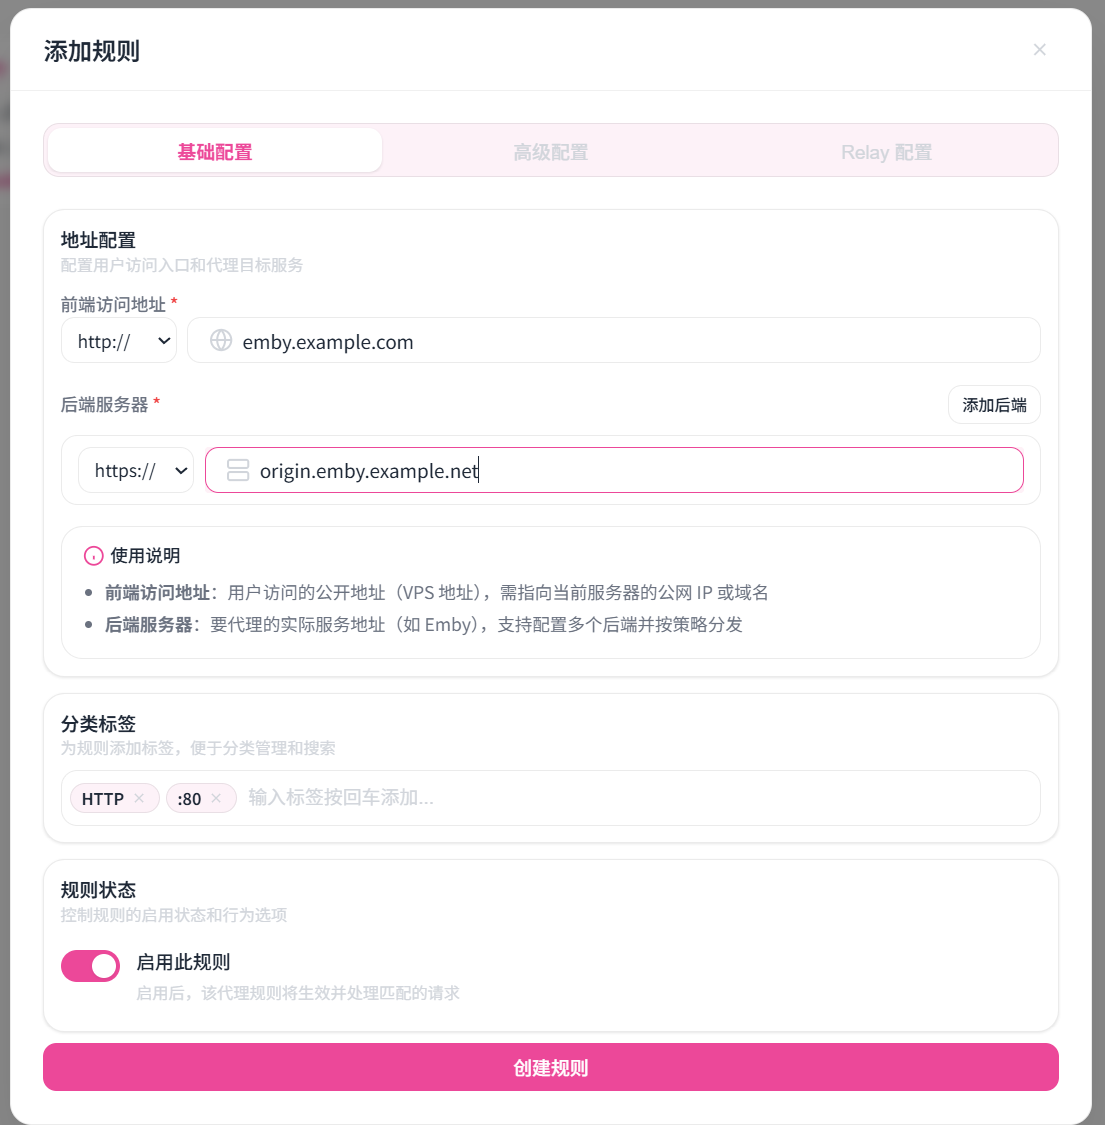
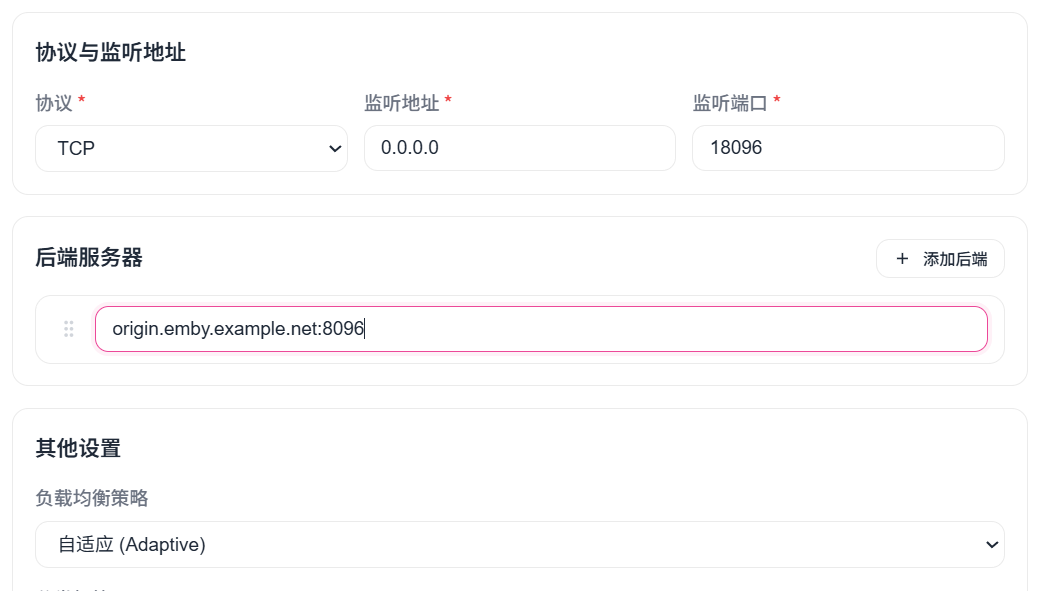
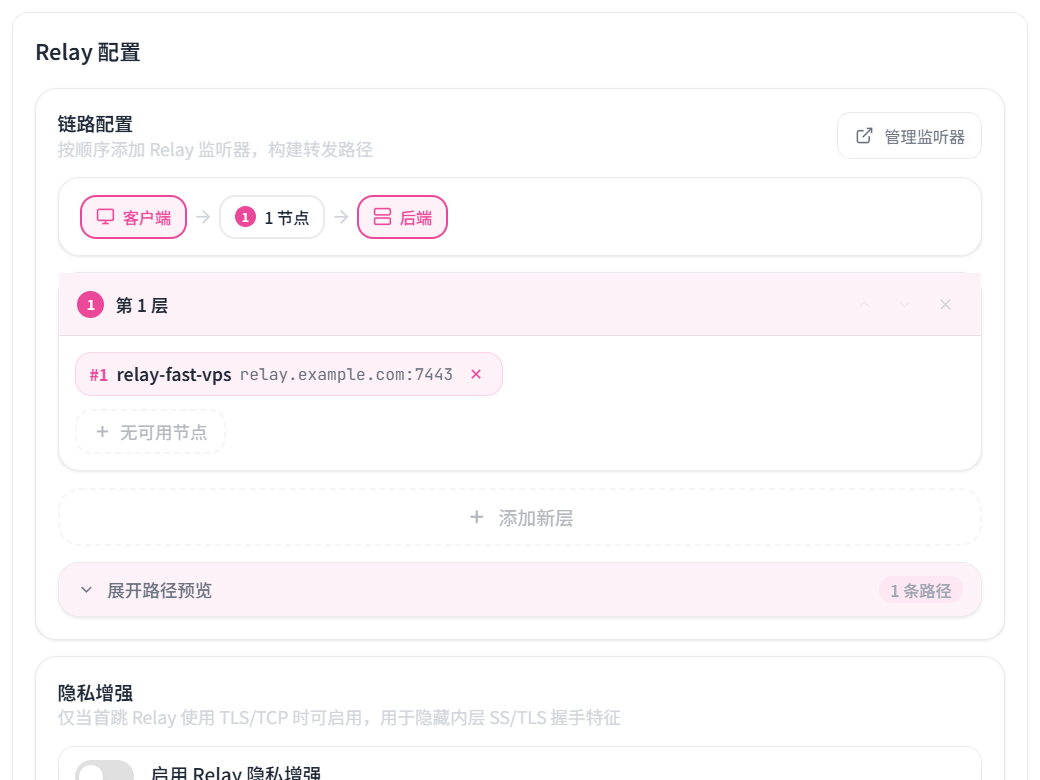
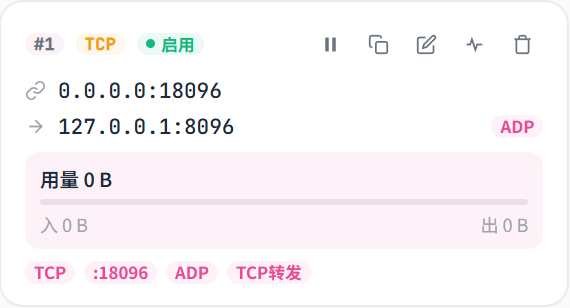
Nginx-Reverse-Emby is a pure-Go reverse proxy control plane designed for self-hosters who want to expose internal services (Emby, Jellyfin, websites, game servers, databases) to the internet safely. It replaces hand-written Nginx configs with a web UI where you create HTTP rules (domain-based, with automatic Let's Encrypt or Cloudflare DNS-01 certificates) and L4 rules (TCP/UDP port forwarding with load balancing and PROXY Protocol). A single Docker Compose file starts the control plane and a built-in local agent; additional Linux/macOS/Windows machines can join as remote agents even behind NAT, and an encrypted Relay tunnel bridges connectivity when direct access fails. Traffic statistics per interface and monthly quotas with optional blocking are built in. The panel authenticates via a long random token (API_TOKEN); there are no user accounts, OAuth, LDAP, or 2FA. Deployment is a one-line script or a manual docker-compose.yaml with a few required env vars. The project is licensed GPL-3.0 and actively developed.
Should you self-host Nginx-Reverse-Emby?
Nginx-Reverse-Emby scores 47/100 on selfhost.directory (how scoring works) and ranks #18 of 24 in Reverse Proxy. It has 191 GitHub stars.
There was no stable release in the past 12 months, so check the repository's recent activity before you rely on it.
Setup is moderate: expect some configuration beyond a single command. An official Docker image is available. It is GPL-3.0-licensed and written mostly in Go.
Its closest alternative on selfhost.directory is Traefik (87/100, 65 398 stars). It scores higher overall, so compare the two before you pick. See Nginx-Reverse-Emby vs Traefik side by side.
Features
- Automatic HTTPS (ACME)
- Backup and Restore
- DDNS public IP detection
- Hot agent upgrades
- HTTP/HTTPS reverse proxy
- Internal PKI for Relay
- L4 TCP/UDP port forwarding
- Multi-node agents
- PROXY Protocol support
- Relay encrypted tunnels
- Secret vault with key rotation
- SOCKS/HTTP egress profiles
- Stream resume for interrupted downloads
- Traffic statistics and quotas
Nginx-Reverse-Emby README
More in Reverse Proxy
 nginx-uiSelf-hosted, open-source web UI for managing Nginx: edit configs, deploy Let's Encrypt certs, tail logs, watch stats and manage clusters, with AI and MCP.
 NPMplusNPMplus is an open-source fork of nginx-proxy-manager offering hardened TLS, HTTP/3 (QUIC), crowdsec integration, and external authentication provider support.
 NPS EnhancedSelf-hosted NAT traversal and reverse proxy exposing internal services via multiple protocols with a web dashboard.
 OAuth2 ProxyOpen-source, self-hosted auth proxy that puts OAuth2/OIDC sign-in in front of web apps, with email/domain/group checks and Redis sessions.
 openresty-managerOpenResty Manager is a self-hosted web control panel for OpenResty with reverse proxy, free SSL, host terminal, file manager, Docker app store, and multi-node CDN.
 PangolinSelf-hosted, open-source SASE stack combining a WireGuard zero-trust VPN, identity-aware reverse proxy, PAM and an AI gateway; the AGPL Community Edition is free.
 PomeriumOpen-source self-hosted identity-aware reverse proxy that gates private web apps, SSH and TCP services through OIDC sign-in and per-request access policy.
 public-websites-dockerA Docker Compose guide for self-hosting static sites with Traefik, Matomo analytics, and remark42 comments — all with automatic Let's Encrypt TLS.
 rustunnelrustunnel is a self-hosted, open-source tunnel server in Rust exposing local services via encrypted WebSocket. Free managed cloud with pay-as-you-go billing and MCP.
 SafeLineSafeLine is an open-source, self-hosted WAF protecting web apps from SQL injection, XSS, and DDoS via intelligent semantic analysis. Runs as a Docker reverse proxy.
 Self-Hosted GatewayOpen-source alternative to Cloudflare Tunnels using WireGuard, NGINX, and Caddy to expose local Docker containers without port forwarding.
 sishSelf-hosted, open-source SSH server for ngrok-style HTTP, WebSocket and TCP tunnels to localhost, shipped as a Docker image or binaries.
0 comments