Self-host SafeLine
v9.4.4Self-hosted WAF with intelligent threat detection
- Stars
- 23 293
- CPU
- 1 core
- RAM
- 1 GB
- Storage
- 5 GB
- Ports
- 9443 (Management web console), 80 (HTTP reverse proxy), 443 (HTTPS reverse proxy), 65508 (Health check), 65443 (Custom page)
- Requires
- Docker, Docker Compose, PostgreSQL
chaitin/safeline-postgres:15.18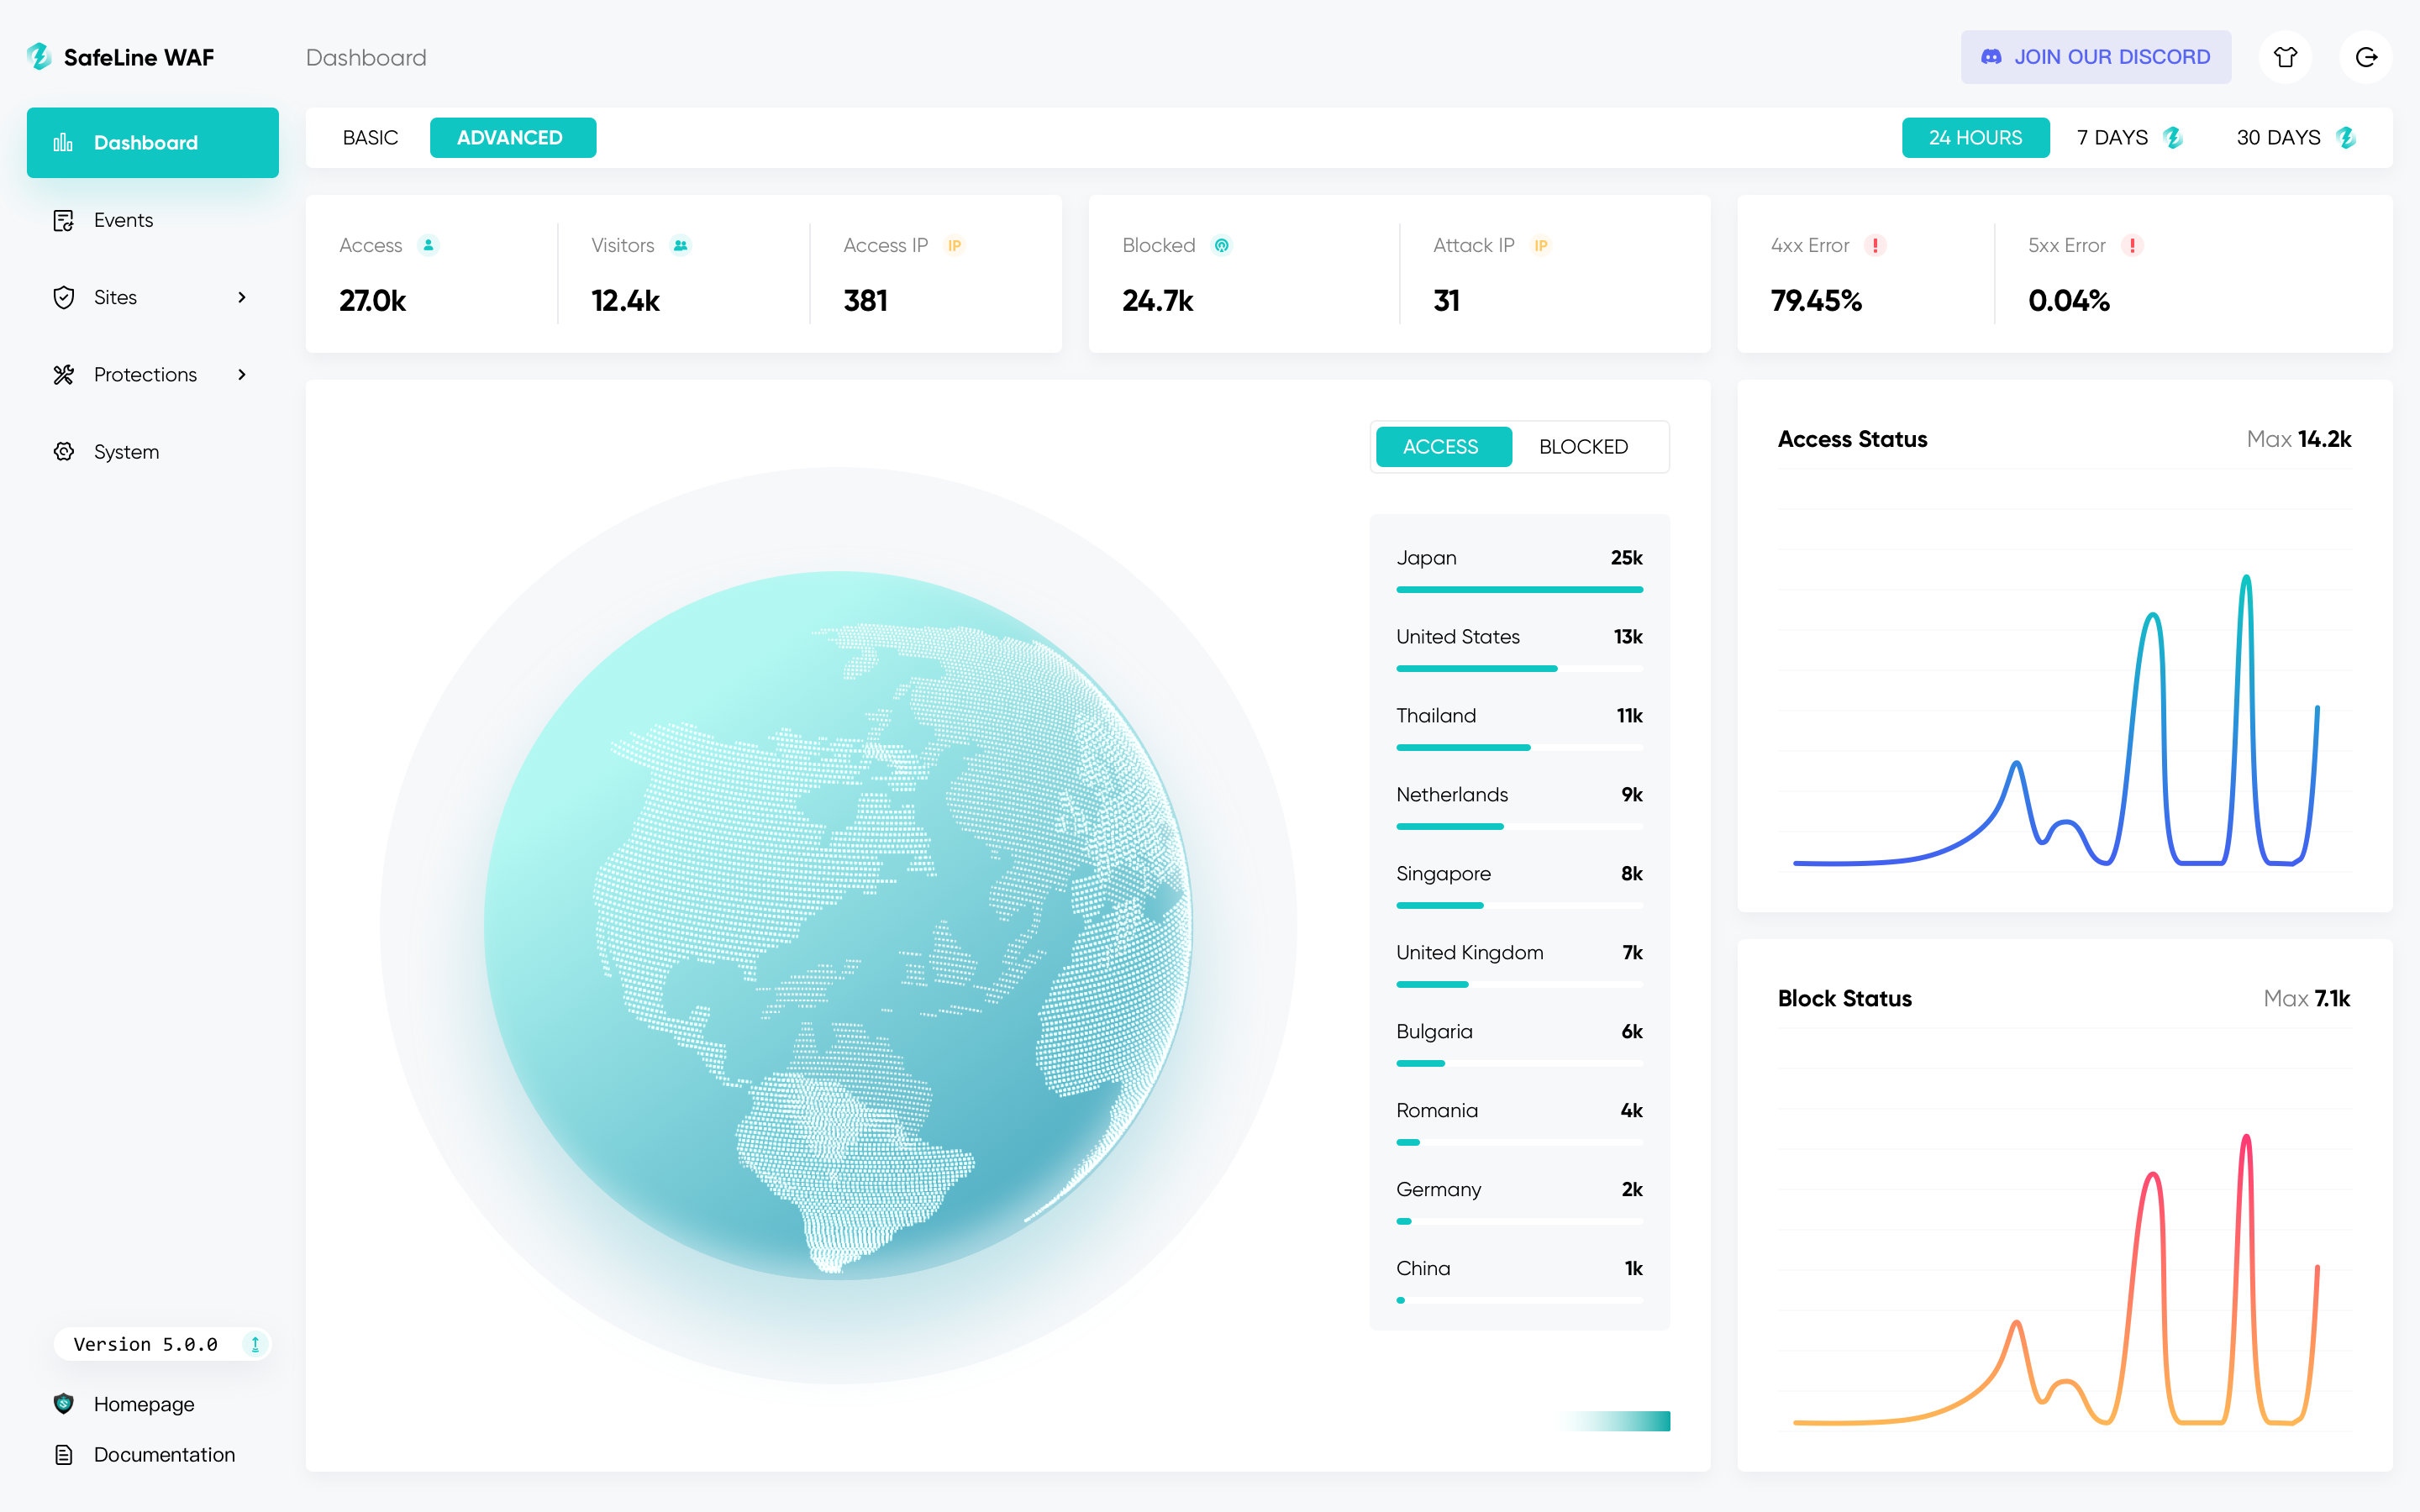
What is SafeLine?
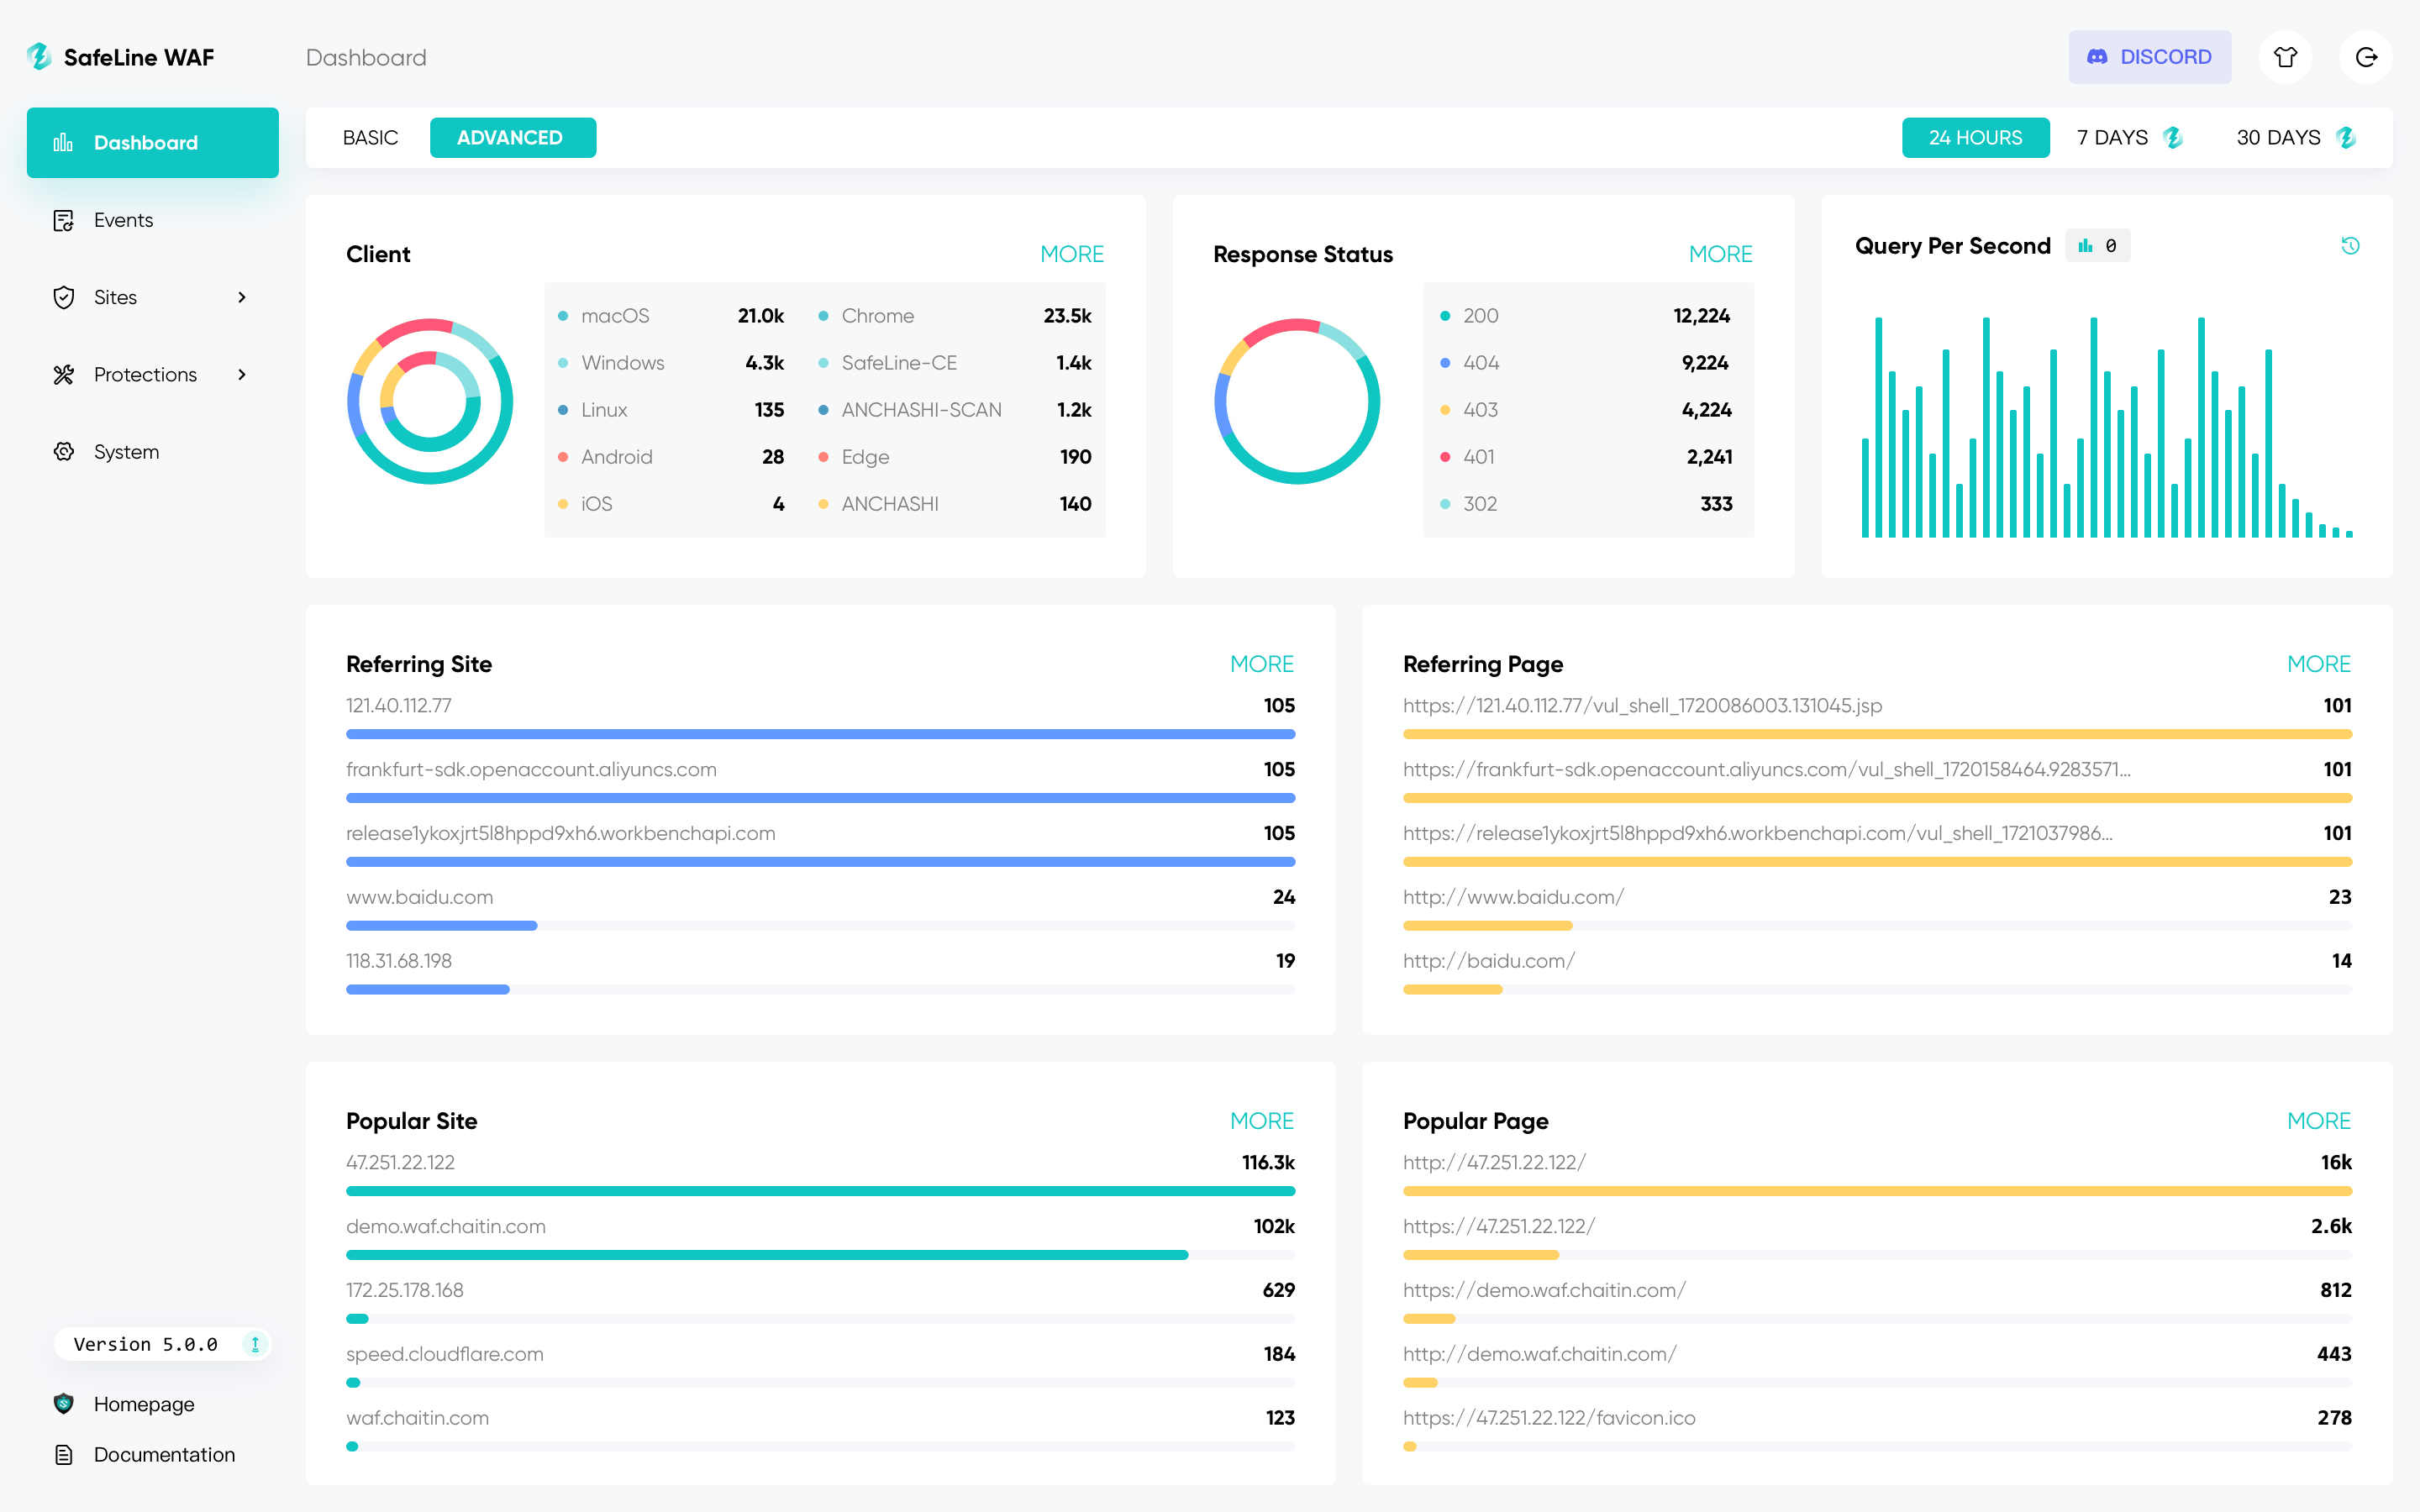
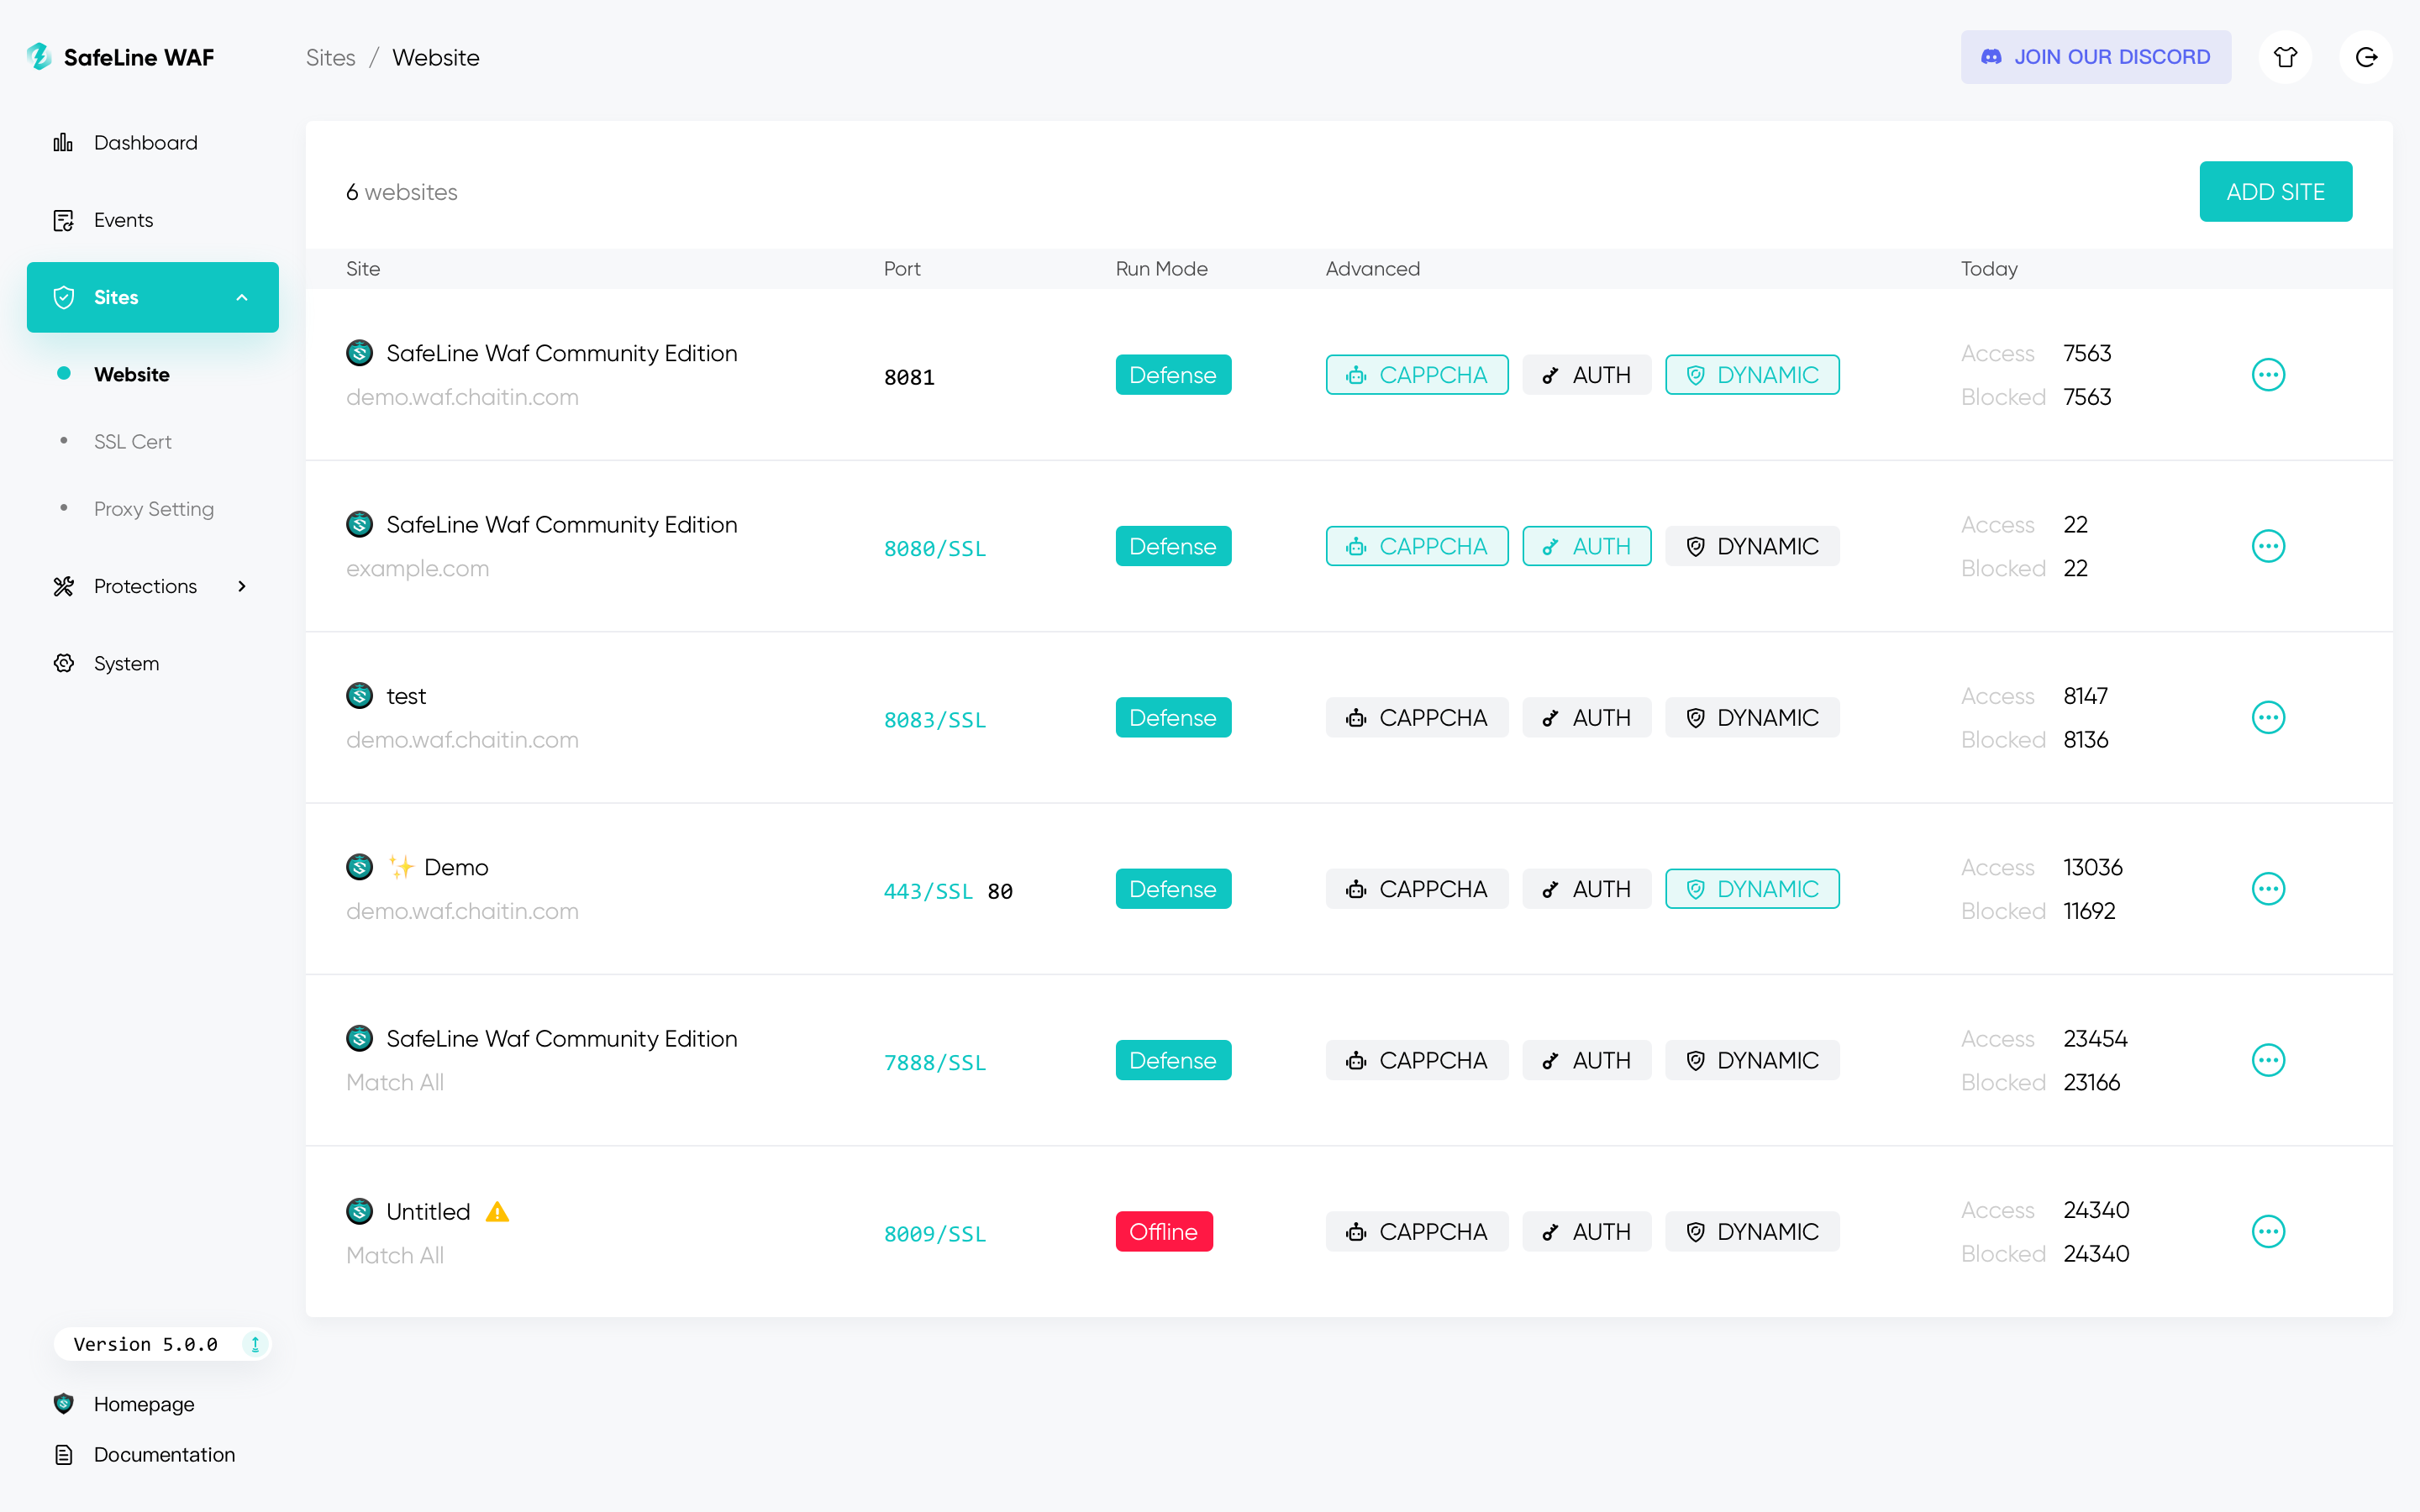
SafeLine is a self-hosted web application firewall and reverse proxy created by Chaitin Tech. It shields web applications by inspecting HTTP traffic and blocking threats such as SQL injection, cross-site scripting, code injection, command injection, XXE, SSRF, path traversal, brute-force attempts, and HTTP flood DDoS attacks. The system uses an intelligent semantic analysis engine for accurate detection, along with rate limiting, CAPTCHA-based bot challenges, password authentication gates, and dynamic encryption of HTML and JavaScript on each request. It runs as a Docker Compose stack with separate containers for the Tengine-based proxy, management API, and PostgreSQL database, exposing a web console on port 9443. A free Personal Edition is available alongside paid Lite, Pro, and Ultimate tiers that add geo-blocking, log export, notifications, load balancing, high-availability sync, custom block pages, and multi-user management. The project reports over 700,000 deployments worldwide.
SafeLine alternatives
 BunkerWeb🛡️ Open-source and cloud-native Web Application Firewall (WAF)CompareBunkerWeb with SafeLine
 nginx-loveSelf-hosted open-source platform for managing Nginx reverse proxies with ModSecurity WAF, Let's Encrypt SSL, load balancing, JA4 bot detection, and multi-user RBAC.Comparenginx-love with SafeLine
 TRAWLA self-hosted, open-source scraping engine that bypasses JavaScript challenges and CAPTCHAs using an adaptive tier engine with HTTP-first approach and MCP support.CompareTRAWL with SafeLine
 crowdsecSelf-hosted, open-source intrusion detection and web-app firewall that reads your logs, bans abusive IPs, and shares a crowdsourced blocklist across users.Comparecrowdsec with SafeLine
 pwnflowPwnflow is a self-hosted, open-source mind-mapping platform for cybersecurity professionals to visualize and track security testing methodologies with AI assistance.Comparepwnflow with SafeLine
 web-checkOpen-source, self-hosted OSINT tool that runs 44 checks on any URL - DNS, TLS, headers, ports, CVEs, trackers - through a web UI or plain API.Compareweb-check with SafeLine
 checkmateSelf-hosted, open-source uptime and infrastructure monitor: HTTP, ping, DNS, Docker and gRPC checks with incidents, status pages and Slack or email alerts.Comparecheckmate with SafeLine
 Middleware ManagerA self-hosted web UI for managing Traefik middlewares, custom services, plugins, and mTLS — compatible with Pangolin or Traefik directly.CompareMiddleware Manager with SafeLine
Should you self-host SafeLine?
SafeLine scores 80/100 on selfhost.directory (how scoring works) and ranks #1 of 3 in Web Application Firewall. It has 23 293 GitHub stars, +560 in the last 30 days.
It shipped 11 stable releases in the past year. The latest, v9.4.4, came out on 11 November 2026. New versions land roughly every 3 weeks.
Setup is moderate: expect some configuration beyond a single command. An official Docker image is available. It is GPL-3.0-licensed and written mostly in Go.
Its closest alternative on selfhost.directory is UUSEC WAF (59/100, 1 723 stars). SafeLine scores higher overall. See SafeLine vs UUSEC WAF side by side.
Features
- Anti-Bot Challenge
- Attack Log ExportAvailable in Lite and Pro editions only
- Authentication Challenge
- Custom Blocking PagesAvailable in Pro edition only
- Discord/Telegram notificationsAvailable in Lite and Pro editions only
- Dynamic Protection
- Geo-blockingAvailable in Lite and Pro editions only
- HTTP Flood DDoS Protection
- Master-Slave Node SyncAvailable in Pro edition only
- Multi-User ManagementAvailable in Pro edition only
- Rate Limiting
- Semantic Analysis Engine
- Upstream load balancingAvailable in Pro edition only
- Web Attack Protection
- Websocket Support
SafeLine README

🏠 Website | 📖 Docs | 🔍 Live Demo | 🙋♂️ Discord | 中文版
FAQ
How to export SafeLine logs to external systems?
Use Fluentd with the fluent-plugin-sql to read from the PostgreSQL database and forward logs via syslog to external systems.
Can SafeLine and business services be deployed on the same machine?
Yes, they can be deployed on the same machine, but it is not recommended as the machine load will be higher compared to separate deployments.
How to enable access logs in SafeLine?
Modify the nginx.conf file in resources/nginx directory, uncomment line 98 and delete line 99, then run 'docker exec safeline-tengine nginx -t' and 'docker exec safeline-tengine nginx -s reload'.
How to reset the admin account password?
Run 'docker exec safeline-mgt resetadmin' to reset the admin password.
Does SafeLine support WebSocket?
Yes, WebSocket is supported by default.
How to change the default port for SafeLine management?
Modify the MGT_PORT variable in the .env file in the installation directory and restart with docker compose down && docker compose up -d.
More in Web Application Firewall
 UUSEC WAFUUSEC WAF is a self-hosted, open-source WAF and API gateway using ML and semantic engines for zero-day detection, with HIPS/RASP defense and Lua rule engine.
 AnubisWeighs the soul of incoming HTTP requests to stop AI crawlers
- BunkerWeb🛡️ Open-source and cloud-native Web Application Firewall (WAF)
 CacheGuard-OSSelf-hosted open-source UTM appliance OS turning x86/x64 machines into complete network security gateways with firewall, VPN, WAF, antivirus, and more.
- crowdsecSelf-hosted, open-source intrusion detection and web-app firewall that reads your logs, bans abusive IPs, and shares a crowdsourced blocklist across users.
 netgoatNetGoat is an open-source, self-hosted Go reverse proxy and free Cloudflare alternative with domain routing, WAF rules, rate limiting, TLS/ACME and bot challenges.
- nginx-loveSelf-hosted open-source platform for managing Nginx reverse proxies with ModSecurity WAF, Let's Encrypt SSL, load balancing, JA4 bot detection, and multi-user RBAC.
0 comments