Self-host nginx-love
v4.01Nginx WAF management with ModSecurity and bot detection
- Stars
- 312
- RAM
- 2 GB
- Storage
- 10 GB
- Ports
- 8080 (Admin UI + /api reverse proxy), 80 (WAF / customer domains (HTTP)), 443 (WAF / customer domains (HTTPS))
- Requires
- Docker
What is nginx-love?
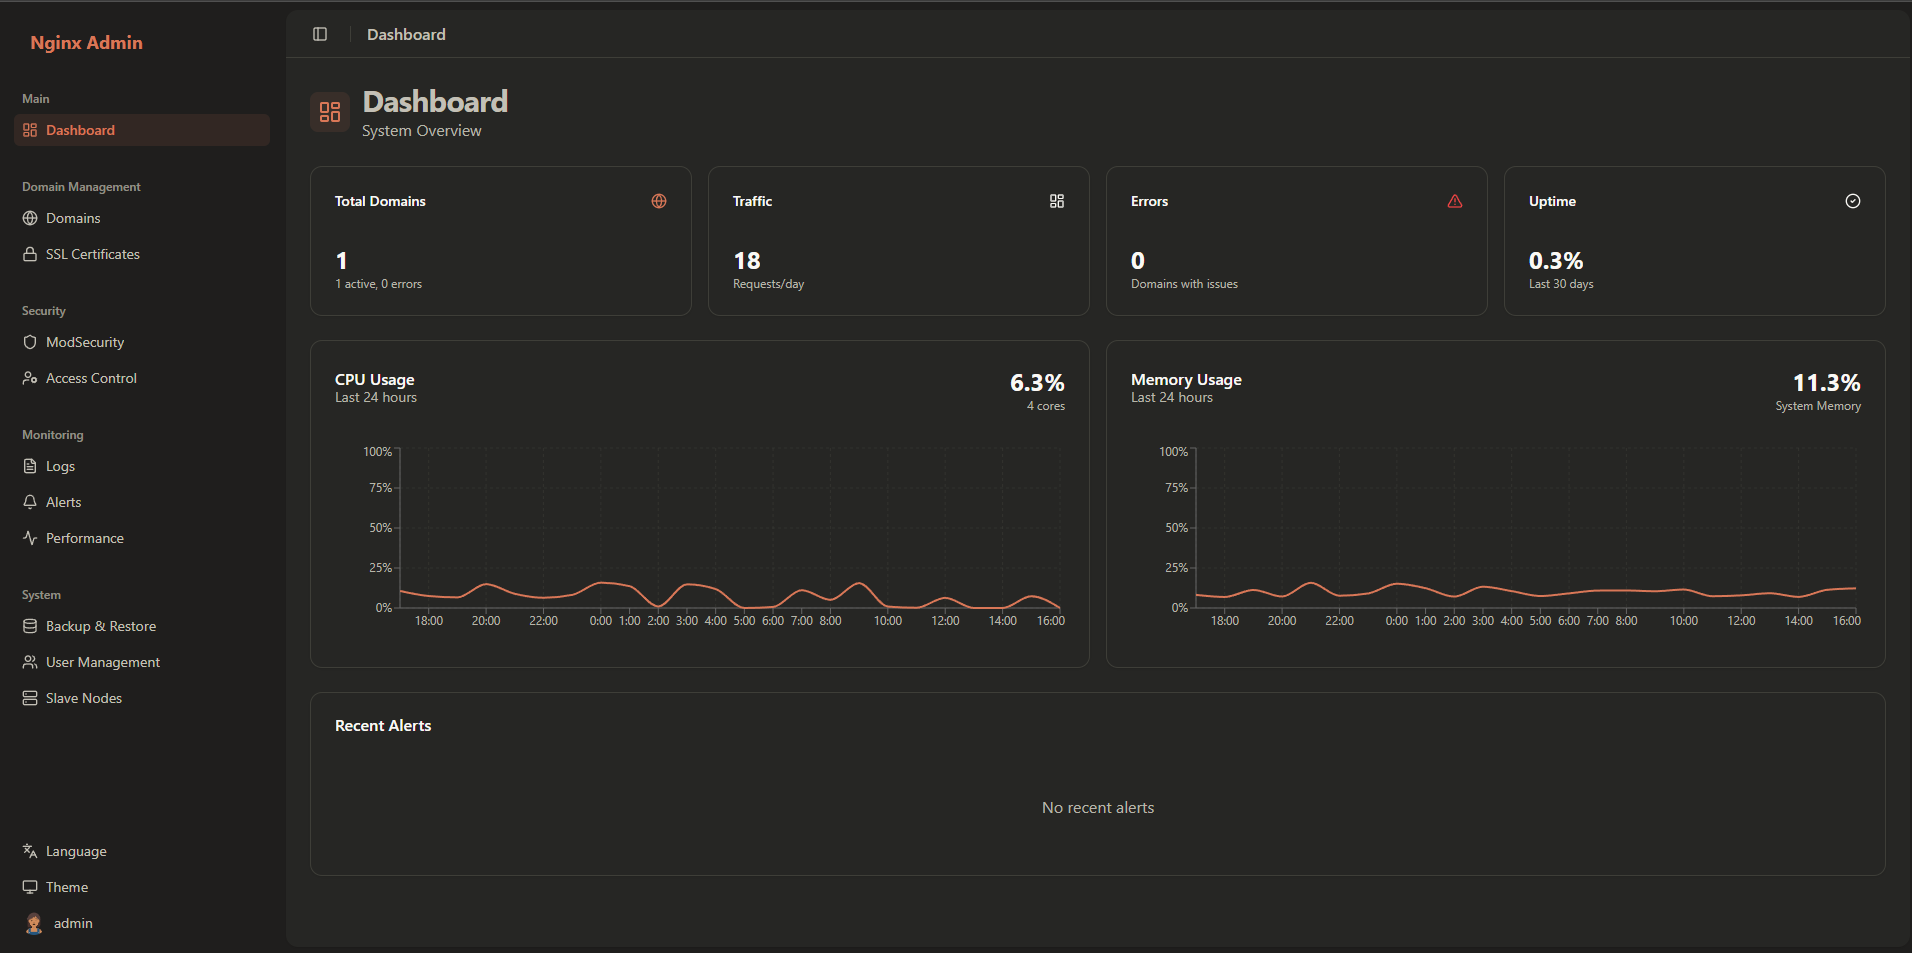
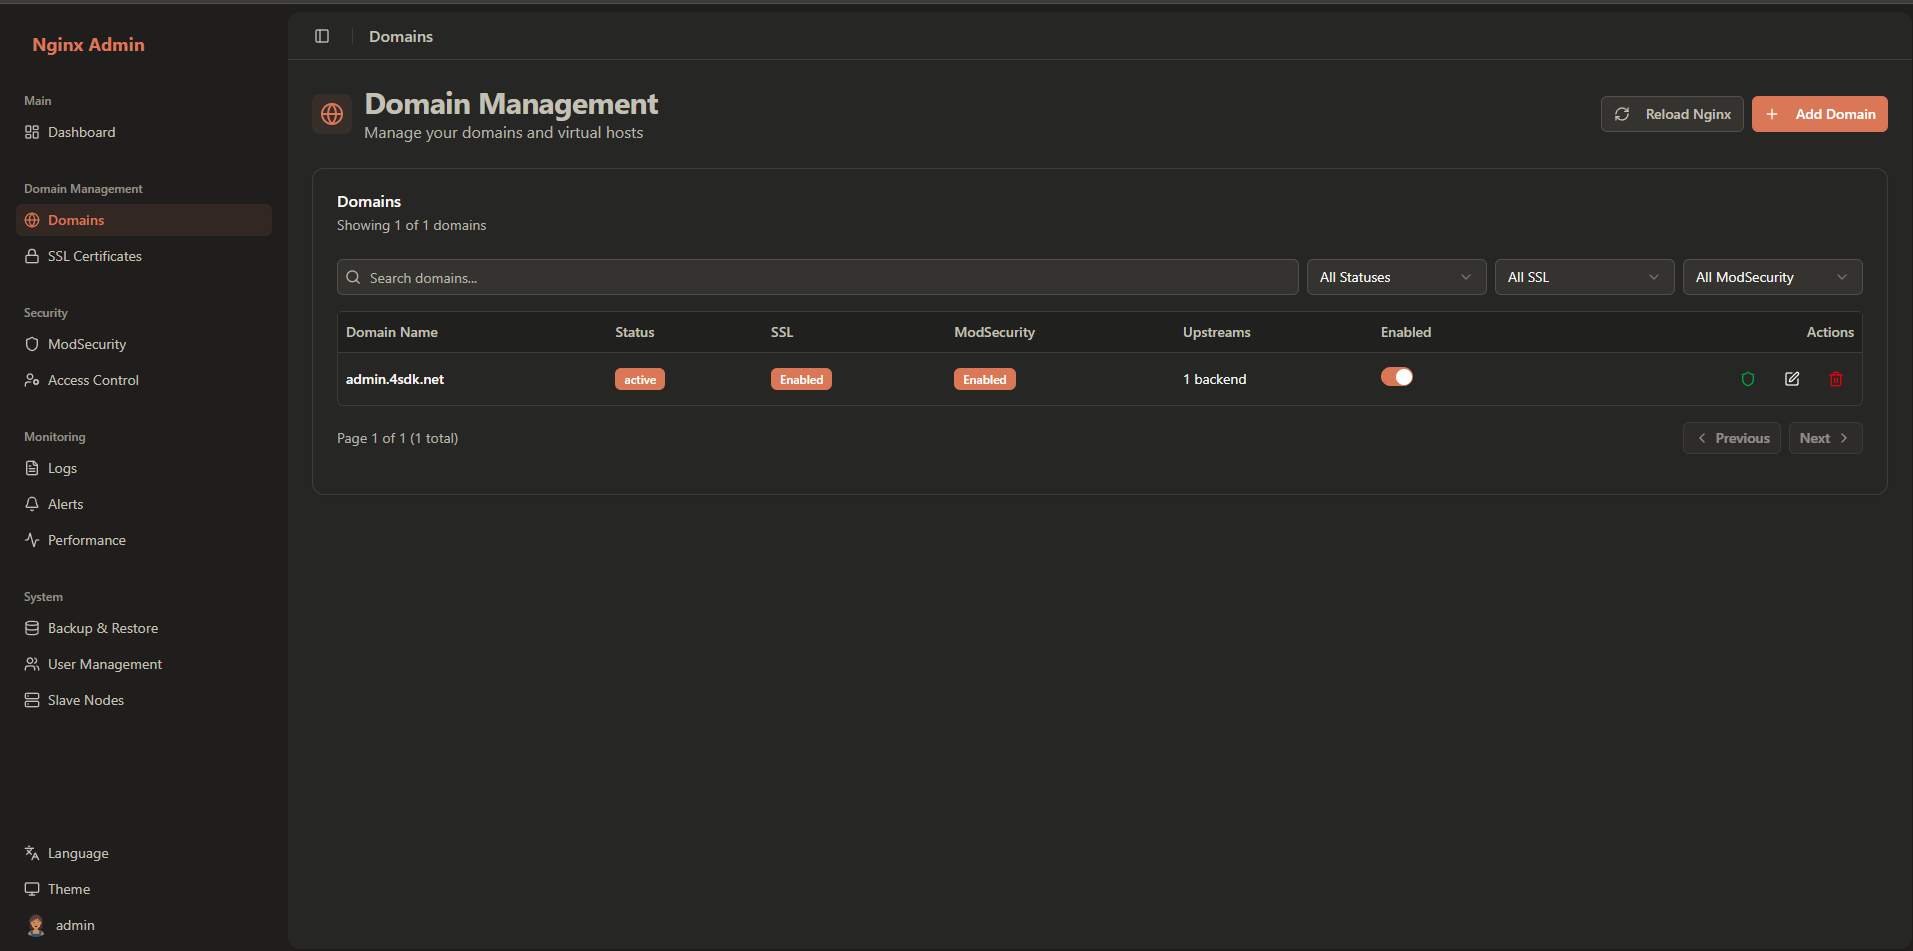
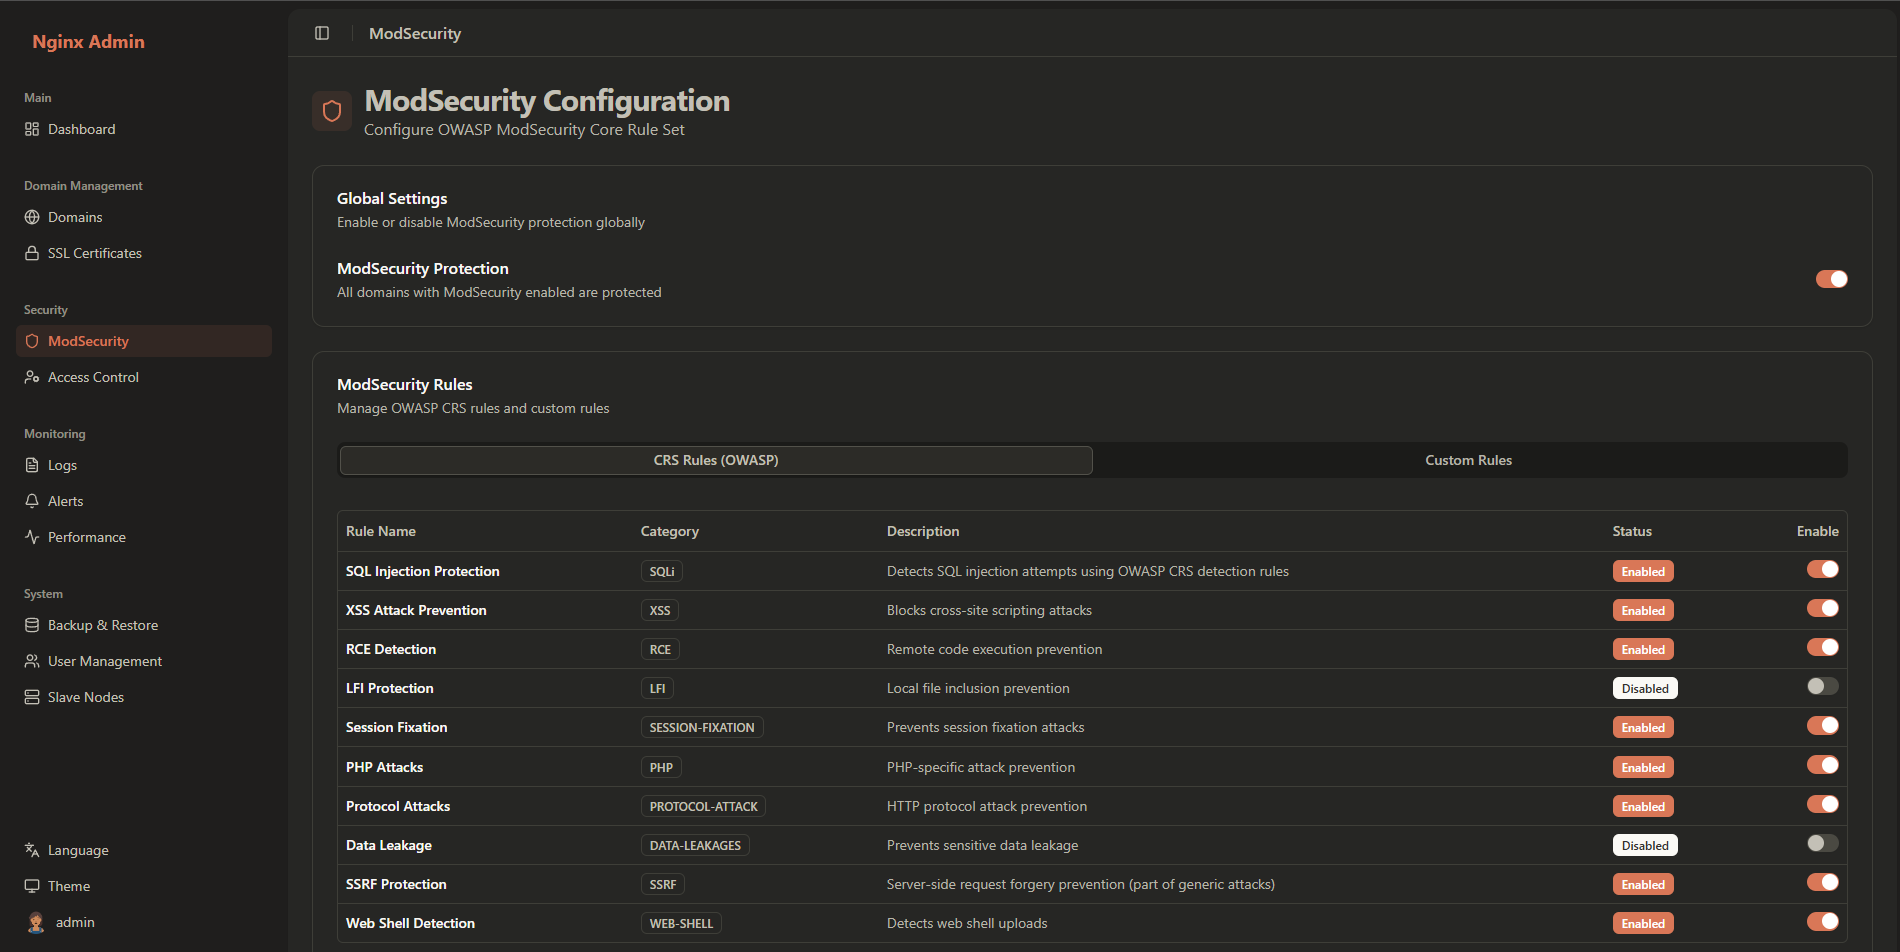
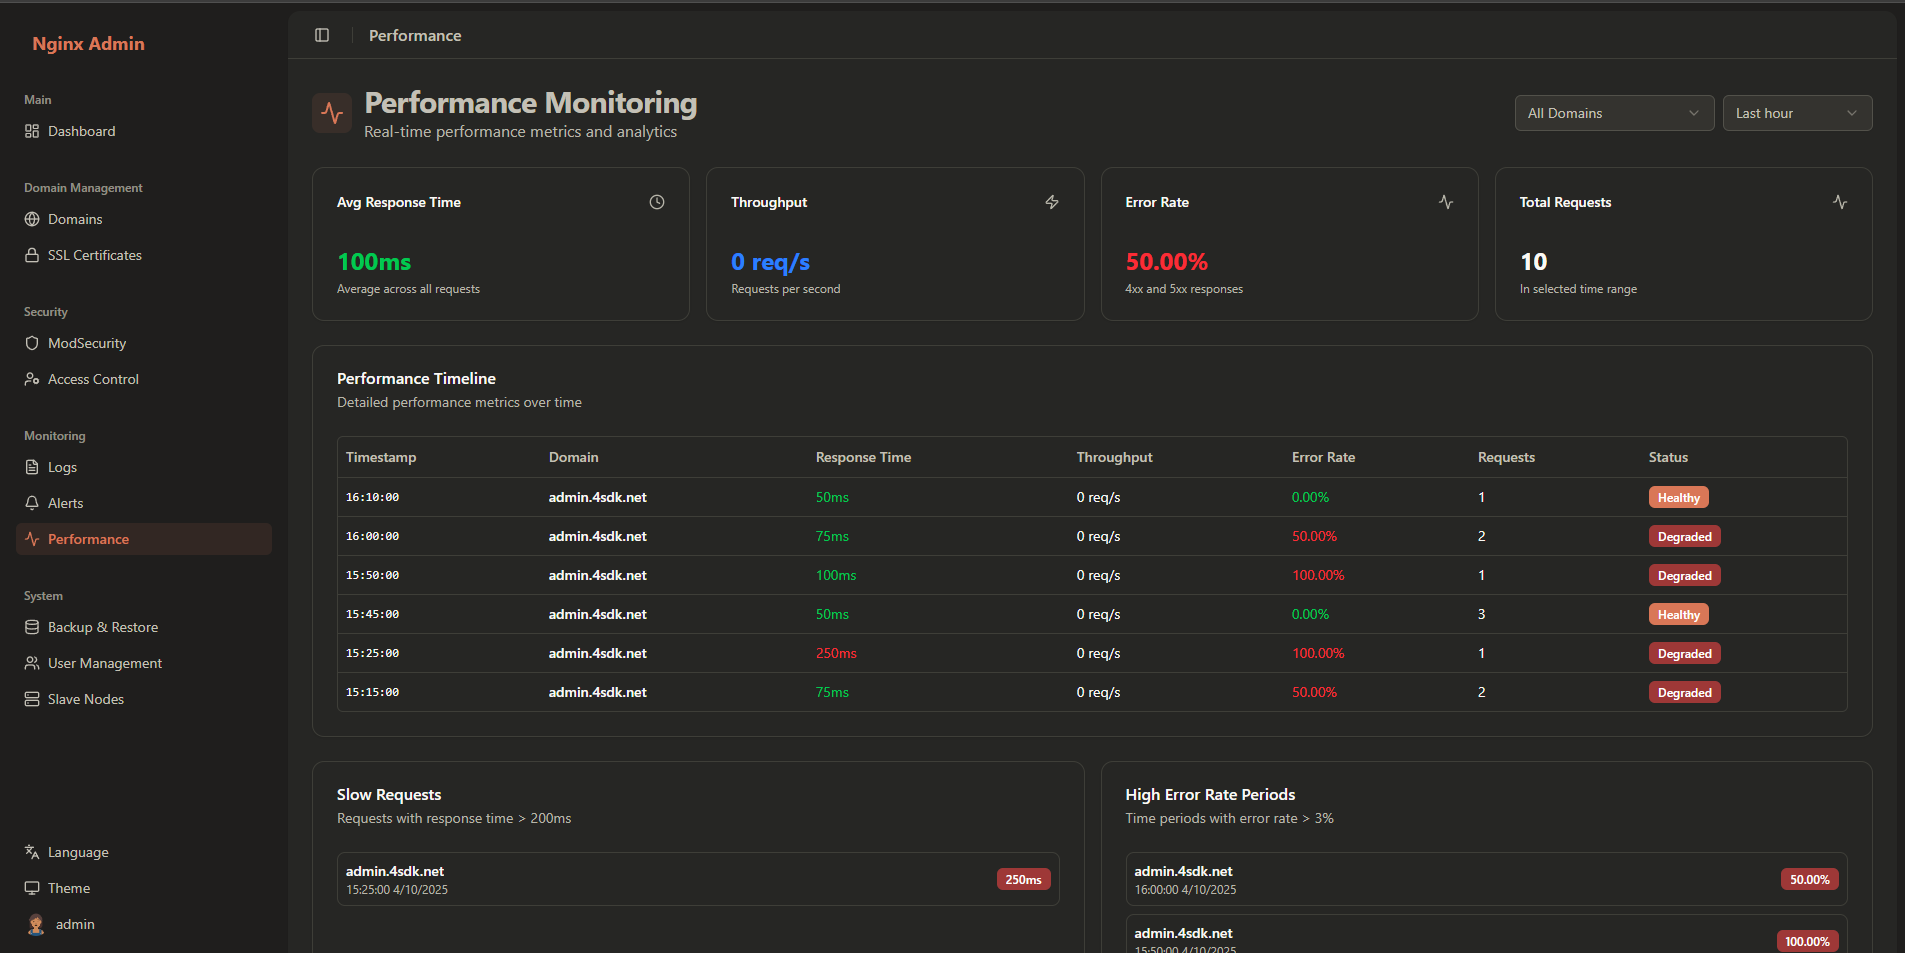
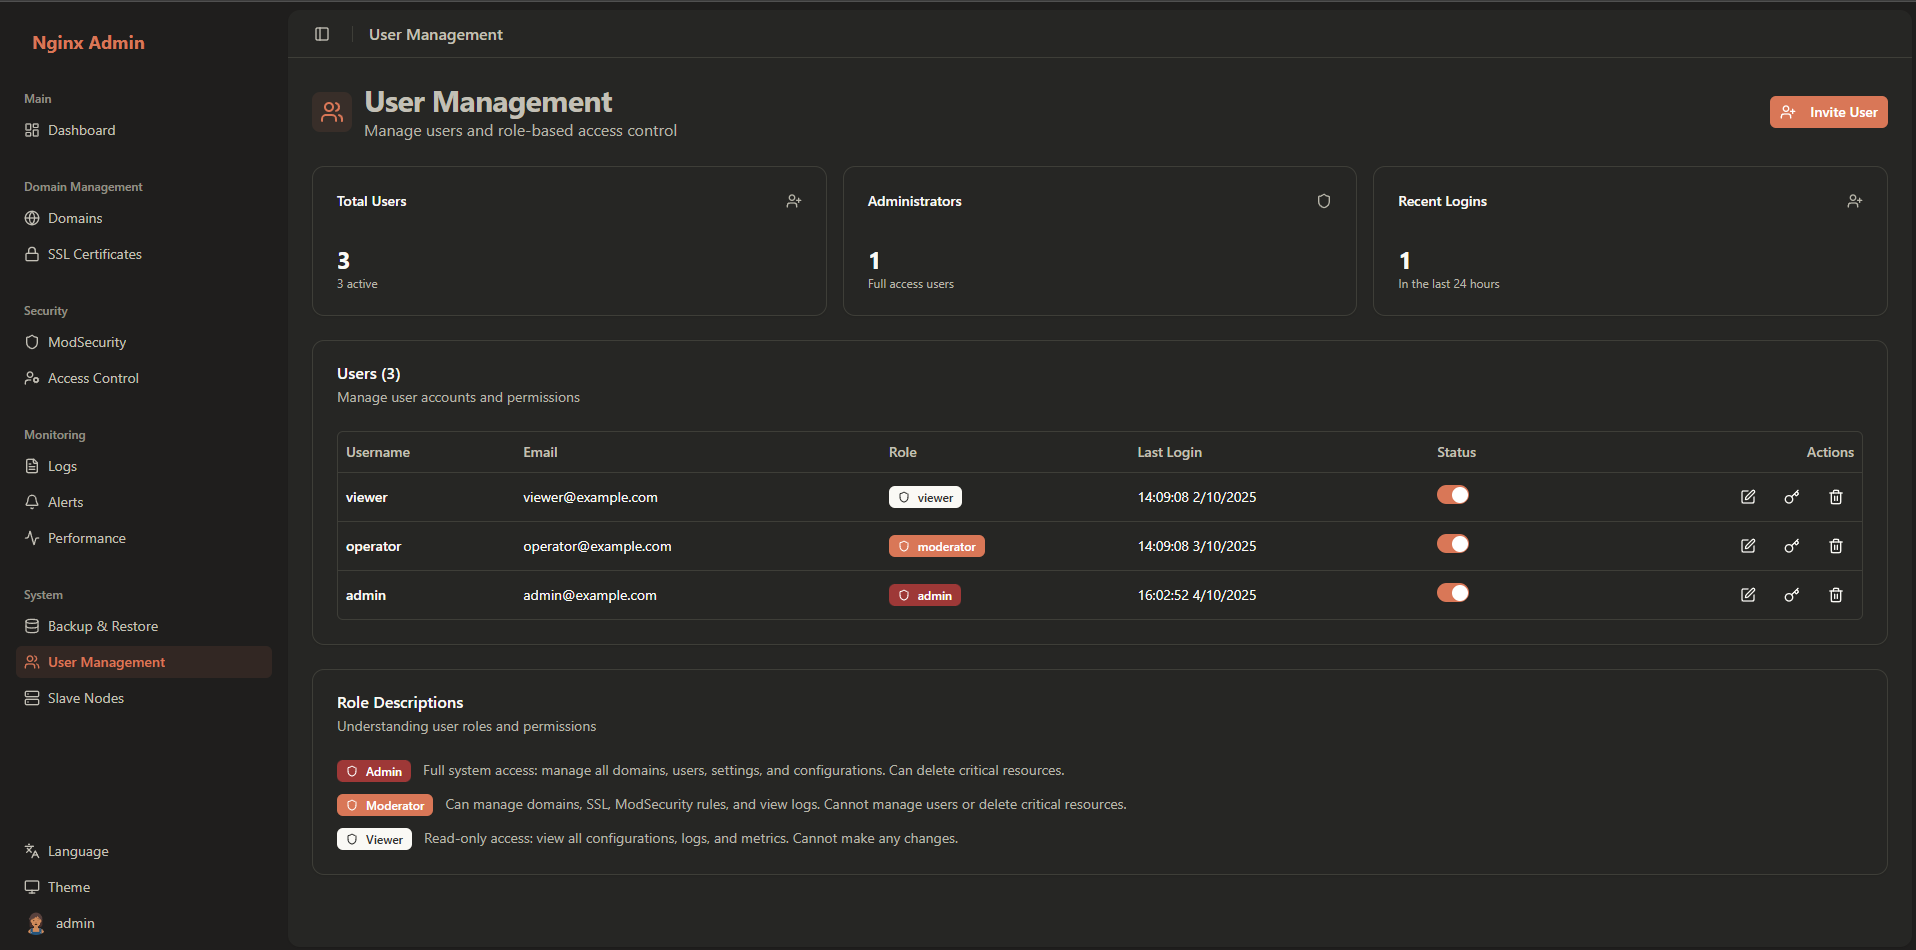
Nginx Love is a self-hosted platform for managing Nginx reverse proxies with integrated ModSecurity WAF and a web-based control panel. It handles domain configuration with upstream health checks, automates Let's Encrypt SSL certificates, and provides JA4 fingerprint-based bot detection. Access control lists support IP, GeoIP, and User-Agent filtering. The system includes performance monitoring with email and Telegram alerts, role-based access control with admin, moderator, and viewer roles, and backup with multi-node synchronization. Deployment uses Docker Compose with three containers — a frontend on port 8080, a backend combining the API with Nginx, ModSecurity, and JA4 on ports 80 and 443, and PostgreSQL 15 — plus a legacy VM option for host-native setups. The default login is admin/admin123, which must be changed on first access. The project is licensed under Apache-2.0.
Should you self-host nginx-love?
nginx-love scores 50/100 on selfhost.directory (how scoring works) and ranks #3 of 3 in Web Application Firewall. It has 312 GitHub stars.
It shipped 1 stable release in the past year. The latest, v4.01, came out on 31 October 2025.
Setup is moderate: expect some configuration beyond a single command. It is Apache-2.0-licensed and written mostly in Typescript.
Its closest alternative on selfhost.directory is SafeLine (81/100, 23 065 stars). It scores higher overall, so compare the two before you pick. See nginx-love vs SafeLine side by side.
Features
- ACL & access lists
- Backup & cluster
- Bot Manager (JA4)
- Domain Management
- Load Balancing
- ModSecurity WAF
- Monitoring & alerts
- Multi-node sync
- Multi-user RBAC
- REST API
- SSL Certificates
- Two-factor authentication
- Web UI
nginx-love README
More in Web Application Firewall
 SafeLineSafeLine is an open-source, self-hosted WAF protecting web apps from SQL injection, XSS, and DDoS via intelligent semantic analysis. Runs as a Docker reverse proxy.
 UUSEC WAFUUSEC WAF is a self-hosted, open-source WAF and API gateway using ML and semantic engines for zero-day detection, with HIPS/RASP defense and Lua rule engine.
 AnubisWeighs the soul of incoming HTTP requests to stop AI crawlers
 BunkerWeb🛡️ Open-source and cloud-native Web Application Firewall (WAF)
 CacheGuard-OSSelf-hosted open-source UTM appliance OS turning x86/x64 machines into complete network security gateways with firewall, VPN, WAF, antivirus, and more.
 crowdsecSelf-hosted, open-source intrusion detection and web-app firewall that reads your logs, bans abusive IPs, and shares a crowdsourced blocklist across users.
 netgoatNetGoat is an open-source, self-hosted Go reverse proxy and free Cloudflare alternative with domain routing, WAF rules, rate limiting, TLS/ACME and bot challenges.
0 comments