Self-host isms-builder
v1.81.2Self-hosted ISMS platform for compliance standards
- Stars
- 256
- Port
- 3000 (HTTP/HTTPS listen port)
ghcr.io/coolstartnow/isms-builder
What is isms-builder?
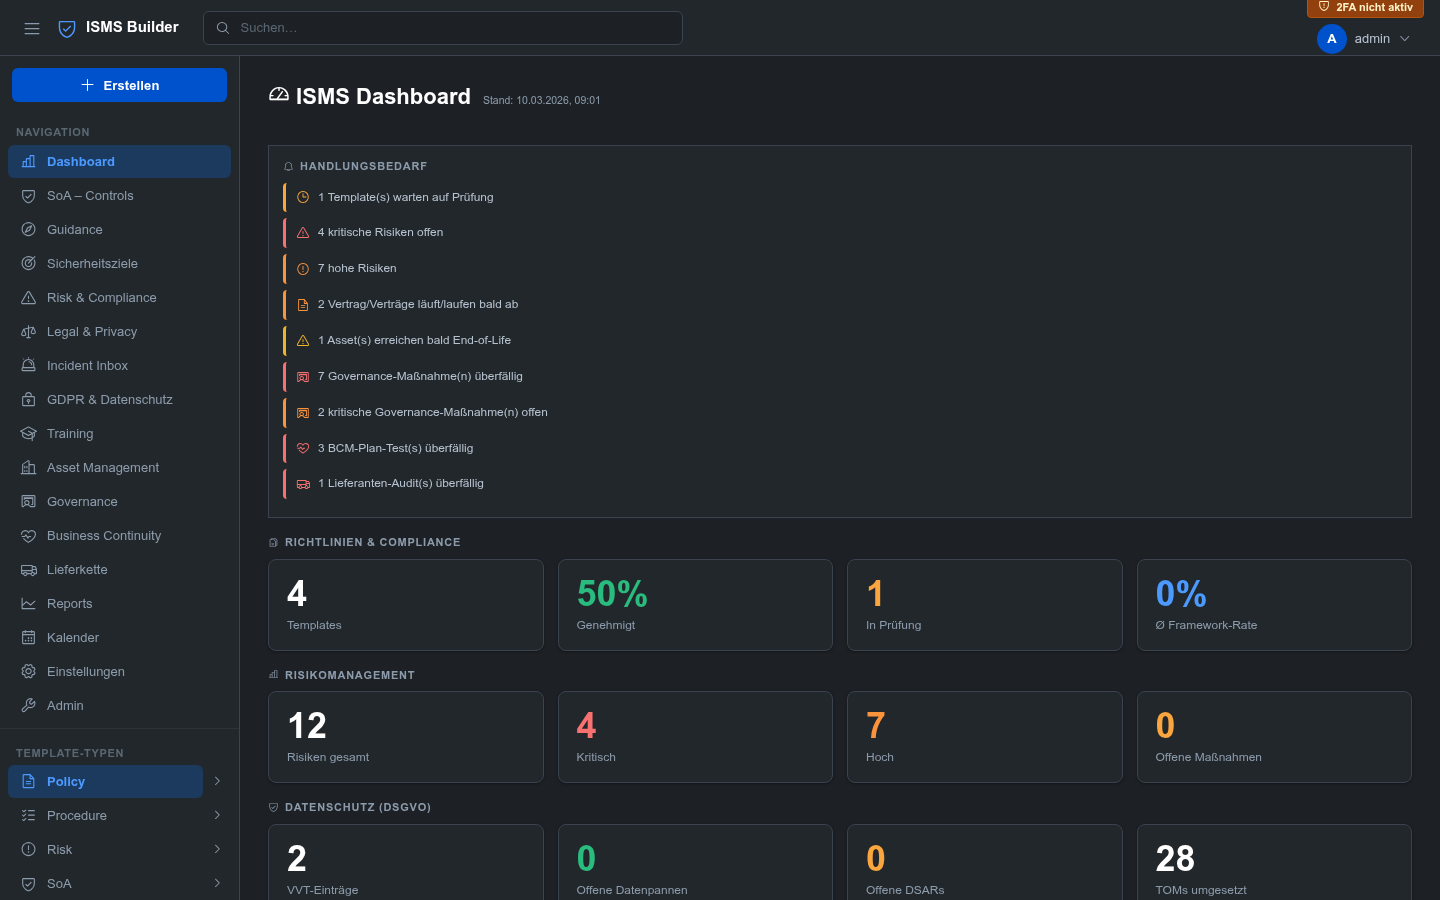
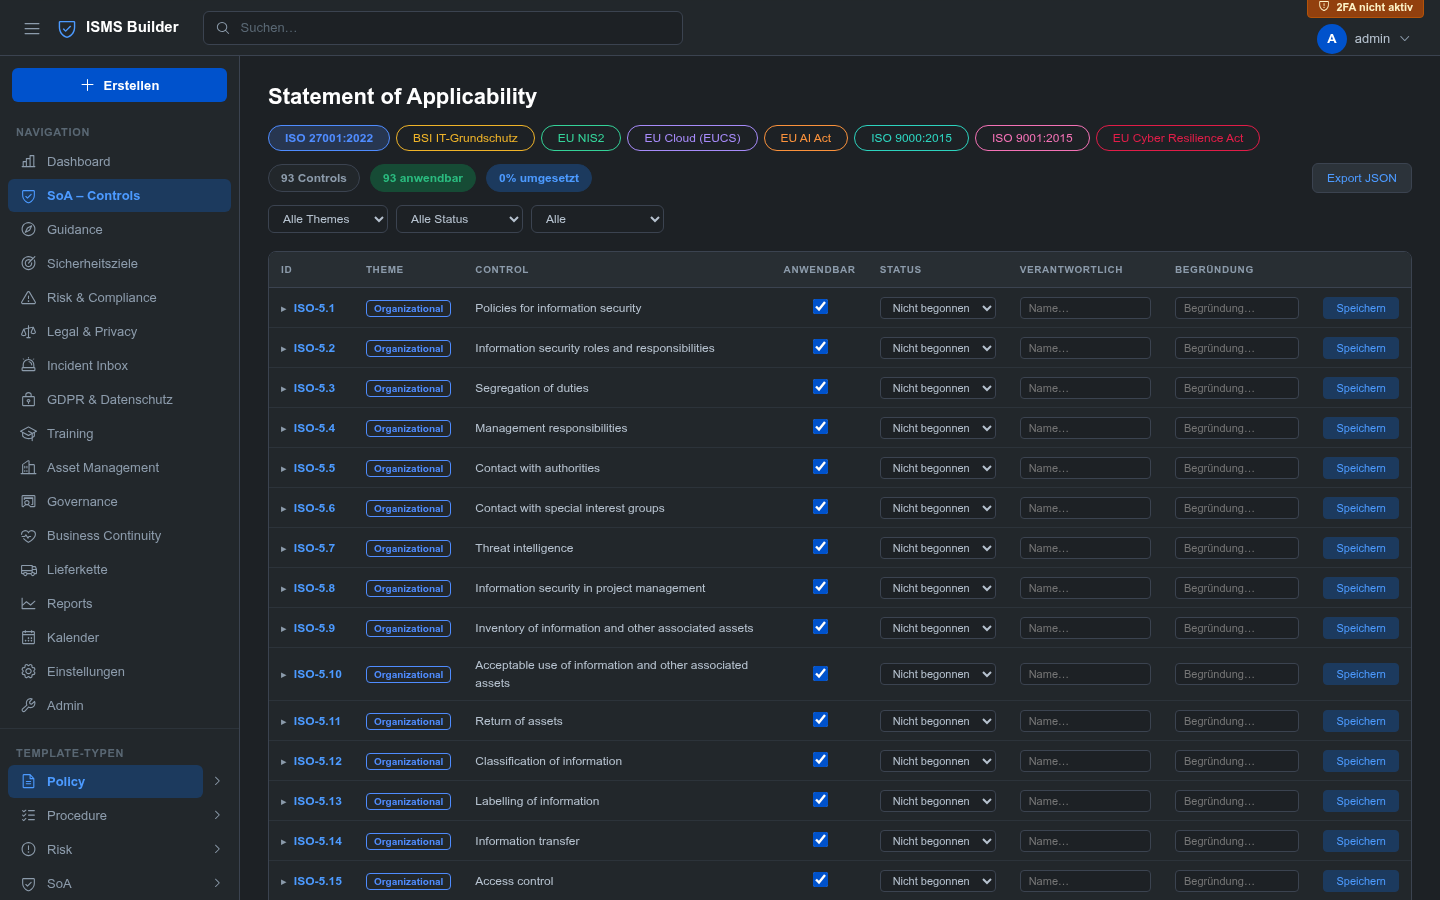
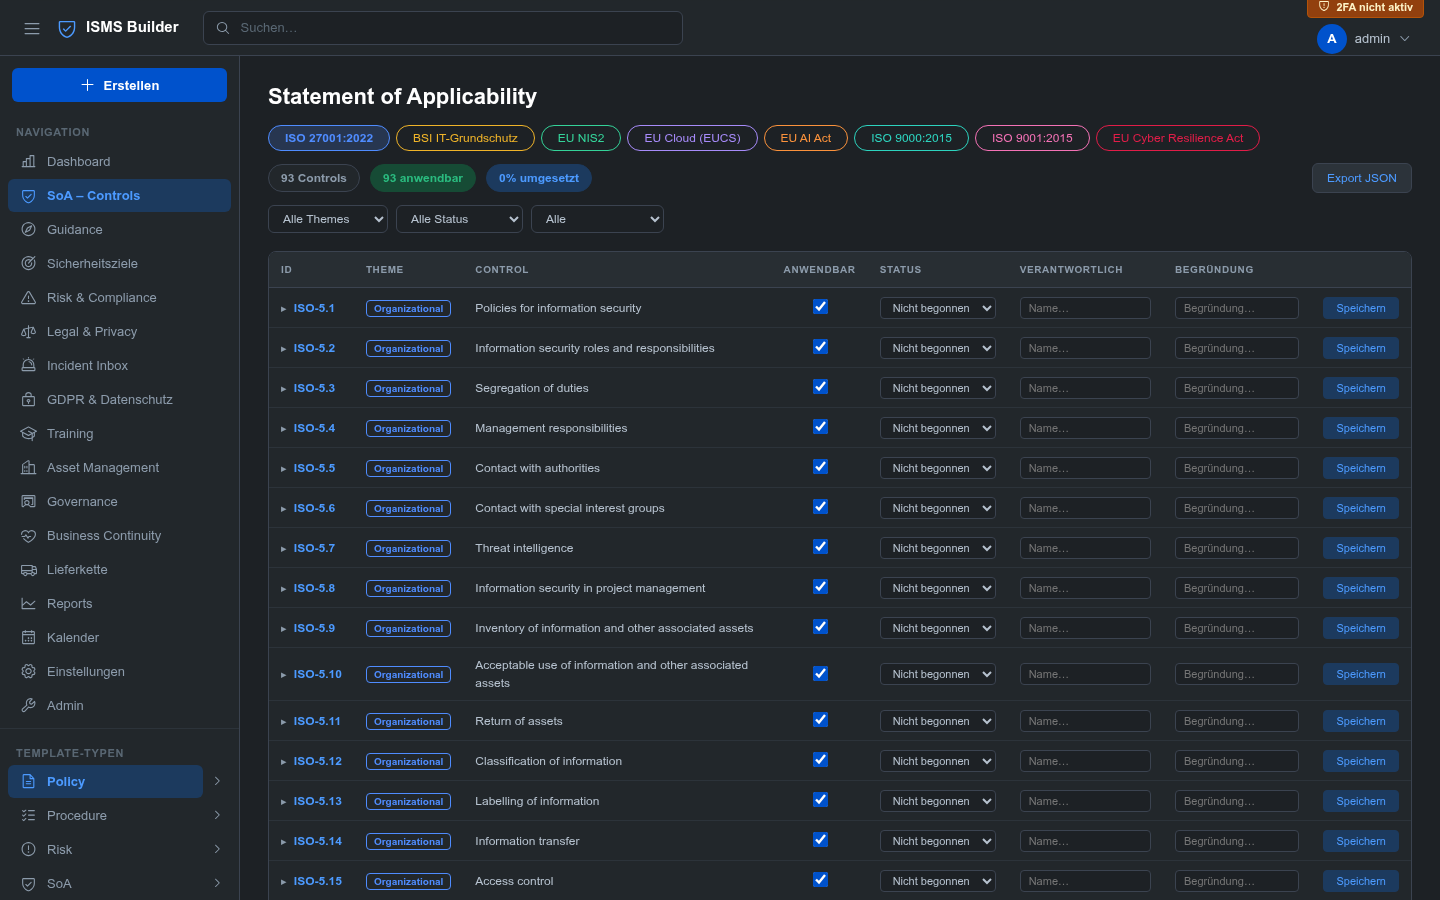
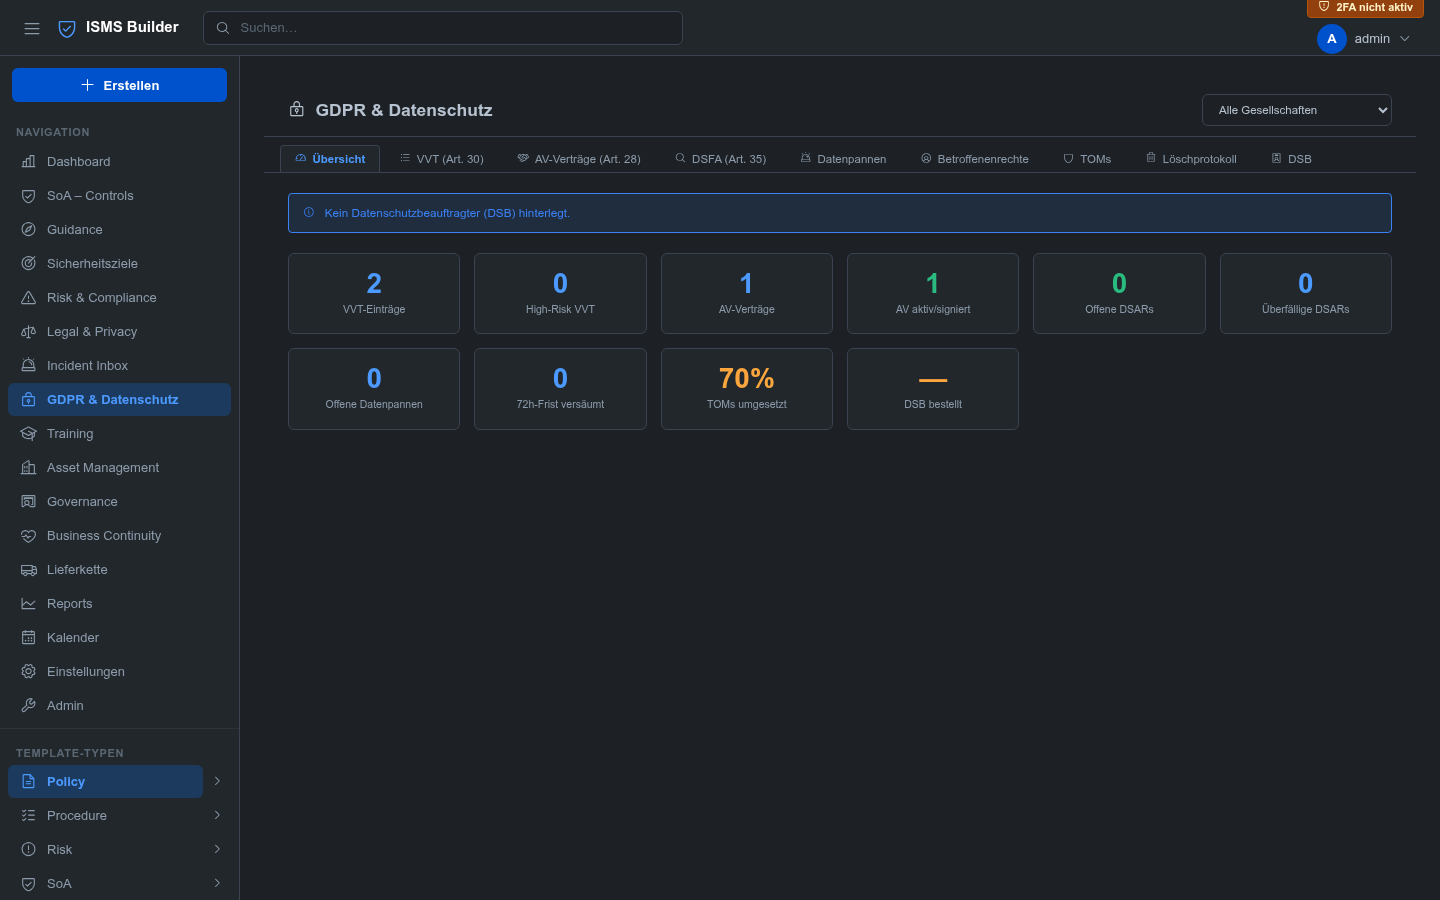
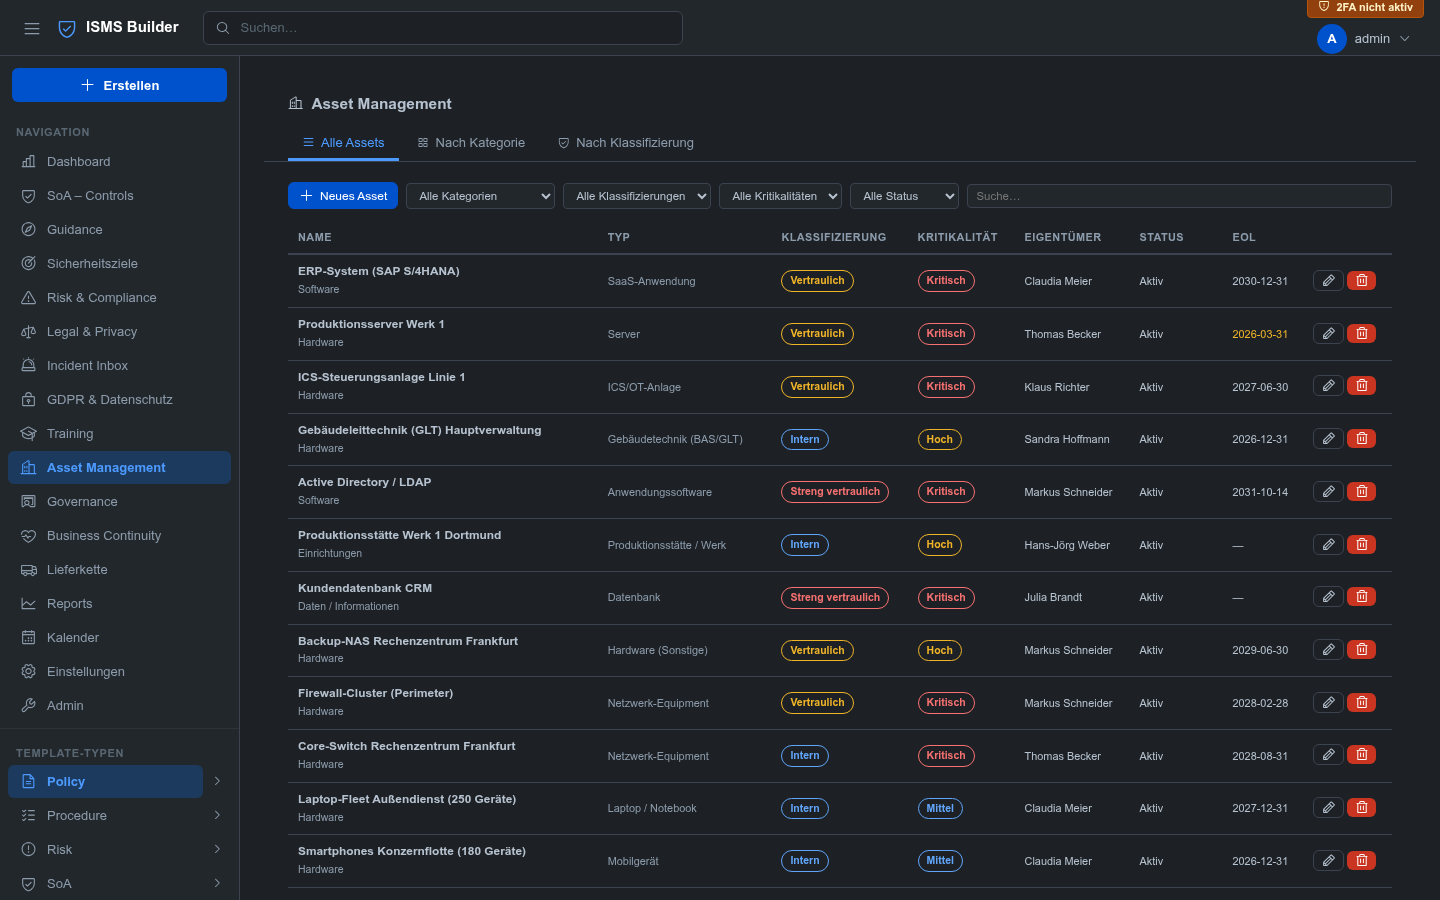
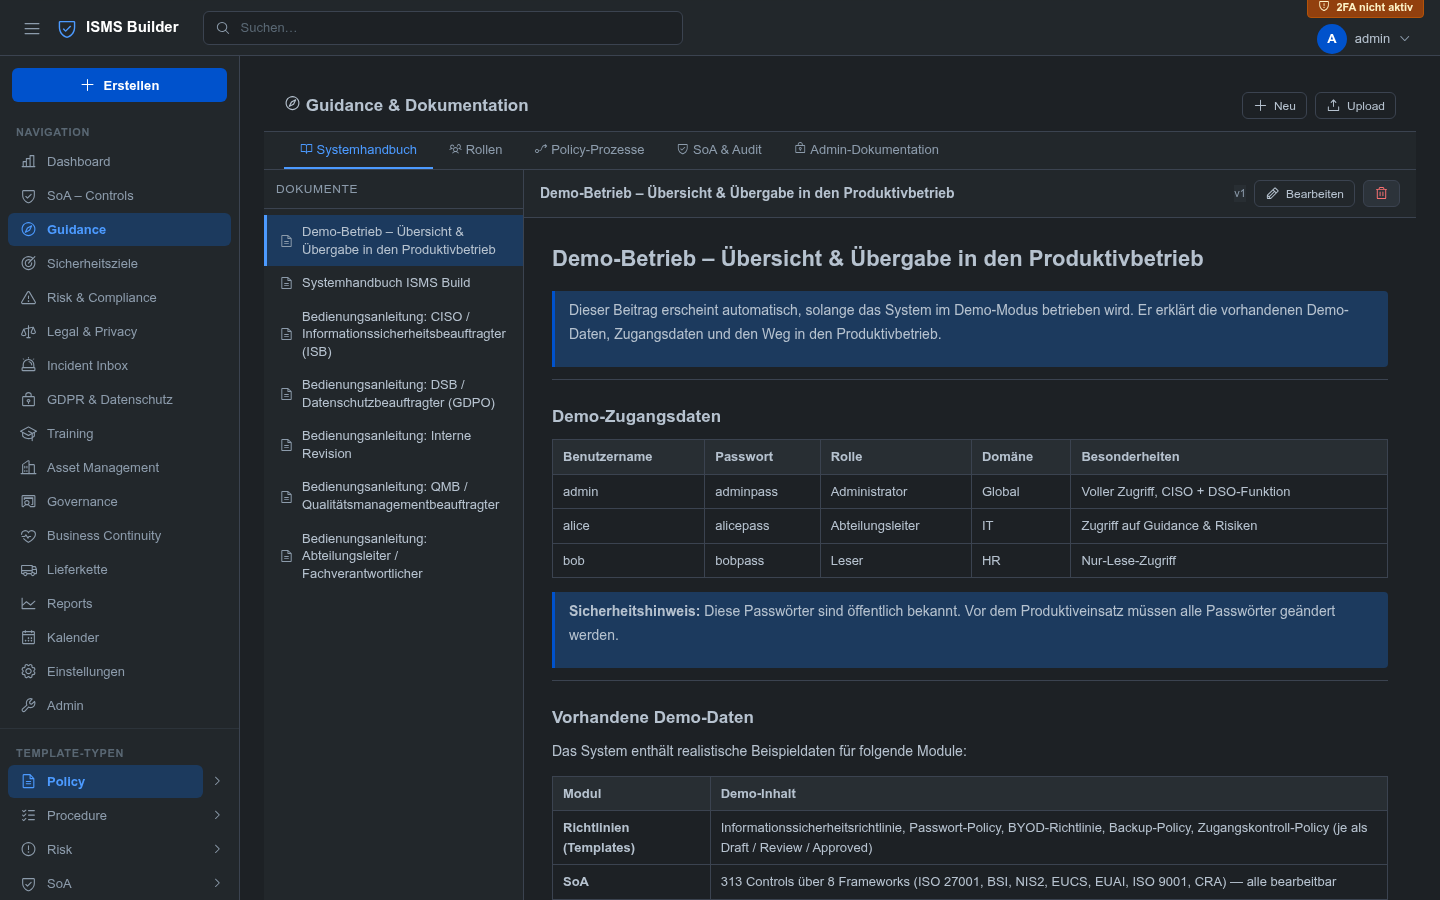
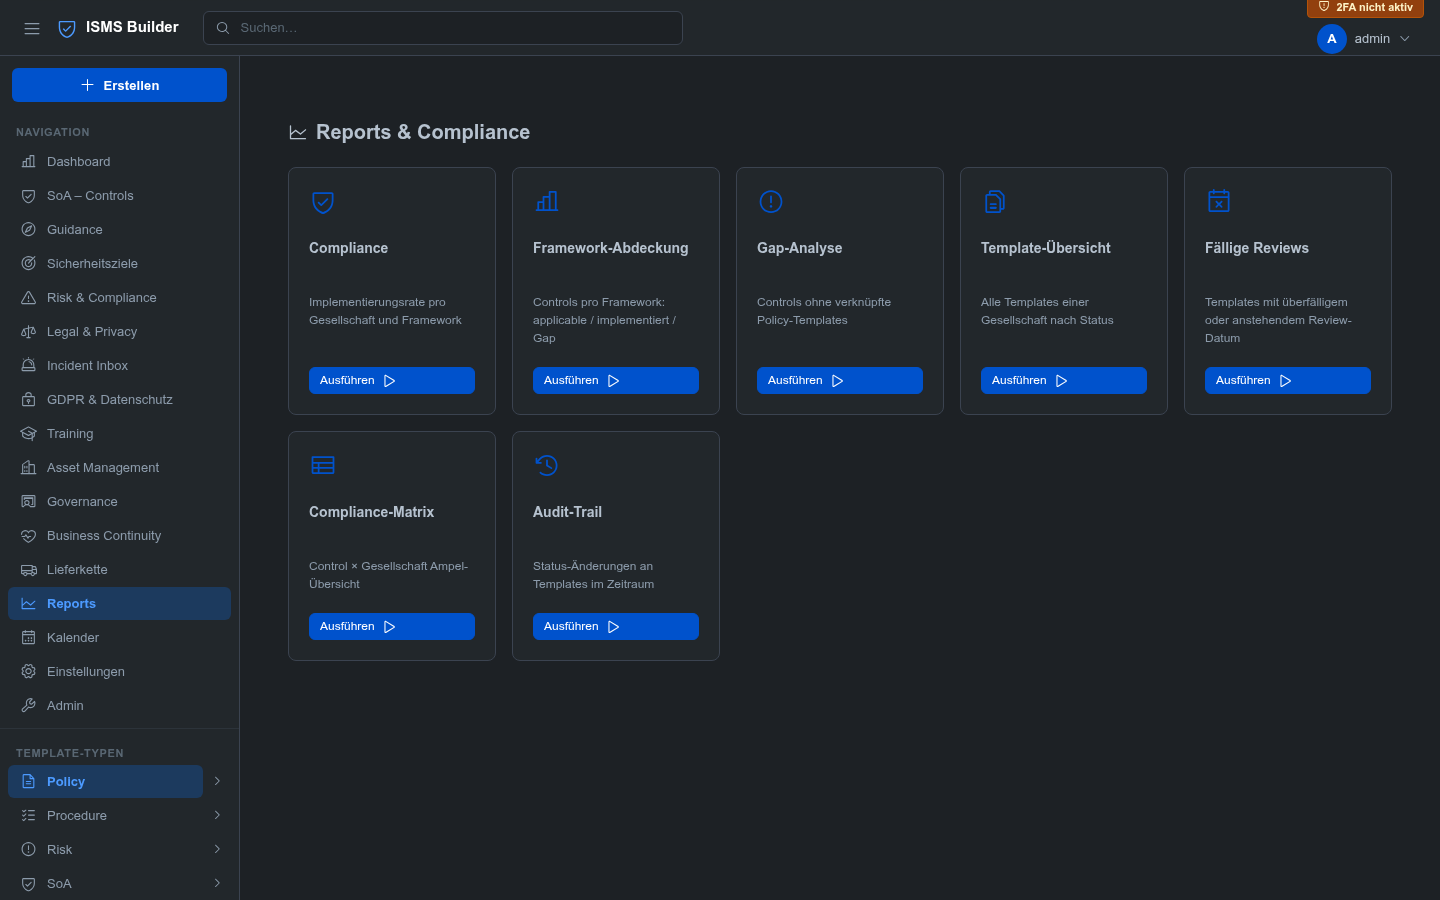
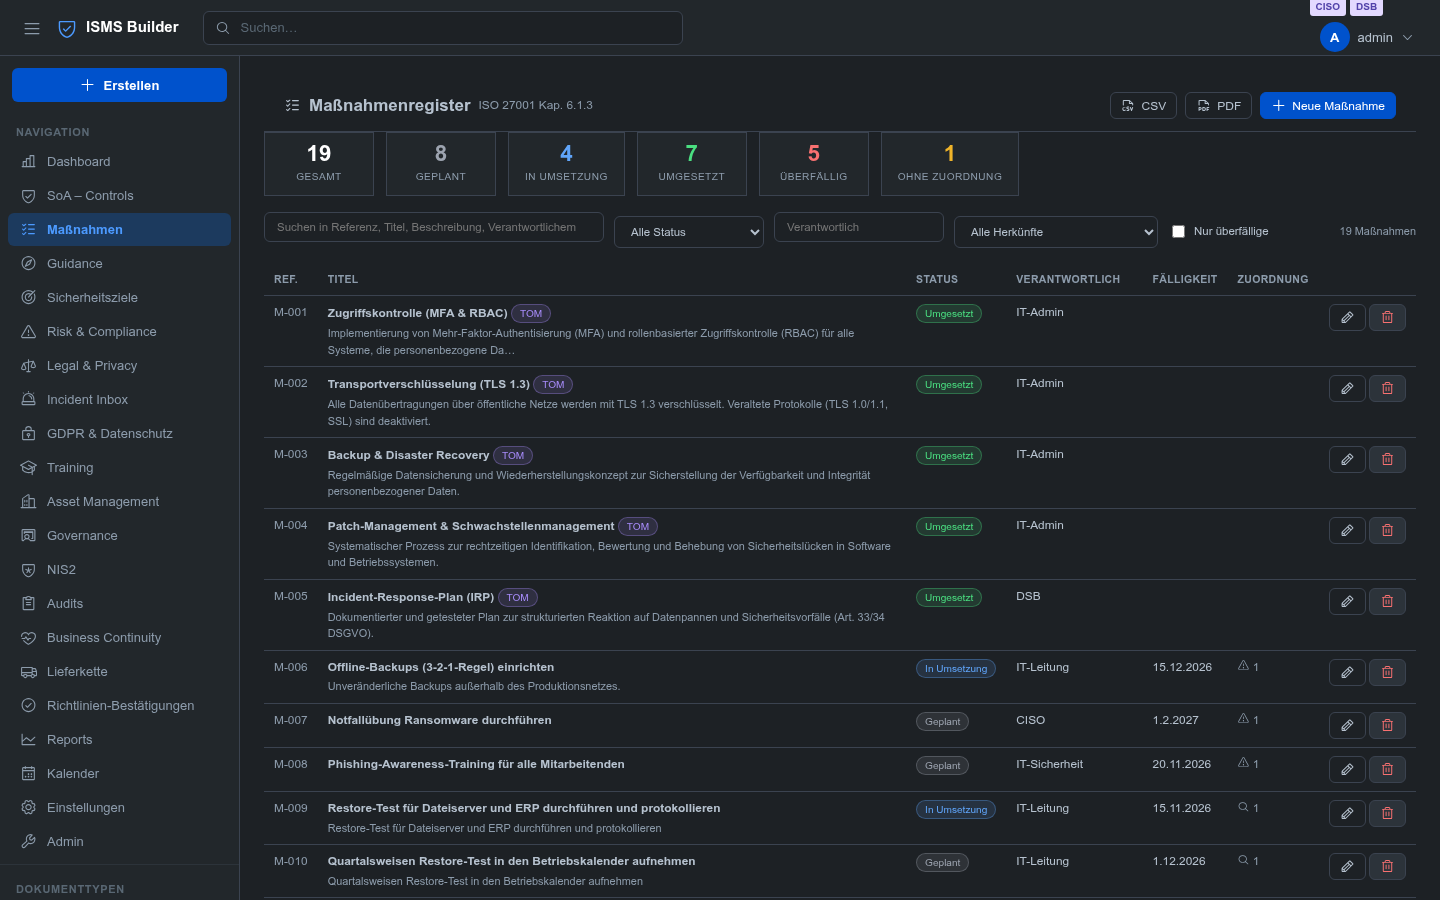
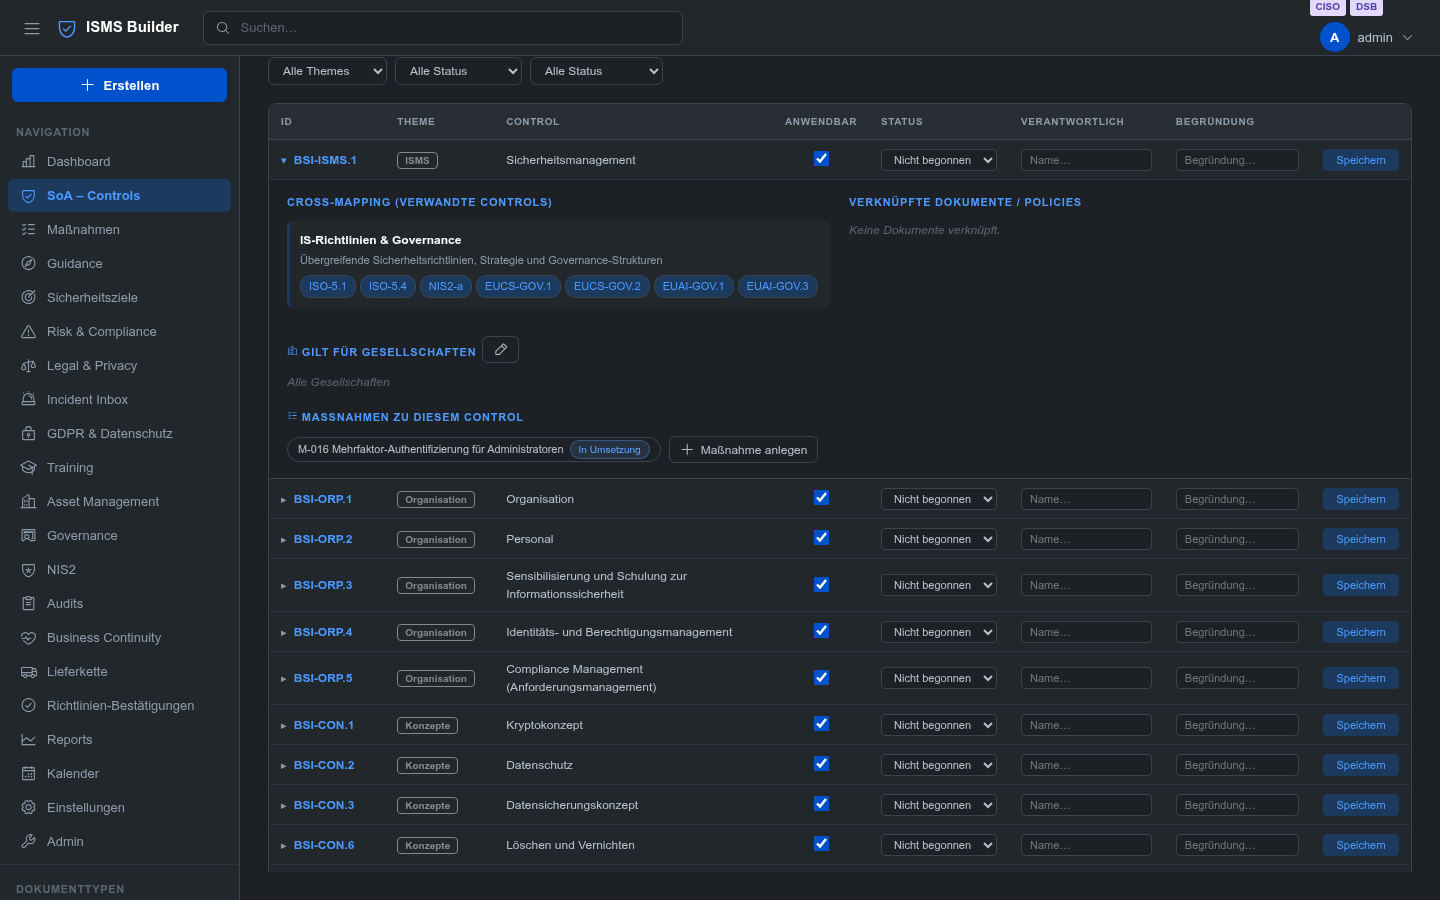
This web application helps organizations build and maintain an Information Security Management System entirely on their own hardware. It addresses major European compliance frameworks including ISO 27001, the NIS2 directive, GDPR, and BSI IT-Grundschutz. Core capabilities span policy authoring with version control, a statement of applicability covering hundreds of controls across multiple standards, risk registers with treatment tracking, GDPR-specific tooling for processing records and breach timers, asset and vendor inventories, business continuity planning, staff training logs, an incident reporting portal, audit planning with checklists, and automated policy acknowledgment workflows. A built-in calendar aggregates deadlines from every module. Optional local AI search runs via Ollama without sending data externally. The interface supports five languages and a multi-entity organizational hierarchy. Deployment is straightforward with Docker Compose using a JSON file backend by default, while SQLite, MariaDB, and PostgreSQL are available as alternatives. A companion Android application enables offline work with synchronization, though it has not yet been publicly released. Development is led by a single practitioner with decades of CISO experience; the codebase is actively evolving and not yet considered feature-complete.
isms-builder alternatives
 compOpen-source, self-hosted compliance platform that automates evidence, policies and controls for SOC 2, ISO 27001, HIPAA or GDPR, pitched as a Vanta alternative.Comparecomp with isms-builder
 OpenGRCOpenGRC is a self-hosted GRC platform for small/mid security teams covering risk, controls, audits, vendor risk, incidents, and policies with 152 importable frameworks.CompareOpenGRC with isms-builder
 emisaremisar gives AI agents declared infrastructure actions instead of shell. Policy gates actions, approvals for risky changes, tamper-evident audit trail.Compareemisar with isms-builder
 AiSOCSelf-hosted, open-source AI SOC with 2,535 detection rules and agents that record every step in an auditable ledger. MIT licensed, no API keys needed.CompareAiSOC with isms-builder
 proboProbo is a self-hosted GRC platform for engineering teams to manage SOC 2, GDPR, ISO 27001, and HIPAA compliance with a web console, CLI, GraphQL API, and MCP tools.Compareprobo with isms-builder
 StackResumeSelf-hosted AI resume builder with multi-agent pipeline, JD tailoring, and export to PDF, Word, and OpenDocument.CompareStackResume with isms-builder
 REI3REI3 is a self-hosted, open-source low-code platform for building multi-user business apps with full data ownership, replacing spreadsheets and SaaS tools.CompareREI3 with isms-builder
 FleetOpen-source MDM and endpoint management for macOS, Windows, Linux and mobile: self-hosted software patching, vulnerability tracking and live device reports.CompareFleet with isms-builder
All self-hosted alternatives to Commercial ISMS platforms (SaaS) →
Should you self-host isms-builder?
isms-builder scores 45/100 on selfhost.directory (how scoring works) and ranks #6 of 8 in Compliance. It has 256 GitHub stars.
It shipped 15 stable releases in the past year. The latest, v1.81.2, came out on 23 October 2026. New versions land roughly every 1 days.
Setup is moderate: expect some configuration beyond a single command. An official Docker image is available. It is AGPL-3.0-licensed and written mostly in JavaScript.
Its closest alternative on selfhost.directory is probo (62/100, 1 487 stars). It scores higher overall, so compare the two before you pick. See isms-builder vs probo side by side.
Features
- Asset Management
- Audit Findings
- BCM / BCP
- GDPR & Privacy
- Governance
- Incident Inbox
- Legal & Contracts
- Measures Register
- Policy Management
- Reports
- Risk Management
- Security Goals
- Supplier Management
- Training Records
isms-builder README

Self-hosted Information Security Management System — open source, no cloud required


📖 Wiki — Docker-Image-Nutzung & Umgebungsvariablen, Architektur & Module, FAQ, Mitwirken (DE/EN)
FAQ
Who maintains the project, and how fast is the response time?
One person, alongside a full-time job. Issues and discussions are usually answered within days; security reports are prioritised. For fixed timelines or guaranteed response times, a commercial vendor is recommended.
Where do I report bugs or security issues?
Regular bugs/feature requests as a GitHub Issue. Security issues should be reported privately via GitHub's private vulnerability reporting, not publicly.
How do I move from demo data to real production use?
You don't: demo and production are never mixed. Production is always a fresh installation — set up a new instance with STORAGE_BACKEND=json, create your own administrator and set your own secrets.
Why aren't the ISO 27001 controls included?
Because ISO 27001, ISO 9000, and ISO 9001 are copyright-protected standards that cannot be redistributed without a licence. BSI IT-Grundschutz, NIS2, EUCS, EU AI Act, and CRA are fully pre-installed instead, since they're based on publicly available legislation.
What's the fastest way to get started?
Easiest via the published Docker image. For a local Node.js install without Docker: clone the repo, run npm install, copy .env.example to .env, set JWT_SECRET, then npm start.
Does ISMS Builder replace certification or legal advice?
No. The tool helps organise and evidence the work towards ISO 27001, NIS2, GDPR/DSGVO, and BSI IT-Grundschutz — the actual assessment remains yours and your auditor's.
Is ISMS Builder a hosted service?
No. ISMS Builder is self-hosted only — no cloud, no SaaS fees, no managed service. Deployment, TLS, hardening, backups, updates, and access control are the user's responsibility.
More in Compliance
 marbleMarble is a self-hosted, open-source fraud and AML platform: no-code transaction monitoring, sanctions and PEP screening, case management and AI-assisted investigations.
 nexus-gatewaySelf-hosted open-source AI gateway intercepting LLM traffic at SDK, network, and OS layers with compliance, routing across 20+ providers, caching, quotas, and audit.
 Open ArchiverAn open-source platform for legally compliant email archiving.
 OpenELIS GlobalSelf-hosted, open-source LIS/LIMS used in 26+ countries. FHIR R4 native with analyzer integration, pathology, sample storage, and One Health surveillance.
- OpenGRCOpenGRC is a self-hosted GRC platform for small/mid security teams covering risk, controls, audits, vendor risk, incidents, and policies with 152 importable frameworks.
 OpenSignA self-hosted, open-source DocuSign alternative for e-signing PDFs: templates, sequential multi-signer flows, audit trails and a document vault.
 PatchMonSelf-hosted open-source platform for patching Linux, FreeBSD, and Windows fleets with outbound-only agents, dry-run validation, and browser SSH/RDP.
 PIAPIA is a free, open-source tool from the French CNIL for GDPR Data Protection Impact Assessments. Available as a portable desktop app or self-hosted web application.
- proboProbo is a self-hosted GRC platform for engineering teams to manage SOC 2, GDPR, ISO 27001, and HIPAA compliance with a web console, CLI, GraphQL API, and MCP tools.
 rudderRudder is a self-hosted, open-core infrastructure security automation platform for configuration, patching, and compliance across Linux and Windows.
 TeampassSelf-hosted, open-source team password vault on PHP/MySQL: folder and role access control, AES-256-GCM encryption, LDAP/OAuth2 SSO, TOTP and compliance reports.
 ThreatMapperSelf-hosted, open-source CNAPP: Deepfence ThreatMapper scans cloud, Kubernetes and container workloads for vulnerabilities, exposed secrets and CIS compliance gaps.
0 comments