Self-host OpenELIS Global
3.3.0Open-source lab information system for clinical labs
- Stars
- 278
- Ports
- 8080 (Backend webapp HTTP), 8443 (Backend webapp HTTPS)
What is OpenELIS Global?
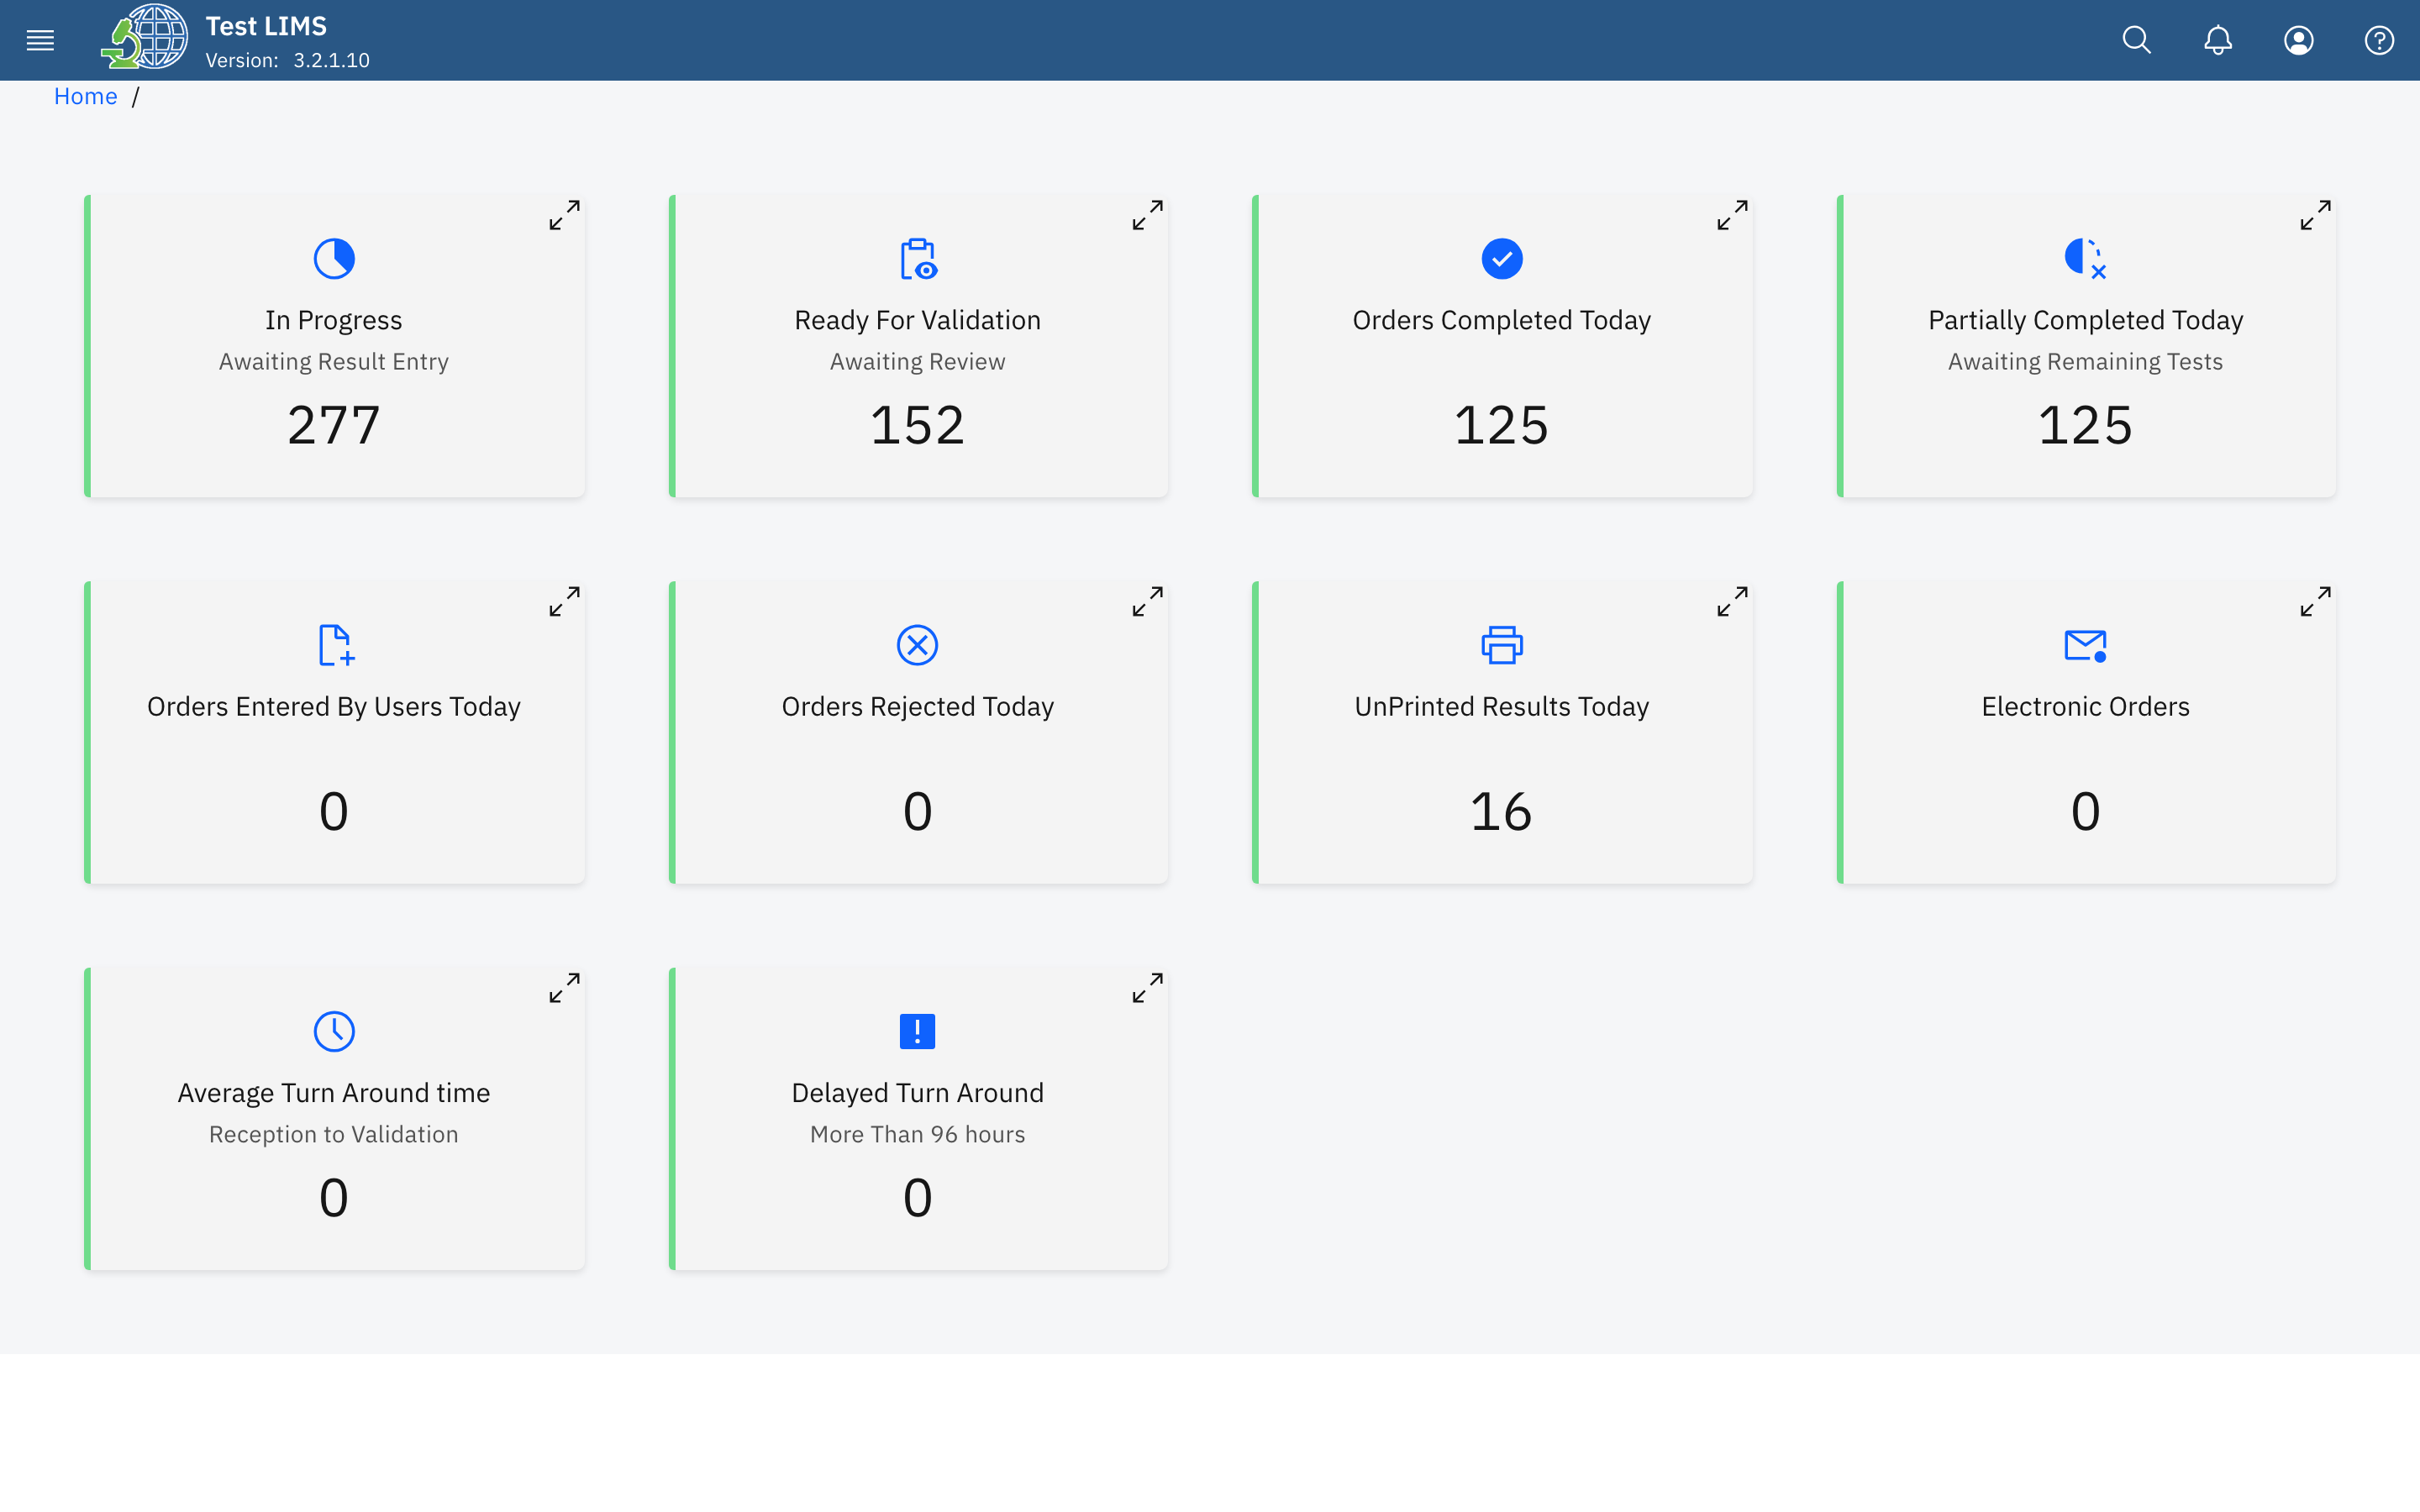
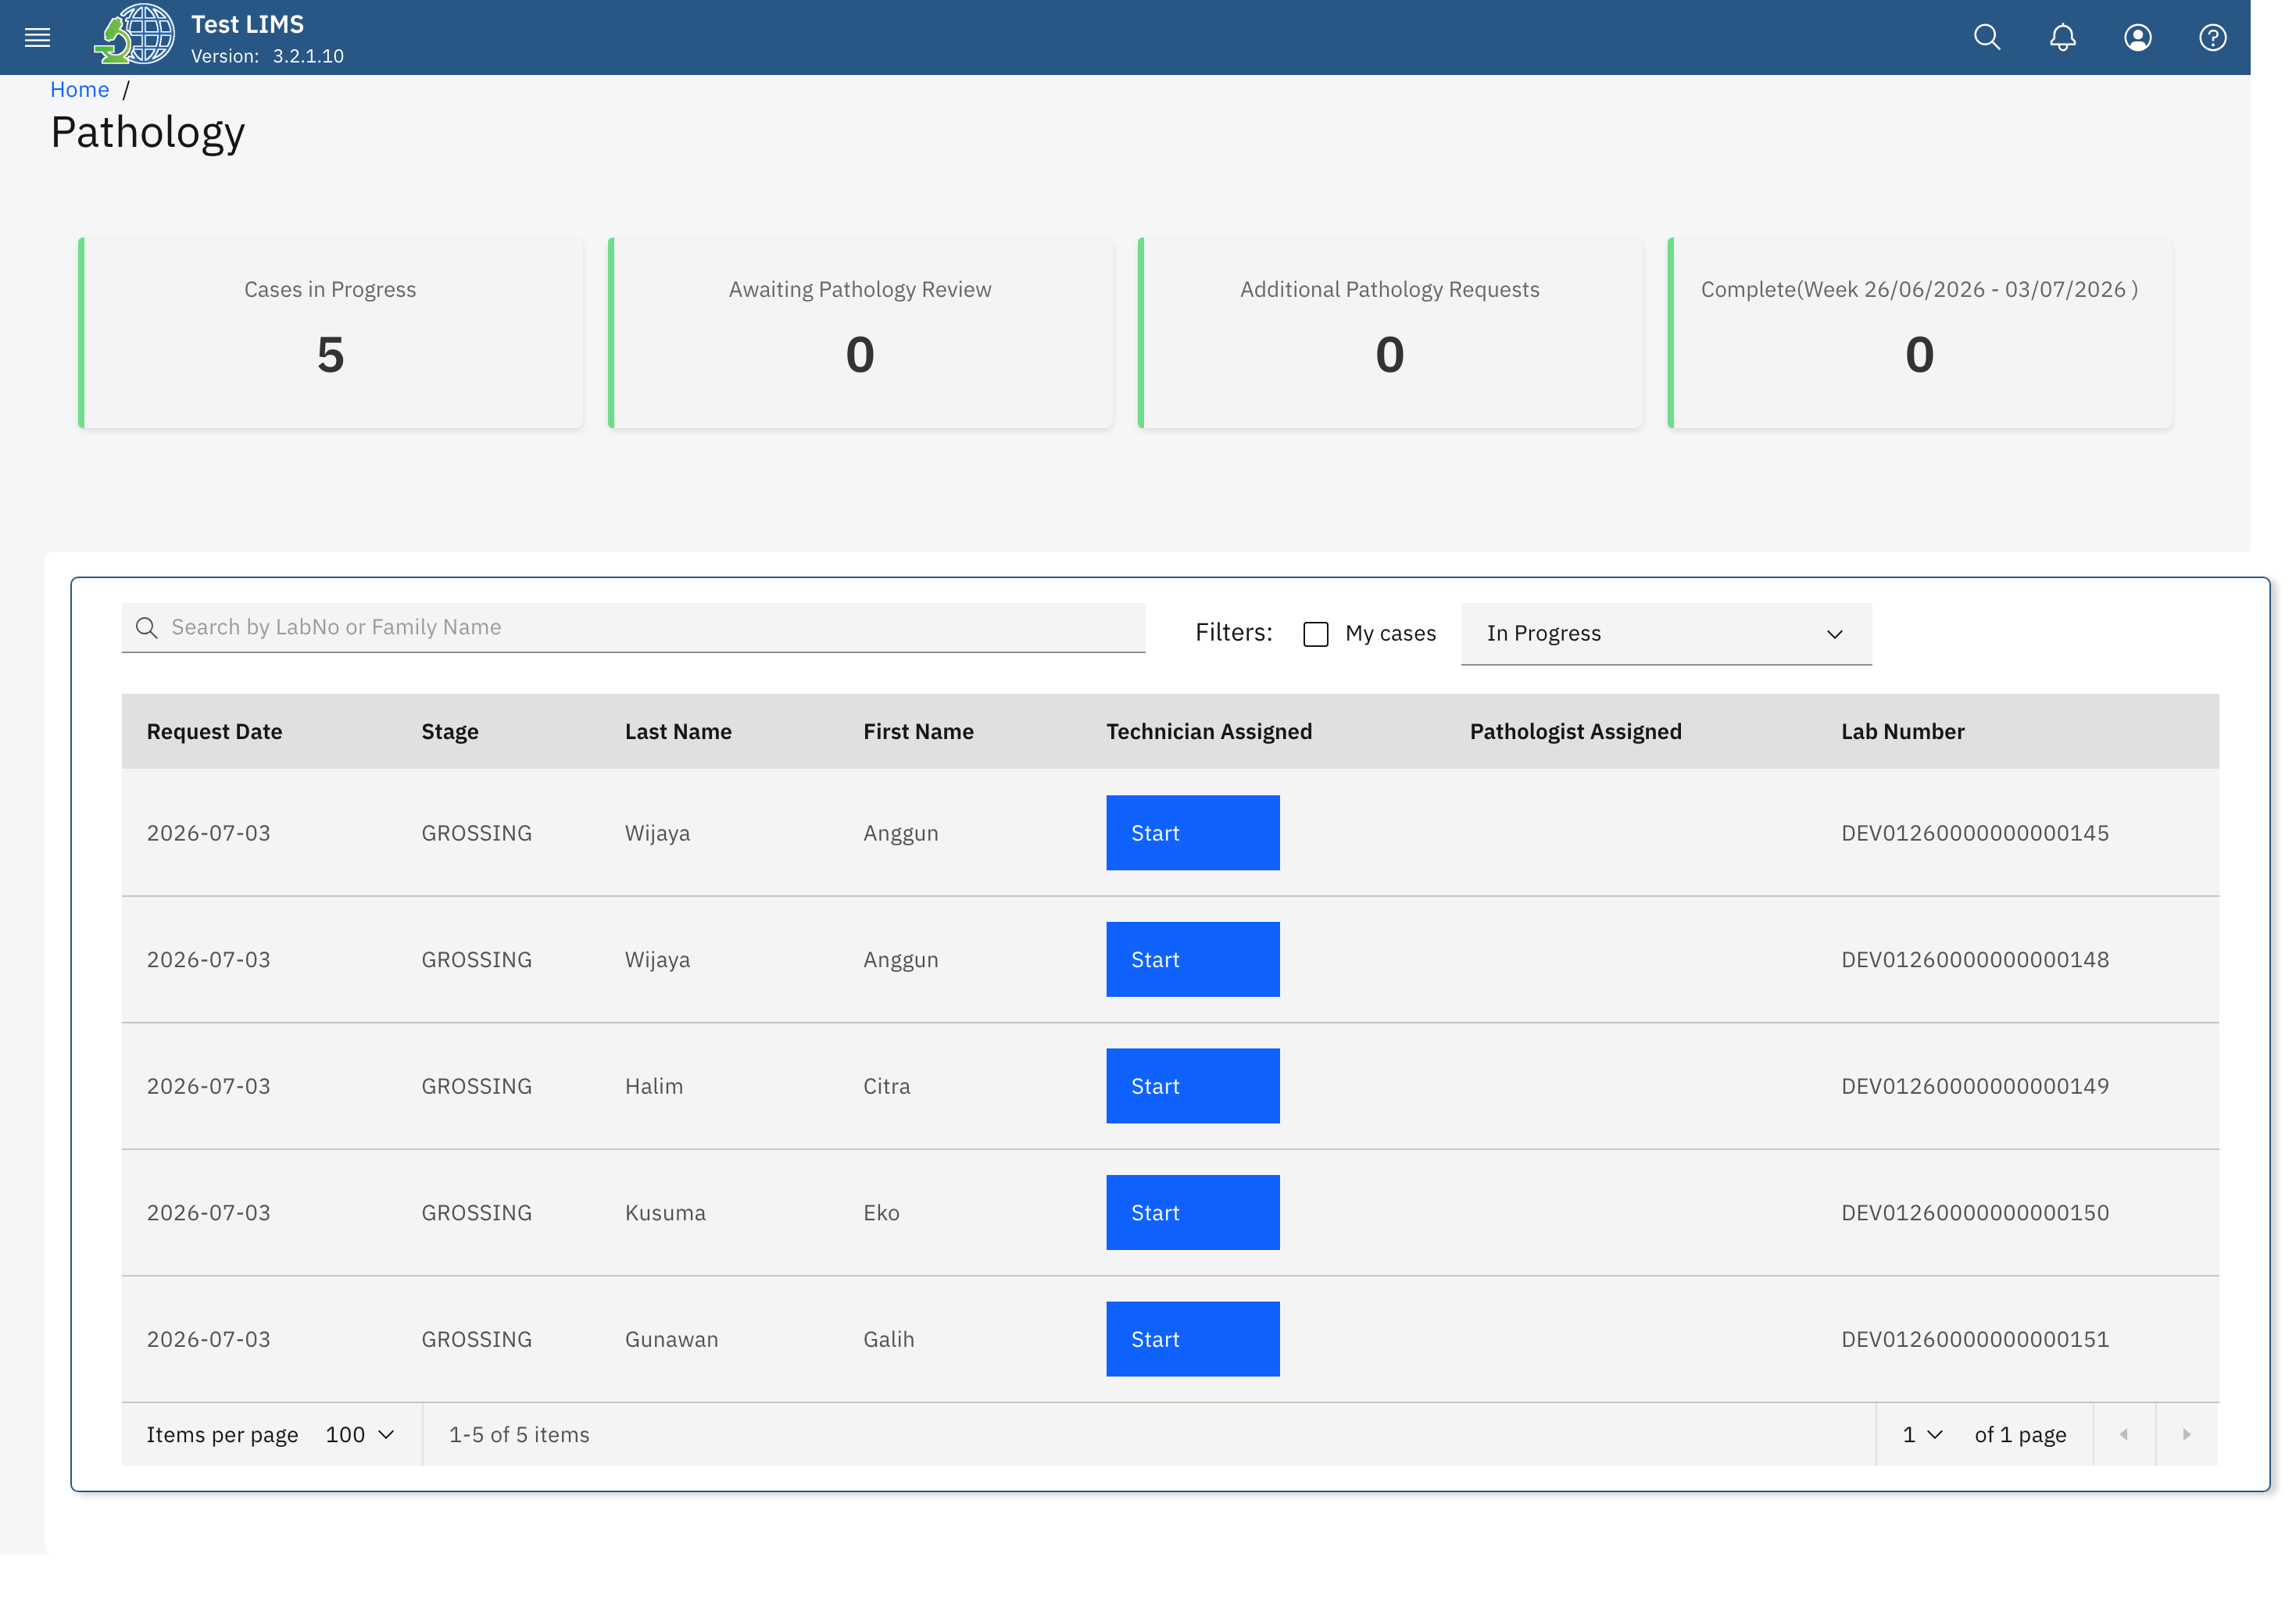
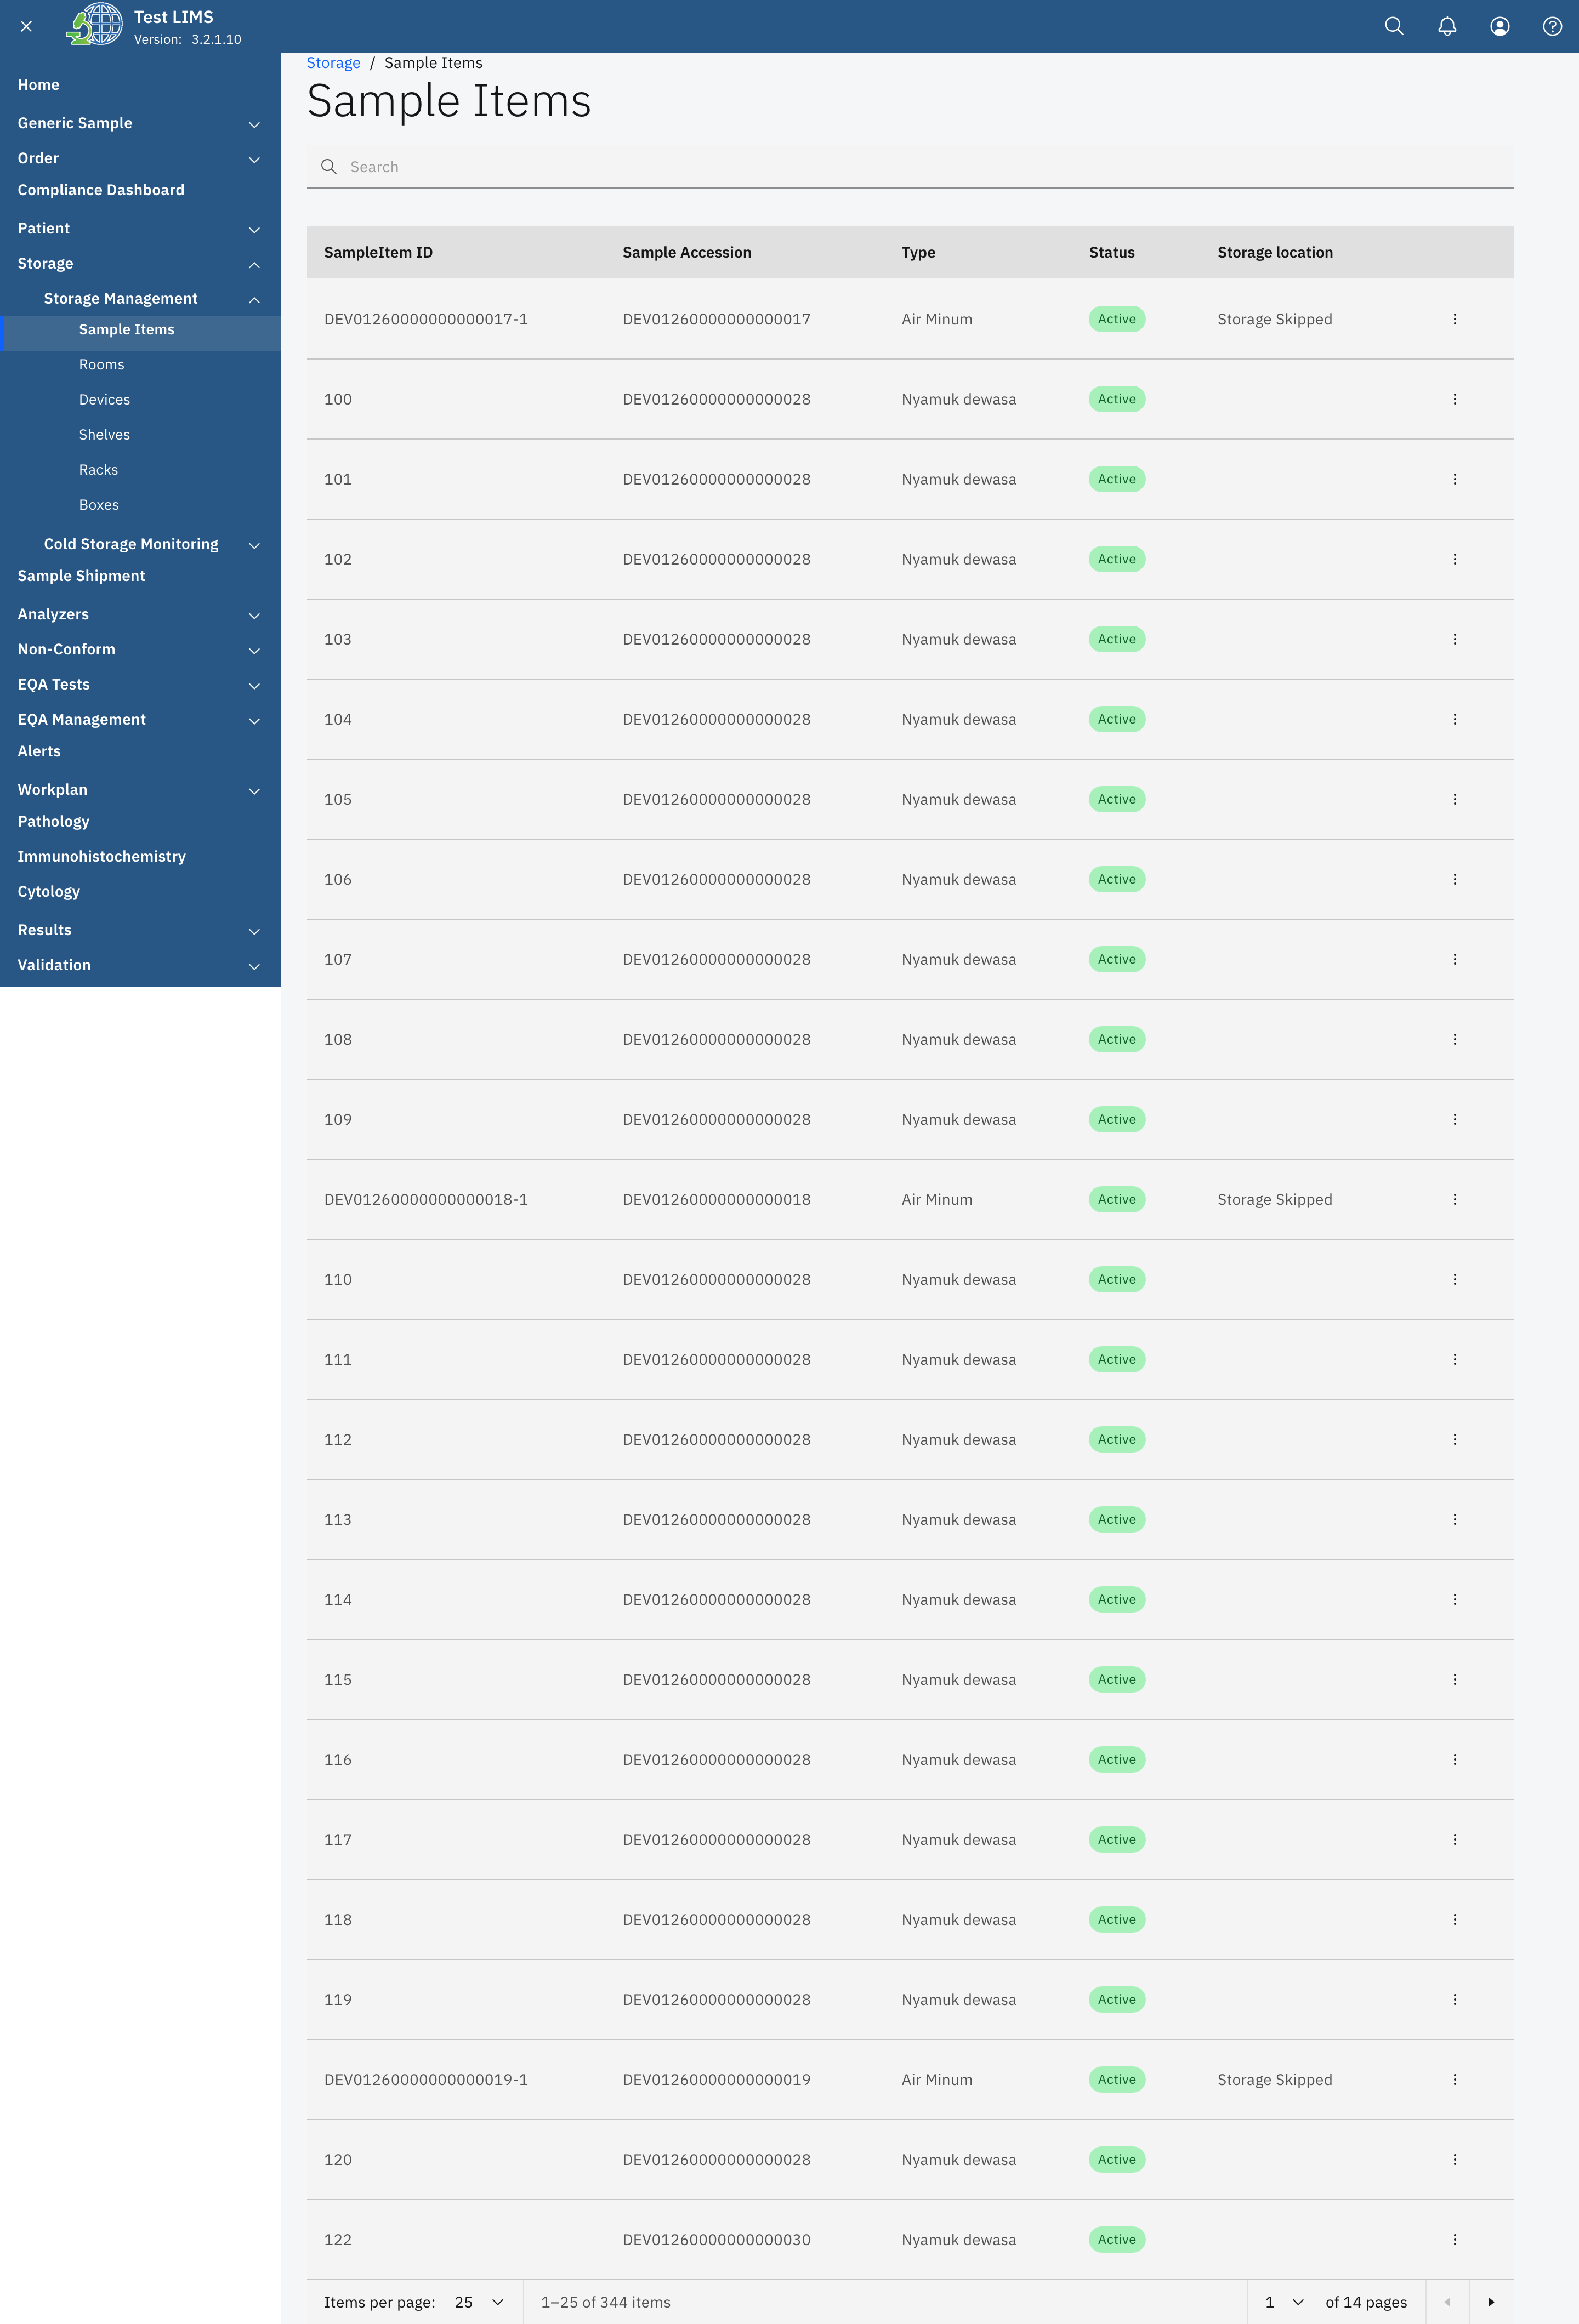
OpenELIS Global is an enterprise-grade Laboratory Information System built for public health laboratories operating at national scale. The software automates laboratory work plans, imports results from clinical analyzers, and handles complex workflows including pathology, cytology, and environmental testing with compliance evaluation. It uses FHIR R4 as its native standard for interoperability with other health systems, satisfies ISO and SLIPTA accreditation criteria, and connects to laboratory instruments through ASTM, HL7, and CSV protocols. The platform tracks specimens through sample storage and chain-of-custody features, manages pathology cases from grossing to sign-out, and provides One Health surveillance across human, animal, and environmental health domains in a single system. Deployment is via Docker Compose using published container images, with an offline installer available for air-gapped environments. A public demo instance runs at demo.openelis-global.org. The project is maintained by the Digital Initiative Group at the University of Washington and released under the Mozilla Public License 2.0.
Should you self-host OpenELIS Global?
OpenELIS Global scores 54/100 on selfhost.directory (how scoring works) and ranks #3 of 5 in Healthcare. It has 278 GitHub stars.
It shipped 8 stable releases in the past year. The latest, 3.3.0, came out on 20 October 2026. New versions land roughly every 4 weeks.
Setup is moderate: expect some configuration beyond a single command. It is MPL-2.0-licensed and written mostly in Java.
Its closest alternative on selfhost.directory is OpenEMR (72/100, 5 555 stars). It scores higher overall, so compare the two before you pick. See OpenELIS Global vs OpenEMR side by side.
Features
- Analyzer integration
- Electronic signatures
- Environmental testing with compliance evaluation
- FHIR R4 native
- ISO/SLIPTA accreditation support
- Laboratory Information System (LIS/LIMS)
- Live demo
- Multi-language Support
- One Health surveillance
- Pathology & Histopathology
- REST API
- Sample storage & chain of custody
- Single Sign-On (SSO)
- Work plan automation
OpenELIS Global README
More in Healthcare
 OpenEMRSelf-hosted, open-source EHR and clinic management suite with scheduling, e-billing, prescriptions, FHIR APIs and a patient portal; runs on Docker or a LAMP stack.
 OpenScribeOpenScribe is a self-hosted, open-source AI medical scribe that records encounters, transcribes audio locally with Whisper, and generates clinical notes using LLMs.
 MirobodyOpen-source, self-hosted AI health data engine: standardizes lab reports, wearables and genetics, answers with source citations, and can run models locally via llama.cpp.
 oncodashSelf-hosted open-source decision support for tumor boards targeting ovarian cancer, with Vue.js frontend and Django backend using Neo4j.
 Open Data CaptureOpen Data Capture is a self-hosted, open-source web platform for clinical questionnaires and interactive tasks, with hash-based patient IDs and multilingual support.
0 comments