selfhost.directory

The index of self-hostable projects — ranked, categorized and served with live updates.
Own your data and stop giving it to big tech.

portal-tunnel logo

Self-host portal-tunnel

v2.7.0

Self-hostable relay tunnel for localhost

ReleaseOpen SourceMIT
Updated9 hours ago
LanguageGo
Setup difficultyModerate
Stars
291
Ports
443 (HTTPS/SNI router ingress), 53 (Embedded authoritative DNS (TCP/UDP)), 40000 (Lease port range start (TCP/UDP for raw TCP and UDP transports)), 40009 (Lease port range end (TCP/UDP for raw TCP and UDP transports))
Docker
ghcr.io/gosuda/portal
Install with Docker
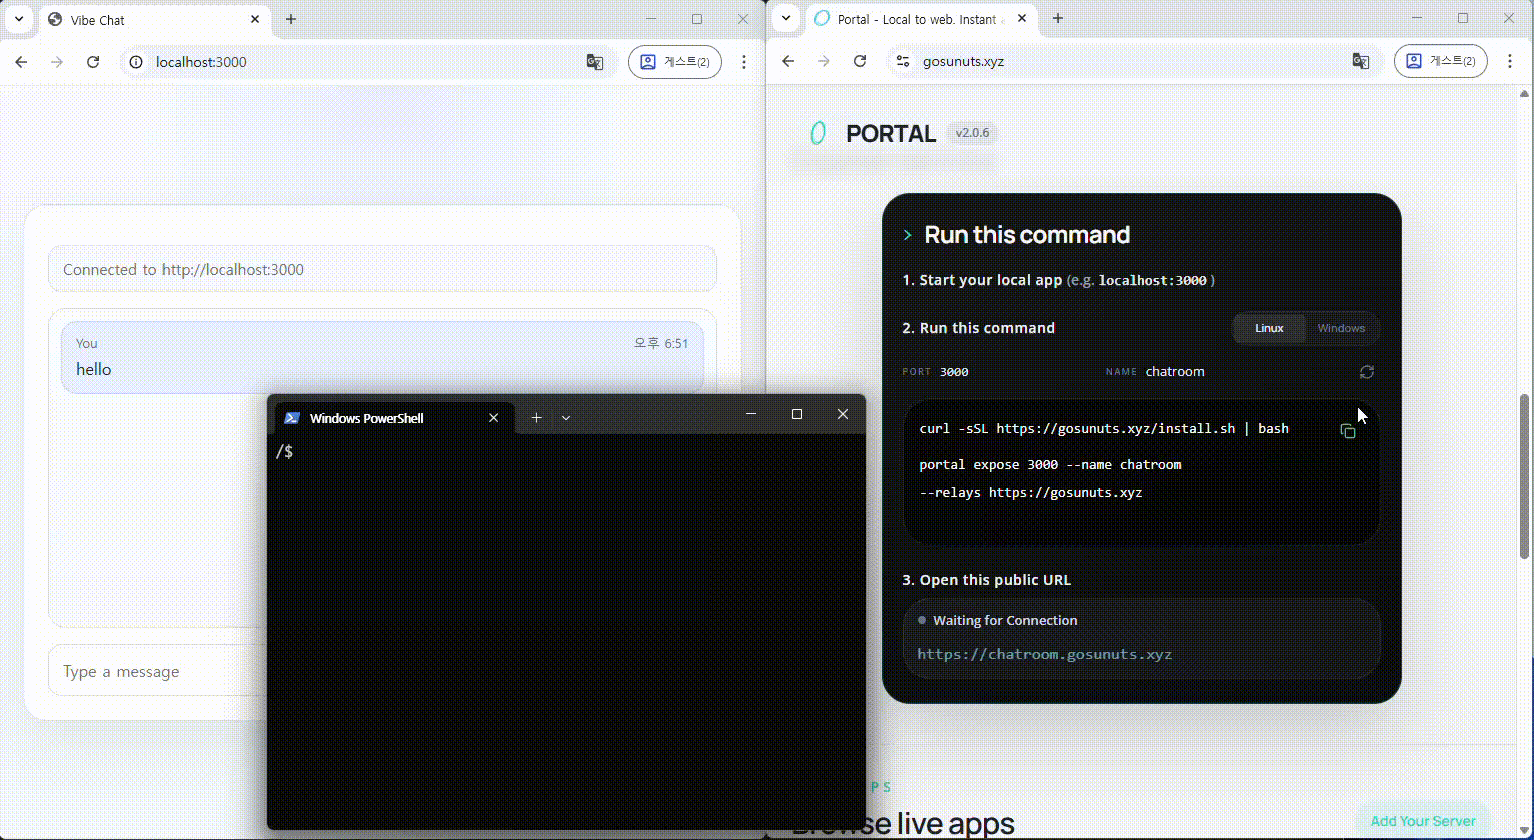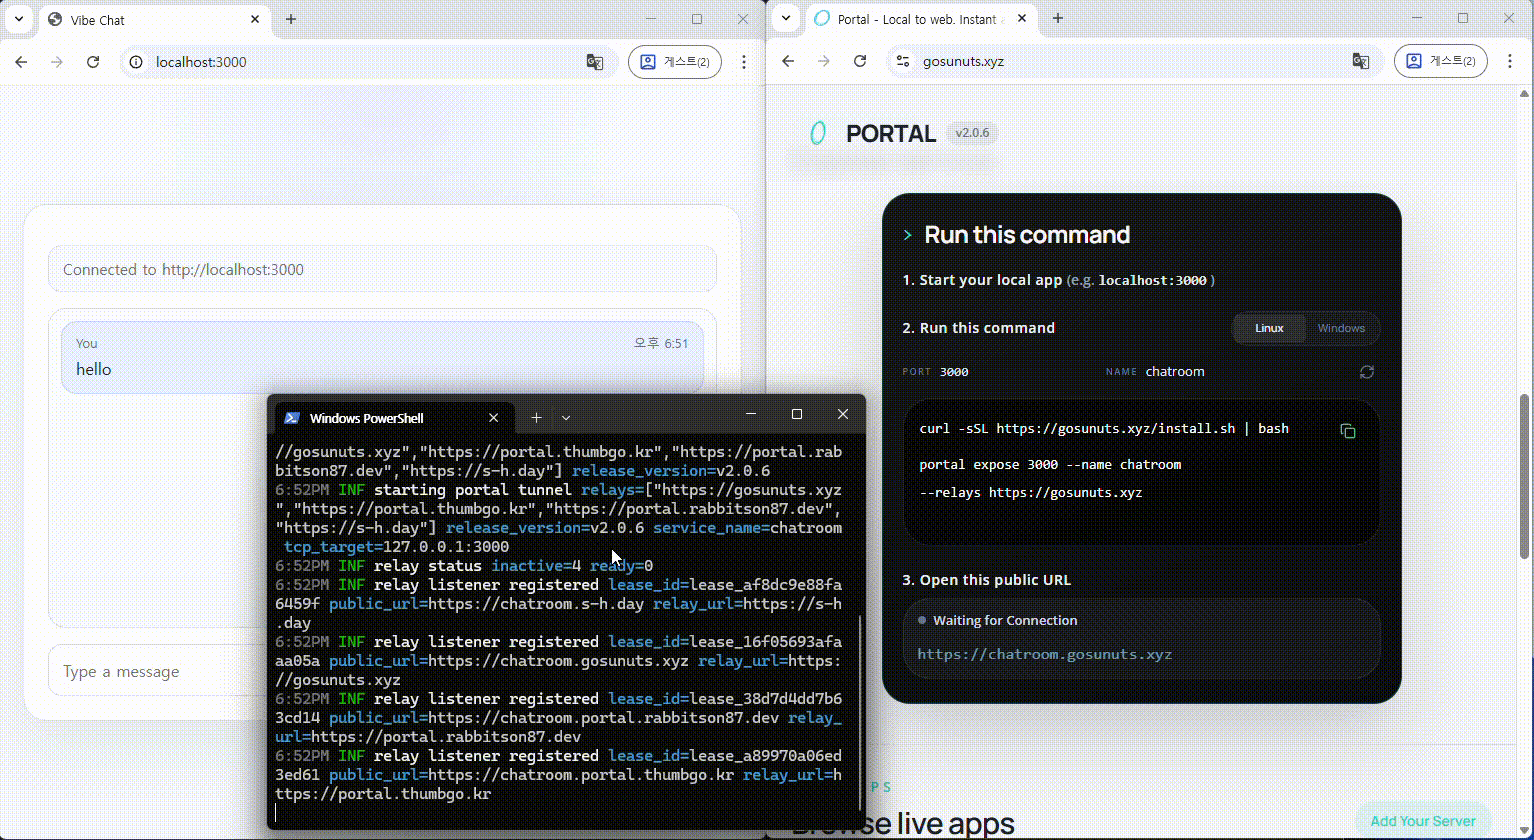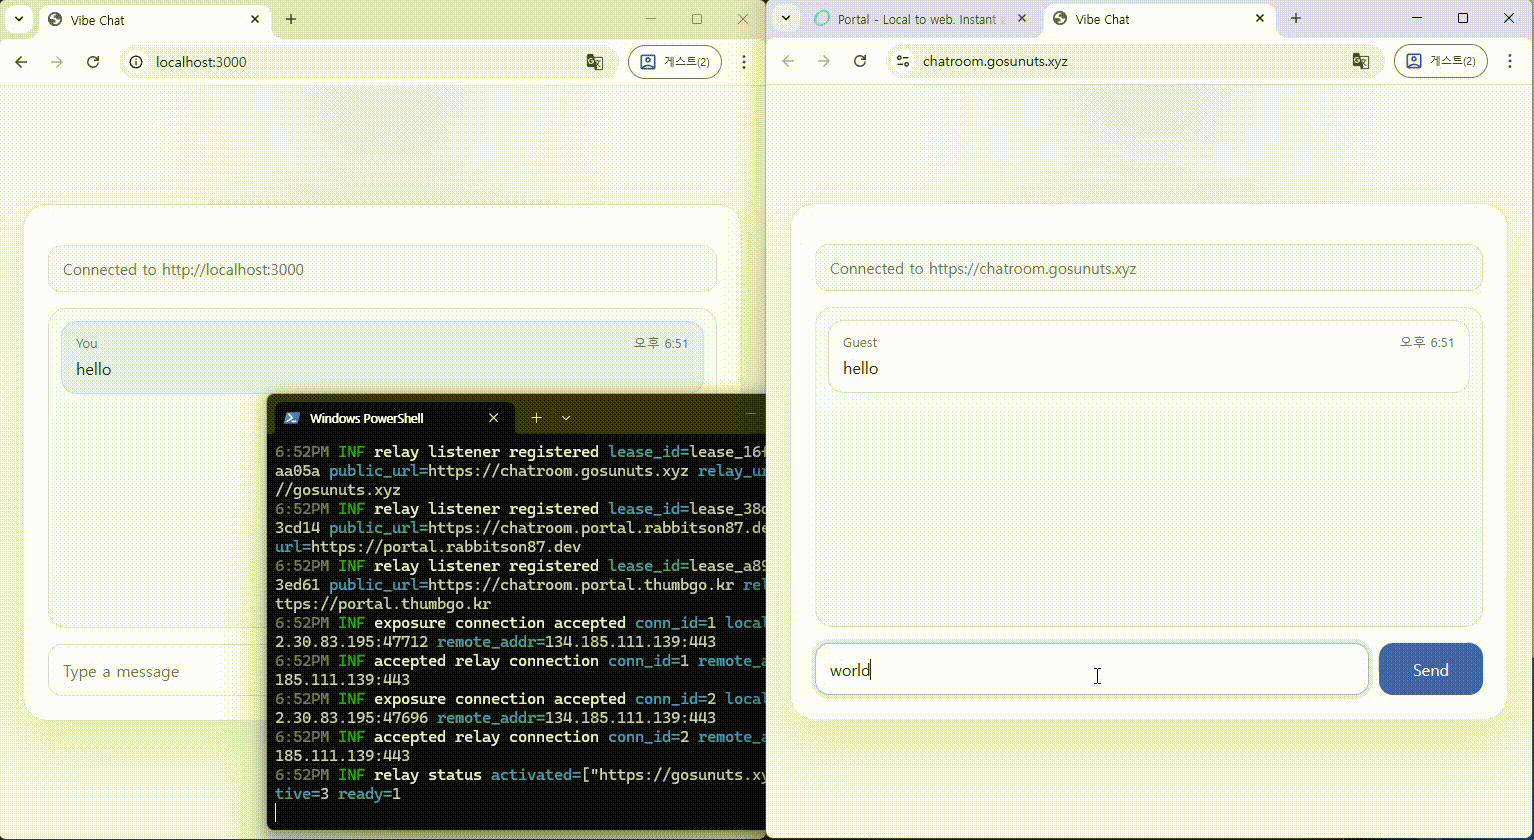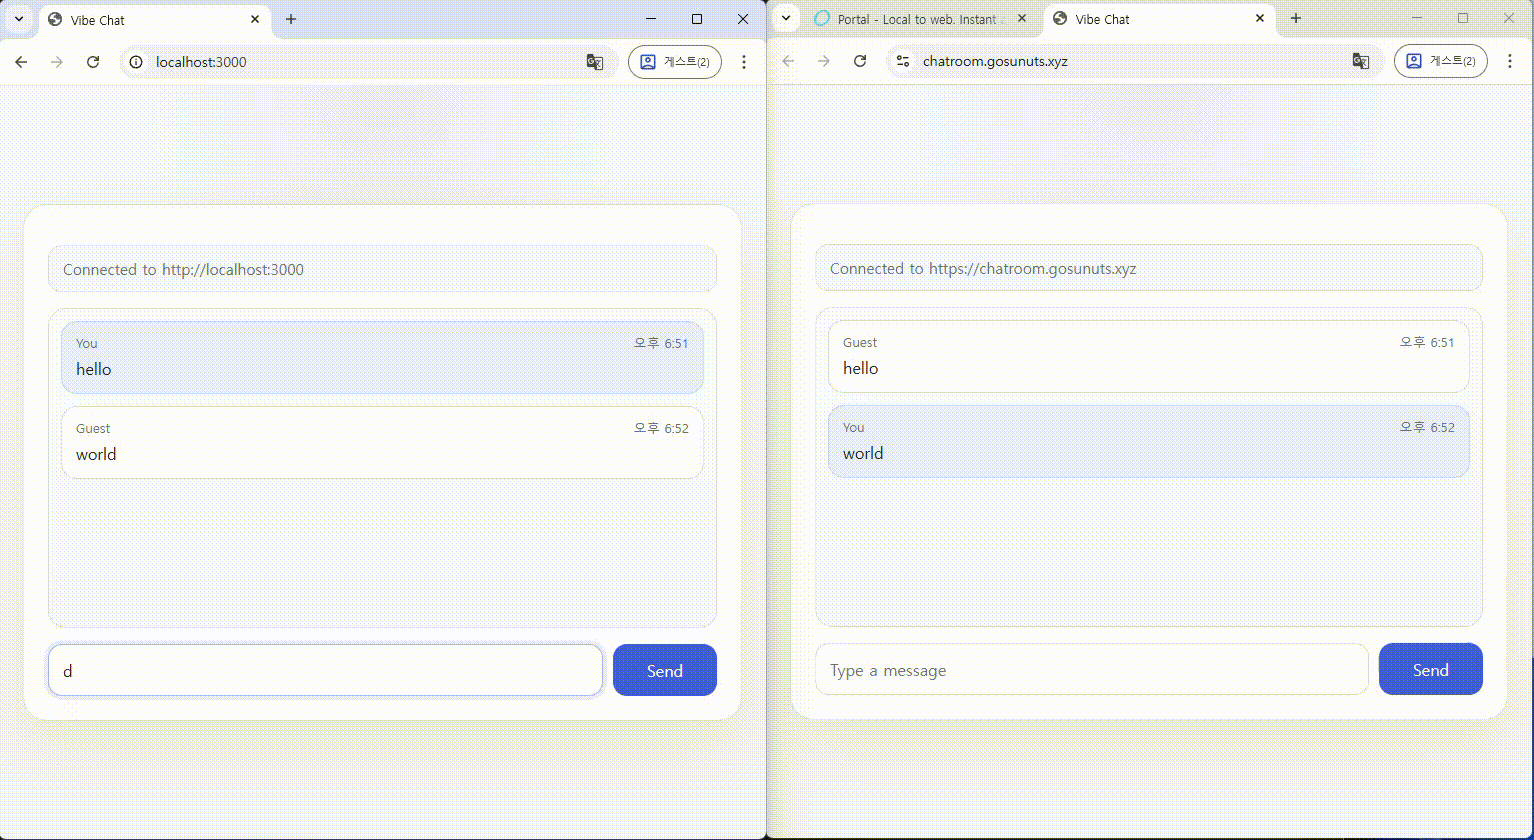
portal-tunnel screenshot 1

What is portal-tunnel?

Portal publishes local apps, APIs, and agents to the internet through self-hosted or public relays. It eliminates port forwarding, firewall rules, and manual DNS. TLS terminates locally for uncached HTTPS streams, while a built-in self-probe detects MITM termination. Multiple relays form failover pools, and an IVNP overlay adds routing privacy. Micropayments use gasless stablecoins on Sui, Casper, or Nano. Auth relies on local secp256k1 identities with SIWE signing — no accounts or API keys. The CLI handles one-off tunnels; Portal Agent runs persistent tunnels from a TOML config with a TUI dashboard. Relays run as a single Docker image with embedded DNS and automatic ACME certs. MIT-licensed, zero telemetry, no enterprise tiers.

Should you self-host portal-tunnel?

portal-tunnel scores 52/100 on selfhost.directory (how scoring works) and ranks #15 of 31 in Networking. It has 291 GitHub stars.

It shipped 20 stable releases in the past year. The latest, v2.7.0, came out on 27 October 2026. New versions land roughly every 5 days.

Setup is moderate: expect some configuration beyond a single command. An official Docker image is available. It is MIT-licensed and written mostly in Go.

Its closest alternative on selfhost.directory is Webhook.site (66/100, 6 786 stars). It scores higher overall, so compare the two before you pick. See portal-tunnel vs Webhook.site side by side.

Features

  • End-to-end tenant TLS
  • IVNP-backed overlay networking
  • MITM self-probe
  • Multi-relay failover
  • Native x402 micropayments
  • No accounts or API keys
  • Opt-in relay static cacheOnly for identity-bound canonical hostnames; friendly aliases always use live origin
  • Portal Agent
  • Public relay registry
  • Raw TCP tunneling
  • Routed HTTP mode
  • Self-hosted relay
  • SIWE application authentication
  • Static site serving
  • UDP Relay

portal-tunnel README

How to install portal-tunnel

Install portal-tunnel with Docker

Environment variables
PORTAL_URL, IDENTITY_PATH, ADMIN_TOKEN

mkdir -p ./relay-data sudo chown 65532:65532 ./relay-data ADMIN_TOKEN=$(openssl rand -hex 32) docker run -d --name portal-relay --restart unless-stopped --cap-add NET_BIND_SERVICE -p 443:443 -p 53:53/tcp -p 53:53/udp -e PORTAL_URL=https://relay.example.com -e IDENTITY_PATH=/portal-certs -e ADMIN_TOKEN="$ADMIN_TOKEN" -v $(pwd)/relay-data:/portal-certs ghcr.io/gosuda/portal:2

Quick start for relay; replace relay.example.com with your domain

How to configure portal-tunnel

  • ACME_CA_DIR_URLCustom ACME CA directory URL

    Custom ACME CA directory URL

    values: HTTPS URL

  • ACME_DNS_PROVIDERembeddedDNS provider for managed DNS-01 challenges

    DNS provider for managed DNS-01 challenges

    values: embedded, cloudflare, gcloud, hetzner, njalla, route53, vultr

  • ADMIN_TOKENBearer token for the admin and policy APIs

    Bearer token for the admin and policy APIs

    values: Any long random value (generate with openssl rand -hex 32)

  • AWS_ACCESS_KEY_IDAWS access key ID for Route53

    AWS access key ID for Route53

    values: Access key

  • AWS_DNSSEC_KMS_KEY_ARNAWS KMS key ARN for Route53 DNSSEC

    AWS KMS key ARN for Route53 DNSSEC

    values: KMS key ARN

  • AWS_HOSTED_ZONE_IDAWS Route53 hosted zone ID

    AWS Route53 hosted zone ID

    values: Zone ID

  • AWS_REGIONAWS region for Route53

    AWS region for Route53

    values: AWS region

  • AWS_SECRET_ACCESS_KEYAWS secret access key for Route53

    AWS secret access key for Route53

    values: Secret key

  • BOOTSTRAPSComma-separated relay API URLs to seed discovery from

    Comma-separated relay API URLs to seed discovery from

    values: Comma-separated URLs

  • CACHE_ENABLEDtrueEnable origin-opted-in cache admission

    Enable origin-opted-in cache admission

    values: true, false

  • CACHE_MAX_BYTES1073741824Relay payload bytes including staging and pinned evictions

    Relay payload bytes including staging and pinned evictions

    values: Positive integer

  • CACHE_MAX_TTL24hMaximum offline TTL added to the bounded lease-liveness deadline

    Maximum offline TTL added to the bounded lease-liveness deadline

    values: Duration between 1s and 8760h

  • CLOUDFLARE_TOKENCloudflare DNS API token

    Cloudflare DNS API token

    values: API token

  • DISCOVERYfalseServe relay discovery endpoints and poll discovery peers

    Serve relay discovery endpoints and poll discovery peers

    values: true, false

  • EMBEDDED_DNS_PORT53Listen port for embedded authoritative DNS server

    Listen port for embedded authoritative DNS server

    values: Port number

  • ENS_GASLESS_ENABLEDfalseEnable ENS gasless DNS import automation

    Enable ENS gasless DNS import automation

    values: true, false

  • GCP_MANAGED_ZONEGoogle Cloud DNS managed zone name or numeric ID

    Google Cloud DNS managed zone name or numeric ID

    values: Zone name or ID

  • GCP_PROJECT_IDGoogle Cloud project ID for Cloud DNS automation

    Google Cloud project ID for Cloud DNS automation

    values: Project ID

  • GOOGLE_APPLICATION_CREDENTIALSPath to GCP service account key file

    Path to GCP service account key file

    values: File path

  • HETZNER_API_TOKENHetzner Cloud API token for DNS automation

    Hetzner Cloud API token for DNS automation

    values: API token

  • HTTP_REDIRECT_ADDR:80TCP listen address for HTTP redirect

    TCP listen address for HTTP redirect

    values: Address like :80 or 127.0.0.1:18080

  • HTTP_REDIRECT_ENABLEDfalseEnable the redirect-only listener

    Enable the redirect-only listener

    values: true, false

  • HTTP_REDIRECT_HSTSfalseEnable HSTS on redirect responses

    Enable HSTS on redirect responses

    values: true, false

  • IDENTITY_PATH/portal-certsDirectory for relay identity, policy state, and certificate material

    Directory for relay identity, policy state, and certificate material

    values: Any valid directory path

  • IVNP_CONFIGOptional IVNP RouterConfig JSON file; requires DISCOVERY=true

    Optional IVNP RouterConfig JSON file; requires DISCOVERY=true

    values: Path to JSON file

  • LANDING_PAGE_ENABLEDfalseInitial dashboard landing-page visibility

    Initial dashboard landing-page visibility

    values: true, false

  • LEGO_CA_CERTIFICATESPath to private CA certificate for ACME

    Path to private CA certificate for ACME

    values: File path

  • MAX_PORT40009Inclusive maximum port for UDP and raw TCP transports (0 = disabled)

    Inclusive maximum port for UDP and raw TCP transports (0 = disabled)

    values: Port number

  • MIN_PORT40000Inclusive minimum port for UDP and raw TCP transports (0 = disabled)

    Inclusive minimum port for UDP and raw TCP transports (0 = disabled)

    values: Port number

  • NJALLA_TOKENNjalla API token for DNS automation

    Njalla API token for DNS automation

    values: API token

  • PORTAL_URLhttps://localhostCanonical public HTTPS origin including its externally reachable port

    Canonical public HTTPS origin including its externally reachable port

    values: Any valid HTTPS URL

  • PPROF_ADDR127.0.0.1:6060pprof listen address

    pprof listen address

    values: Address

  • PPROF_ENABLEDfalseEnable pprof diagnostics

    Enable pprof diagnostics

    values: true, false

  • SNI_PORT443Local TCP SNI router listen port; follows PORTAL_URL port when unset

    Local TCP SNI router listen port; follows PORTAL_URL port when unset

    values: Any valid port number

  • TCP_ENABLEDfalseEnable raw TCP relay transport

    Enable raw TCP relay transport

    values: true, false

  • TRUSTED_PROXY_CIDRSExplicit trusted proxy CIDR allowlist for forwarded headers

    Explicit trusted proxy CIDR allowlist for forwarded headers

    values: Comma-separated CIDRs

  • TRUST_PROXY_HEADERSfalseTrust X-Forwarded-* and X-Real-IP headers from trusted proxies

    Trust X-Forwarded-* and X-Real-IP headers from trusted proxies

    values: true, false

  • UDP_ENABLEDfalseEnable UDP relay transport

    Enable UDP relay transport

    values: true, false

  • VULTR_API_KEYVultr API key for DNS automation

    Vultr API key for DNS automation

    values: API key

  • X402_ENABLEDfalseEnable relay-owned Sui x402 facilitator

    Enable relay-owned Sui x402 facilitator

    values: true, false

  • X402_PAY_TOPayment recipient address for relay-owned x402

    Payment recipient address for relay-owned x402

    values: Address

  • X402_TESTNETfalseUse Sui testnet for x402

    Use Sui testnet for x402

    values: true, false

portal-tunnel releases & version history

More in Networking

Rate this project

Click to rate — no account needed.

0 comments

Posting as guest
Loading comments…