Self-host passwordcockpit
1.4.1Team password manager with folder permissions and LDAP
- Stars
- 137
- Ports
- 8080 (HTTP web interface (when SSL disabled)), 4343 (HTTPS web interface (when SSL enabled))
- Requires
- MariaDB/MySQL
passwordcockpit/passwordcockpit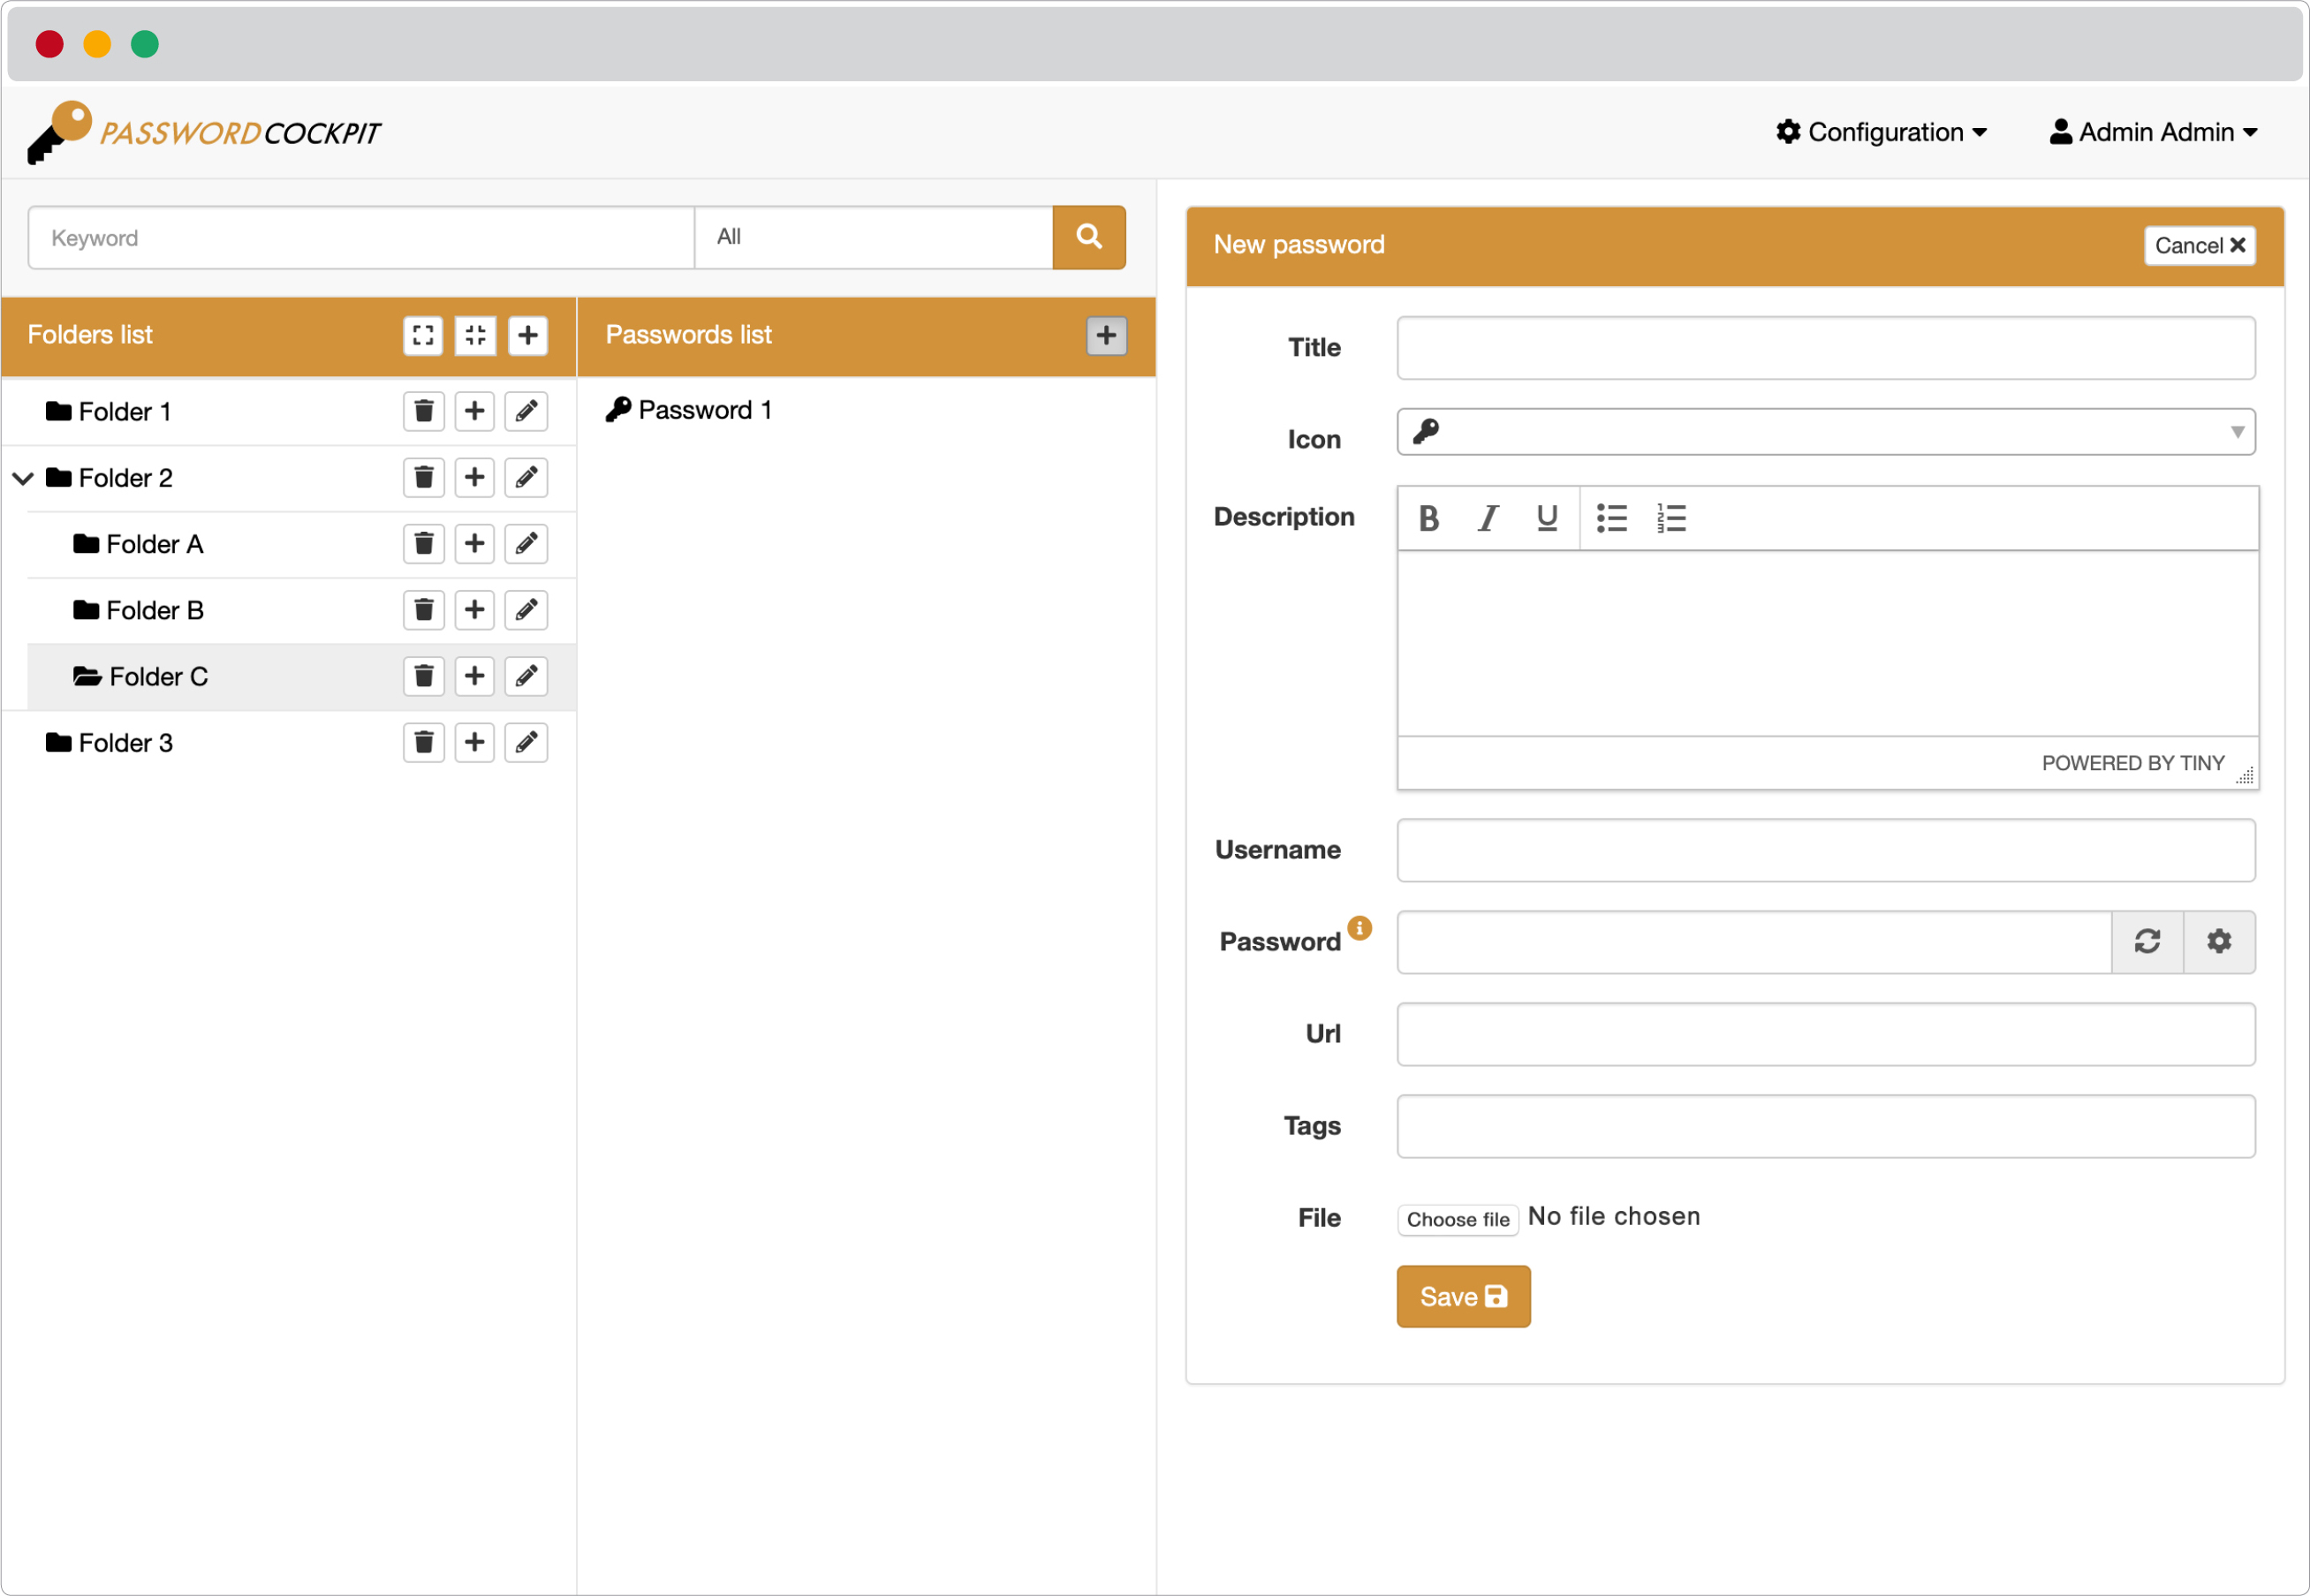
What is passwordcockpit?
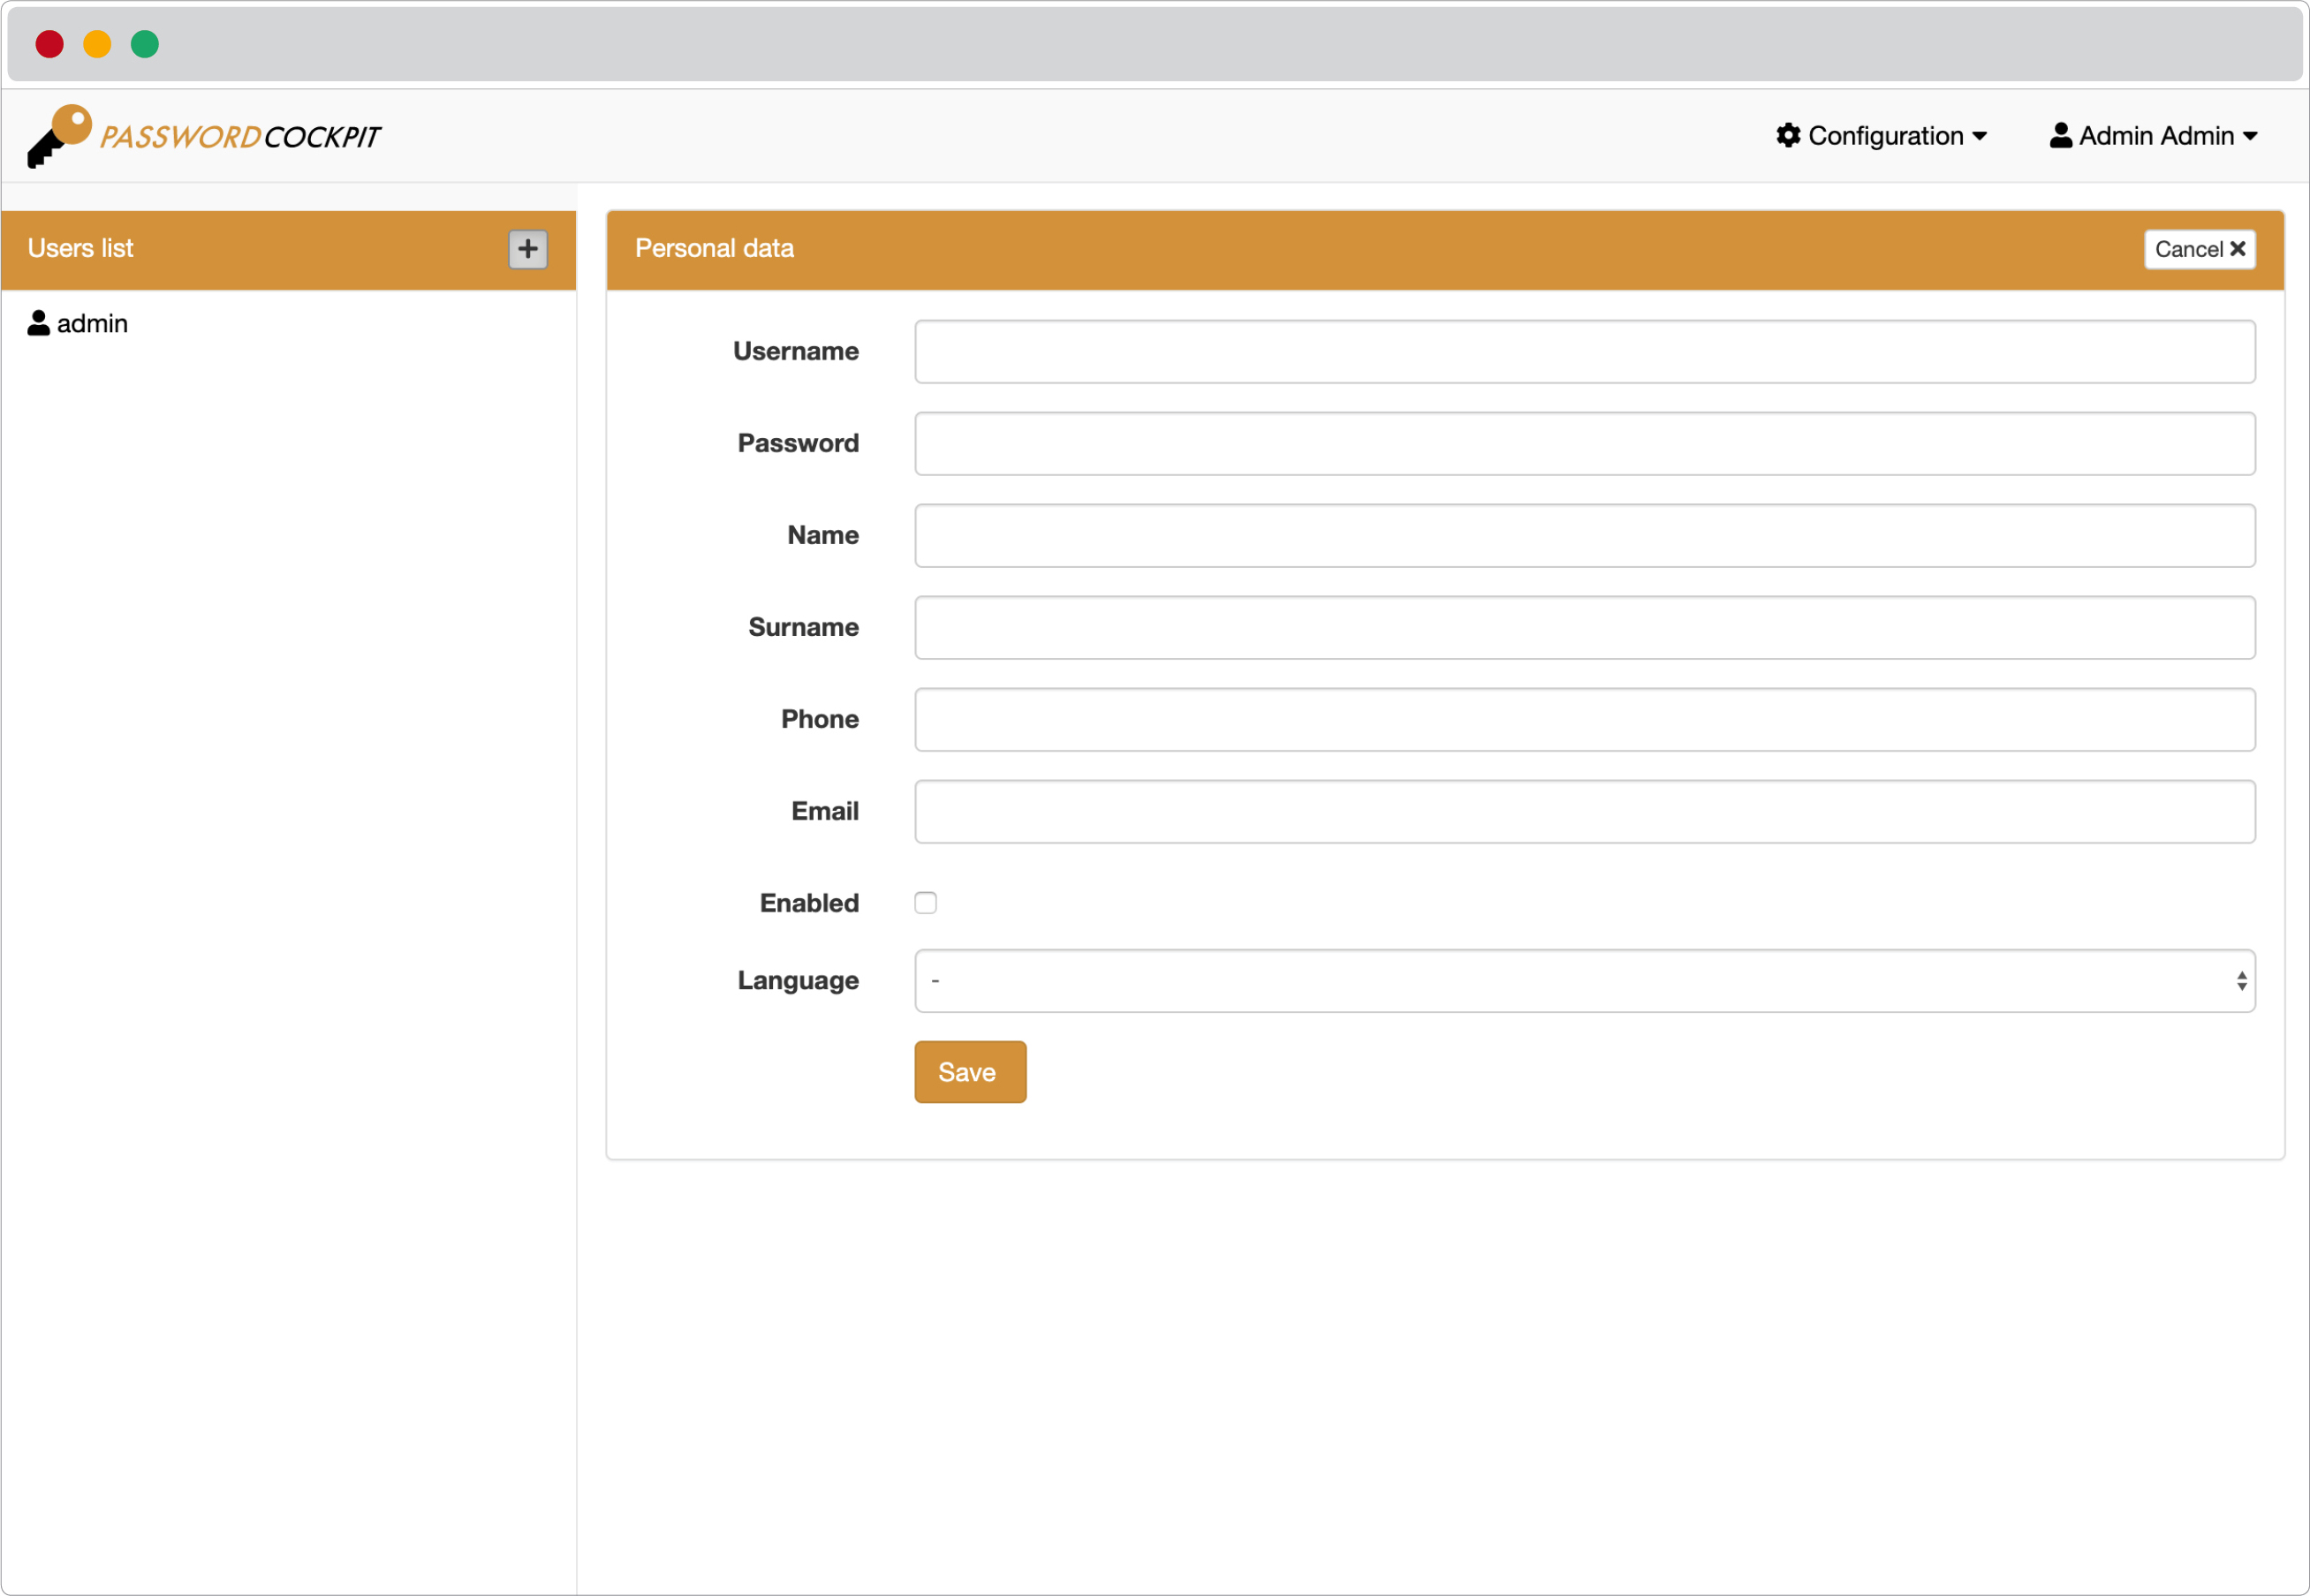
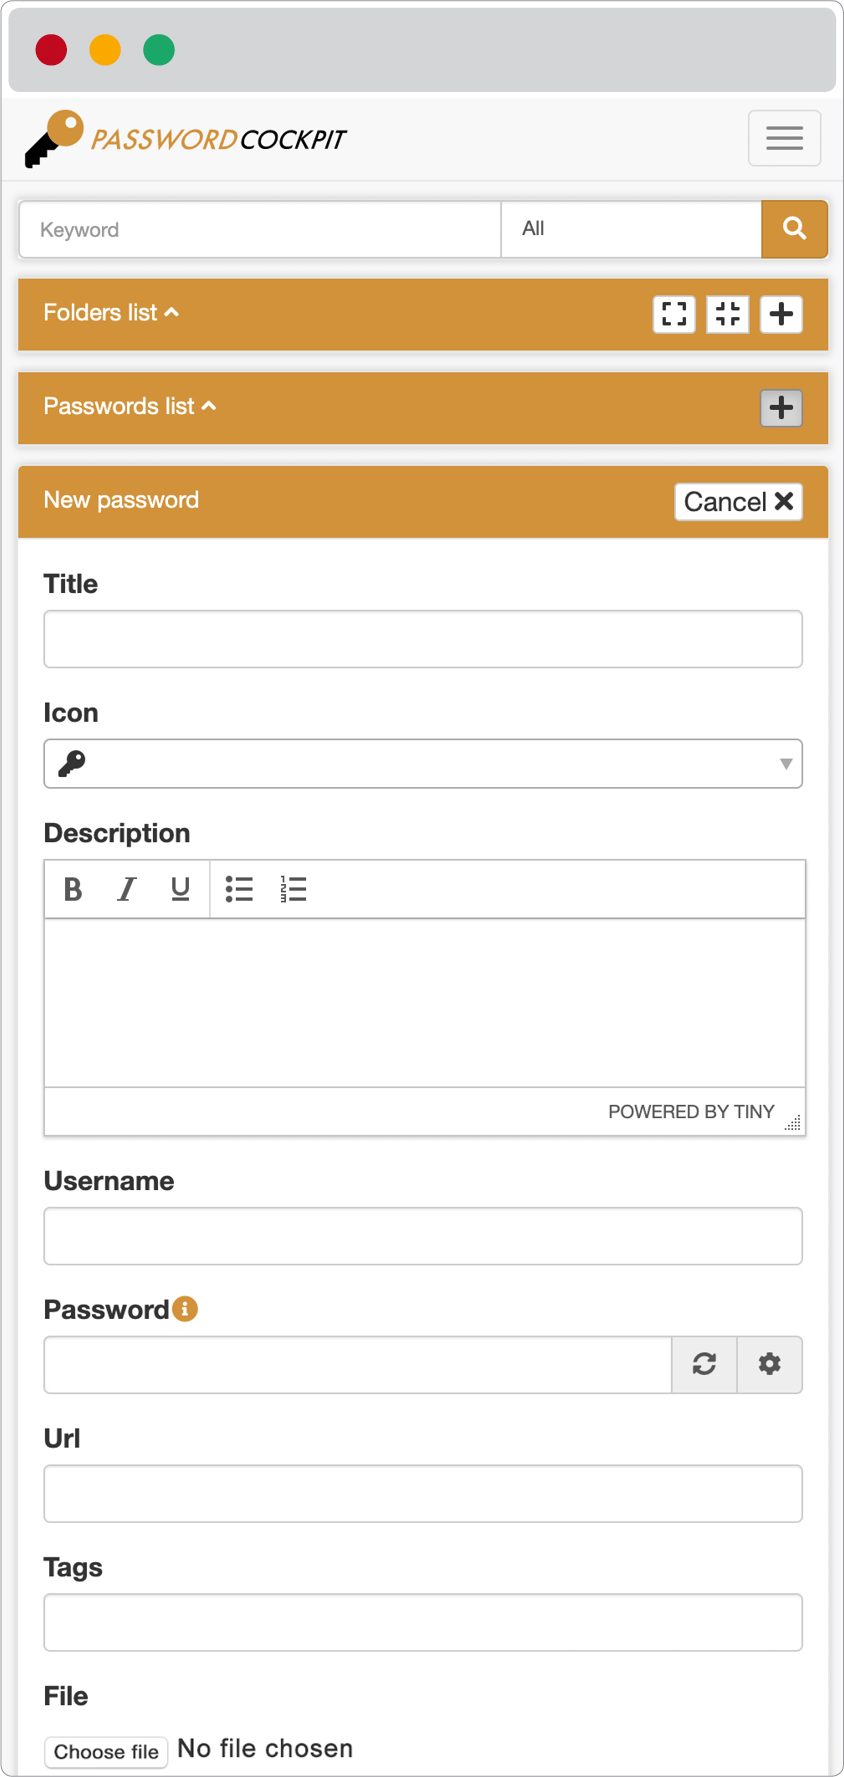
Passwordcockpit is a self-hosted password manager designed for team use. It provides a web interface where users can keep, share, and access passwords, certificates, and files. The application uses folder-based permissions with three access levels (no access, read, manage) and global permissions for user and folder management. Authentication supports both local database passwords and LDAP integration. Data is protected through three encryption layers: personal PIN encryption for individual passwords, SSL/TLS for data in transit, and database encryption for stored credentials and files. The backend is built with PHP (Mezzio/Laminas) and the frontend uses Ember.js with Bootstrap. It runs as a single Docker image with MariaDB/MySQL as the database. The REST API is documented with Swagger. The UI is responsive and works on mobile devices. Available in English, Italian, French, and German.
Should you self-host passwordcockpit?
passwordcockpit scores 47/100 on selfhost.directory (how scoring works) and ranks #14 of 28 in Password Managers. It has 137 GitHub stars.
It shipped 1 stable release in the past year. The latest, 1.4.1, came out on 22 October 2026.
Setup is moderate: expect some configuration beyond a single command. An official Docker image is available. It is BSD-3-Clause-licensed and written mostly in Dockerfile.
Its closest alternative on selfhost.directory is Vaultwarden (89/100, 69 809 stars). It scores higher overall, so compare the two before you pick. See passwordcockpit vs Vaultwarden side by side.
Features
- Bcrypt password hashing
- Custom SSL Certificates
- File attachments
- Folder-based permissions
- Global user permissions
- LDAP Authentication
- Multi-language Support
- Multi-layer encryption
- Non-root container
- PIN-based password encryption
- REST API with Swagger documentation
passwordcockpit README
More in Password Managers
 privateglue-publicPrivateGlue is a self-hosted, open-source web app linking devices, Markdown notes, and encrypted credentials for freelancers and homelabbers.
 pwmPWM is a self-hosted, open-source password self-service app for LDAP directories. Users reset passwords, unlock accounts, and manage credentials via web UI.
 quickblaze-encryptQuickBlaze Encrypt is a self-hosted, open-source PHP app for sending secrets via one-time view links that self-destruct after being read once.
 scrt.linkscrt.link is a self-hosted, open-source service for sharing passwords and files via end-to-end encrypted, ephemeral links that self-destruct after viewing.
 shaarkShaark is a self-hosted, open-source platform for web links, markdown posts, passwords, and photos with tagging, search, RSS, dark mode, and PWA.
 shareA self-hosted, open-source tool for sending passwords, notes, code, and big files through one-time encrypted links that vanish after use — no accounts needed.
 share-a-secretAn open-source, self-hosted tool for sharing sensitive data through encrypted links that expire after use.
 sharepwdSelf-hosted zero-knowledge secret sharing with client-side AES-256-GCM encryption, burn-after-reading, encrypted file sharing, CLI, and 5-layer anti-bot protection.
 ShhhShhh is a self-hosted, open-source Flask app for creating encrypted secrets that auto-delete after viewing or expiring, keeping sensitive data out of emails and chats.
 sysPasssysPass is a self-hosted, open-source PHP password manager with AES-256 encryption, 2FA, LDAP/AD integration, and JSON-RPC API for business and personal use.
 TeampassSelf-hosted, open-source team password vault on PHP/MySQL: folder and role access control, AES-256-GCM encryption, LDAP/OAuth2 SSO, TOTP and compliance reports.
 VaultwardenSelf-hosted, open-source Bitwarden-compatible password manager server written in Rust, offering nearly full API compatibility with official Bitwarden clients.
0 comments