Self-host open·kritt
v1.4.1AI vulnerability research platform
- Stars
- 2 378
- Ports
- 5173 (frontend web UI), 3002 (backend REST API), 8090 (executor view)
- Requires
- PostgreSQL
What is open·kritt?
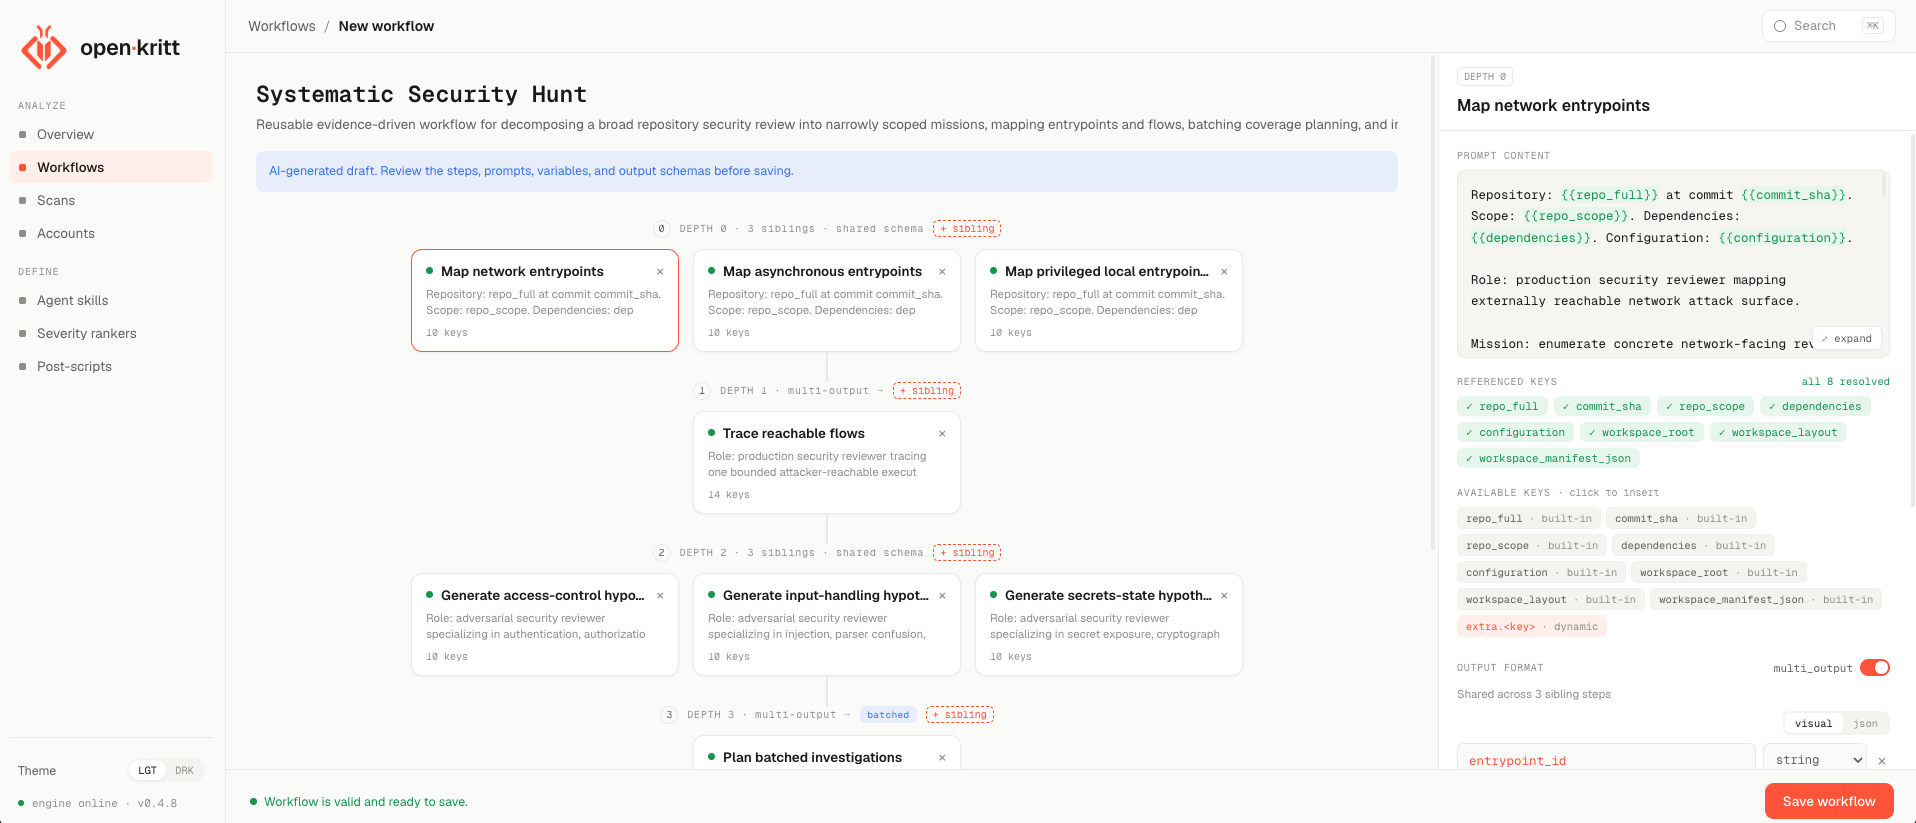
open·kritt is a self-hosted security research platform that breaks codebase analysis into small tasks run by AI agents at the same time. It serves security researchers and developers who want full command over their setup. The system creates reusable workflows from chained prompts, scans local or remote repositories using Codex, Anthropic's Claude Code, or xAI's Grok Build, verifies findings with post-scripts that confirm exploitability and build proofs of concept, exports complete scan results as ZIP archives with manifests, and ranks results through custom severity rules and automatic de-duplication. It runs via Docker Compose with a repository-local CLI (./kritt) that handles environment setup and model access configuration. The backend API has no authentication by default and must be protected by network isolation or a reverse proxy. The project uses the AGPL-3.0 license and is maintained by two developers.
Should you self-host open·kritt?
open·kritt scores 62/100 on selfhost.directory (how scoring works) and ranks #24 of 78 in Security. It has 2 378 GitHub stars.
It shipped 5 stable releases in the past year. The latest, v1.4.1, came out on 16 August 2026. New versions land roughly every 6 days.
Setup is moderate: expect some configuration beyond a single command. It is AGPL-3.0-licensed and written mostly in JavaScript.
Its closest alternative on selfhost.directory is pentagi (83/100, 32 648 stars). It scores higher overall, so compare the two before you pick. See open·kritt vs pentagi side by side.
Features
- AI agent orchestration
- Finding prioritization
- Finding verification
- Headless CLI
- Multiple AI provider support
- Repository scanning
- Scan result export
- Workflow Builder
open·kritt README
More in Security
 OpenNVRSelf-hosted NVR with open AI adapter contract — run any model on your hardware, air-gapped by default, with full audit trails and model fingerprinting.
- OpenSSH SFTP serverOpenSSH is the premier connectivity tool for remote login with the SSH protocol. It encrypts all traffic to eliminate eavesdropping, connection hijacking, and other attacks.
 openvpn_webpanel_managerSelf-hosted proprietary VPN panel managing OpenVPN, Cisco, L2TP, WireGuard, Sing-box with users, resellers, multi-node, REST API. Commercial license required.
 opnborgSelf-hosted daemon that backs up, monitors, and audits OPNsense firewalls via WebUI, with AI security audit, git history, and fleet config sync.
 OTSOTS is a self-hosted, open-source one-time secret sharing platform with client-side AES-256 encryption; server never sees plaintext, secrets auto-delete on first read.
 OTS - One Time SecretsOne-Time-Secret sharing platform with a symmetric 256bit AES encryption in the browser
 passwd-pageSelf-hosted, open-source zero-knowledge secret sharing tool with burn-after-read, file sharing, CLI, and MCP server for AI agents.
 Password Pusher🔐 Securely share sensitive information with automatic expiration & deletion after a set number of views or duration. Track who, what and when with full audit logs.
 PasteGuardSelf-hosted privacy proxy that masks personal data and secrets before requests reach AI providers like OpenAI and Anthropic.
 pentagiSelf-hosted, open-source multi-agent platform that runs autonomous penetration tests with professional security tools in Docker sandboxes and produces reports.
 permifyAn open-source authorization as a service inspired by Google Zanzibar, designed to build and manage fine-grained and scalable authorization systems for any application. — Permify is now part of FusionAuth 🎉
 phaseSelf-hosted secrets manager with end-to-end encryption for storing and deploying application secrets across environments.
0 comments